Virginia VCDPA: DSAR Privacy Portal
A Virginia resident visits your site, uses your content, and at some point decides to exercise the rights the law guarantees them. They want to know what you have on them. They want to correct an inaccuracy. They want you to stop using their data for ads.
This page covers one piece of the picture. For the full scope of the VCDPA — who must comply, the thresholds, the consumer rights and the penalties — start with our complete guide to the VCDPA and cookies.
What happens from that point on?
The Virginia Consumer Data Protection Act (VCDPA, Va. Code § 59.1-575 et seq.), in effect since January 1, 2023, defines exactly what must happen: the channel to receive the request, the deadline to respond, the appeal process in case of denial, and what happens when the business does not comply.
This article covers all of it.
DSAR stands for Data Subject Access Request. In practice, it is any formal request made by a consumer to exercise the rights the law grants them over their own data.
This includes asking to see what you collected, correcting incorrect information, requesting deletion of their data, asking for a portable copy, refusing the use of their data for targeted advertising, or contesting a decision you made about a previous request.
If you are already familiar with the GDPR, the DSAR framework is familiar. The VCDPA follows the same logic: the consumer needs a functional channel to exercise the rights the law guarantees.
Under Va. Code § 59.1-577 A, Virginia residents have five main rights:
The consumer can request confirmation that the business processes their data and obtain a copy of the personal data the business holds, under Va. Code § 59.1-577 A, 1.
The response must be provided in an accessible and comprehensible format.
The consumer can request correction of inaccuracies in personal data, taking into account the nature of the data and the purposes of processing, under Va. Code § 59.1-577 A, 2.
This covers any outdated, incomplete, or incorrect data. The business cannot ignore this request.
The consumer can request deletion of data they provided or that was obtained about them, under Va. Code § 59.1-577 A, 3.
There is a valid alternative in the VCDPA that does not exist in other laws: if the business obtained data from a source other than the consumer, it can fulfill the deletion request in two ways. It can delete the data outright, or it can retain the minimum data necessary to ensure the consumer's personal data remains deleted from active records and is not used for any other purpose (Va. Code § 59.1-577 B, 5).
The consumer can obtain a copy of their data in a portable and, where technically feasible, readily usable format, when processing is carried out by automated means, under Va. Code § 59.1-577 A, 4.
This makes it easier to transfer data to another controller.
The consumer can refuse the processing of their data for three specific purposes (Va. Code § 59.1-577 A, 5):
Targeted advertising (ads based on activities across non-affiliated websites over time).
Sale of personal data to third parties.
Profiling in furtherance of decisions that produce legal or similarly significant effects concerning the consumer (such as access to credit, housing, insurance, employment, or healthcare services).
Under Va. Code § 59.1-577 C, if the business denies a request, the consumer has the right to appeal the decision.
The appeal process must:
Be conspicuously available and easy to find.
Be comparable to the original request submission process.
Result in a written response within 60 days, including the decision and the reasoning.
If the appeal is denied, the business must inform the consumer about how to contact the Virginia Attorney General to file a complaint. Va. Code § 59.1-577 C specifies that, if available, the mechanism to contact the Attorney General should be online.
The VCDPA is direct on deadlines.
45 days from receipt of an authenticated request (Va. Code § 59.1-577 B, 1).
The deadline can be extended by another 45 days when reasonably necessary, considering complexity and volume of requests, as long as the consumer is notified within the initial period with the reason for the extension.
60 days to respond to appeals (Va. Code § 59.1-577 C).
These deadlines start when the request is received and authenticated. If additional information is needed to verify the consumer's identity, the deadline is paused until authentication is completed.
Va. Code § 59.1-577 B uses the term "receipt of the request." For deadline purposes, the request is received when the business has the minimum information needed to process it.
The identity verification process can influence this marker. If the business requests additional information to authenticate the consumer, the deadline is paused until authentication is completed, under Va. Code § 59.1-577 B, 4.
This is why the verification process must be agile, proportionate to the type of data involved, and clearly described in the submission channel.
Under Va. Code § 59.1-578 E, the controller must establish and describe in the Privacy Policy at least one secure and reliable means for consumers to submit rights requests.
This means must:
Consider how consumers normally interact with the controller.
Ensure secure and reliable communication.
Allow the controller to authenticate the consumer's identity.
Not require the consumer to create a new account. The business may require use of an existing account, but cannot force the user to register a new one just to exercise a legal right.
A well-structured Privacy Portal offers:
A request submission form with clear categories (access, correction, deletion, portability, opt-out).
A proportionate and non-discriminatory identity verification process.
Automatic receipt confirmation with a tracking reference number.
A log of each request, action taken, and response sent.
An appeal channel for denied cases.
The cookie consent on the site and the Privacy Portal must be integrated so that consumer preferences are reflected in real time in the business's operational systems.
The VCDPA requires the controller to authenticate the consumer's identity using commercially reasonable efforts, under Va. Code § 59.1-577 B, 4.
If authentication is not possible with commercially reasonable efforts, the business is not required to fulfill the request, but may ask for additional information that is reasonably necessary.
In practice, this means:
For low-risk data: an email confirmation may be sufficient.
For sensitive data or higher-risk situations: a second verification factor may be justified.
What is never acceptable: requiring physical ID documents for access to simple browsing data, creating deliberately burdensome processes to discourage requests, or denying requests based on impossible authentication when simpler methods are available.
Under Va. Code § 59.1-577 B, 3, request processing is free of charge up to twice per year per consumer.
This is an important point of difference from other state laws. The NHDPA, for example, provides free service only once per year. The VCDPA guarantees twice.
From the third request within the same 12-month period, the business may charge a reasonable fee or decline if the request is manifestly unfounded, excessive, or repetitive. The burden of demonstrating the excessive nature lies with the business.
Receive and authenticate the data subject.
Locate all personal data the business holds about this consumer across all systems.
Prepare a copy in a readable and accessible format.
Include in the response: categories of data, purposes of processing, third parties with whom the data was shared.
Send the response within the 45-day deadline.
An up-to-date data inventory is what makes this process viable at scale.
Receive and authenticate.
Identify which data is inaccurate and in which systems it is stored.
Correct in primary systems and, where applicable, notify third parties that received the data so they can also make the correction on their side.
Confirm to the consumer that the correction was made.
Receive and authenticate.
Check whether a legal exception exists that allows retaining the data (legal obligation, judicial defense, protected purpose).
If no exception: delete from active systems. For data obtained from third parties, there is the option of retaining the minimum necessary to ensure the data remains deleted from active records (Va. Code § 59.1-577 B, 5).
Notify third parties that received the data to also delete it where applicable.
Confirm to the consumer what was deleted and, if any partial retention is justified, explain the legal basis.
Receive and authenticate.
Generate a file with the consumer's data in a portable and machine-readable format, such as JSON or CSV.
Deliver it to the consumer securely within the deadline.
The opt-out of targeted advertising, data sale, or profiling with significant effects must result in the effective cessation of processing for those purposes.
The VCDPA does not specify a separate cessation deadline, unlike the NHDPA which has a specific 15-day period. The legal standard is "without undue delay" within the general 45-day response period. In practice, well-configured systems process opt-outs in real time or within a few hours.
A consent management platform integrated with the business's systems automates this workflow.
The business may deny a request when:
It cannot authenticate the consumer's identity with commercially reasonable efforts.
The request is manifestly unfounded or excessive.
A legal exception justifies continued processing or retention.
In all cases, the denial must be communicated to the consumer within the 45-day deadline, with:
The reason for the denial clearly stated.
Instructions on how to appeal the decision (Va. Code § 59.1-577 B, 2).
The appeal process must result in a written response within 60 days. If the appeal is also denied, the consumer must be informed about how to contact the Virginia Attorney General.
Va. Code § 59.1-578 A, 4 expressly prohibits businesses from discriminating against consumers who exercise their rights. This includes denying products or services, charging different prices, or offering lower quality.
The exception: voluntary loyalty, rewards, premium features, discount, or club card programs that offer benefits in exchange for data use are permitted, provided the consumer participates voluntarily.
Va. Code § 59.1-578 F prohibits processing data of known children under 13 for targeted advertising, data sale, or profiling with significant effects.
For social media platforms, starting January 2026, protection extends to minors under 16, with a 1-hour daily usage limit (Va. Code § 59.1-577.1).
If your portal receives requests from users in these age ranges, the process must have a differentiated flow.
Every processed request must be documented. This includes:
Date and time of receipt.
Type of request.
Authentication process performed.
Action taken (fulfilled, denied, or alternative adopted).
Date and form of response to the consumer.
In case of denial: recorded justification.
In case of appeal: complete history and final decision.
This documentation is what protects the business in the event of an Attorney General investigation. Without records, there is no way to demonstrate that processes were completed within the required deadlines.
Before initiating any action, the Attorney General must send notice with 30 days for the business to cure the violation (Va. Code § 59.1-584 B). If the business cures and provides a written correction statement, no action is initiated.
Businesses without a structured DSAR process have great difficulty correcting in 30 days what should have been implemented from the start. The cure period is a guarantee, not a compliance strategy.
If the violation continues, penalties can reach US$ 7,500 per violation, with each consumer whose right was violated potentially counting as a separate violation.
AdOpt logs every consent and opt-out interaction with a timestamp and unique identifier. When the consumer opts out of targeted advertising through the Privacy Portal, the system automatically updates cookie and tracker triggers.
AdOpt's auditable log serves as evidence that processes were completed as required by the VCDPA. And when legislation changes, the platform updates automatically.
Over 60,000 websites already run with AdOpt.
Privacy is not a banner. It is a position.
Want to build a Privacy Portal for your site that complies with the VCDPA? Talk to our team.
Request submission channel without requiring creation of a new account (Va. Code § 59.1-578 E).
Coverage of all 5 rights guaranteed by the VCDPA: access, correction, deletion, portability, and opt-out.
Conspicuously available appeal process comparable to the original submission channel (Va. Code § 59.1-577 C).
45-day response deadline, with the option to extend by another 45 days with notification (Va. Code § 59.1-577 B, 1).
60-day deadline to respond to appeals (Va. Code § 59.1-577 C).
Commercially reasonable identity authentication process (Va. Code § 59.1-577 B, 4).
Free service up to twice per year per consumer (Va. Code § 59.1-577 B, 3).
Documented record of each request, action taken, and response sent.
Information about how to contact the Attorney General in case of a denied appeal (Va. Code § 59.1-577 C).
Non-discrimination protection for consumers exercising their rights (Va. Code § 59.1-578 A, 4).
Differentiated treatment for known children under 13 (Va. Code § 59.1-578 F).
Notification to third parties where applicable for deletion or correction of shared data.
| Request type | Response deadline | Extension possible |
|---|---|---|
| Access, correction, deletion, portability | 45 days | +45 days with notification |
| Opt-out (advertising, sale, profiling) | 45 days | +45 days with notification |
| Appeal of a decision | 60 days | Not specified |
| Cure period for violations | 30 days guaranteed | No extension |
1. Does the VCDPA require a dedicated Privacy Portal?
Not by name. Va. Code § 59.1-578 E requires the controller to establish and describe in the Privacy Policy at least one secure and reliable means for submitting requests. A dedicated Privacy Portal is the most organized way to meet this requirement, but a well-structured contact form or a monitored email address can also fulfill the obligation, as long as they meet the security and reliability criteria.
2. Does the VCDPA have a specific deadline to cease processing after an opt-out?
Not in the same way as the NHDPA, which specifies 15 days. The VCDPA uses the criterion "without undue delay" for the general response, with a maximum of 45 days (Va. Code § 59.1-577 B, 1). In practice, for targeted advertising opt-outs, the expectation is that cessation is processed with the greatest technically reasonable agility, within the formal response deadline.
3. How many times per year must the business process DSARs free of charge?
Twice per year per consumer, under Va. Code § 59.1-577 B, 3. From the third request within the same 12-month period, the business may charge a reasonable fee or decline if the request is manifestly unfounded, excessive, or repetitive. The burden of proving the excessive nature lies with the business.
4. What happens if the business does not have a DSAR process when it receives an Attorney General notice?
The Attorney General sends notice with 30 days to cure (Va. Code § 59.1-584 B). If the business fails to implement the process within the deadline or breaches the written correction statement provided, the AG may seek penalties of up to US$ 7,500 per violation. Each consumer whose right was violated can be a separate violation, which quickly escalates the financial exposure.
5. How does the VCDPA handle data of consumers obtained from third parties in the context of a deletion request?
Va. Code § 59.1-577 B, 5 offers a specific alternative for this case. A business that obtained data from a source other than the consumer may fulfill the deletion request in two ways: by deleting the data outright, or by retaining the minimum data necessary to ensure the consumer's personal data remains deleted from active records and is not used for any purpose other than maintaining that deletion. This alternative does not exist in the NHDPA or in some other US state privacy laws.
Ready to build a Privacy Portal for your site that complies with the VCDPA? Talk to our team.
Virginia VCDPA compliance rests on documents that need to agree with each other: the cookies policy, which declares every tracker and its purpose; the privacy policy, which explains what you do with the data.
Tags
Related posts
Florida FDBR and Cookies: All You Need to Know
Everything you need to know about the Florida Digital Bill of Rights (FDBR): who must comply, the $1 billion threshold, 7 consumer rights, FIPA vs FDBR explained, penalties, and cookies.
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.

IOWA ICDPA and Cookies: All you need to Know
Iowa ICDPA explained: the longest response deadline of all US state privacy laws (90 days), 90-day cure period, opt-out for sensitive data, limited deletion scope, no right to correct, and how it compares to UCPA, VCDPA, and OCPA.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!

Montana MTCDPA: Privacy Policy
Learn what your MTCDPA Privacy Policy must include after Montana's SB 297 amendments from the conspicuous "privacy" hyperlink and last-updated date requirements to sale disclosures, minor protections, and how to keep your notice operationally aligned with your stack.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

Cookies and the TDPSA
If your website uses cookies and serves users in Texas, the Texas Data Privacy and Security Act (TDPSA) applies to you. This article breaks down exactly how cookies are treated under the law—and what your business must do to remain compliant and build user trust.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.

Cross-Domain Cookie Consent: One Choice, Several Sites
Cross-domain cookie consent lets one visitor choice apply to several sites. See when sharing is valid, how tags read it and what to test before you launch.
Colorado CPA and Cookies: All You Need to Know
The Colorado Consumer Privacy Act went into effect July 1, 2023 (CPA). CPA is a vital piece of legislation designed to protect the privacy of residents in Colorado. Understanding its requirements is essential for any business operating in the state. This act is all about giving control back to the consumers regarding their personal data. But what does this mean for you and your business, especially when it comes to managing cookies on your website?
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

Canada PIPEDA: Privacy Policy
How to write a PIPEDA privacy policy: what the ten principles require you to disclose, what to add for Quebec, and a checklist before you publish.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.

Global Privacy Control (GPC) Explained: What It Is and Who Has to Honor It
Global Privacy Control (GPC) is a browser opt-out signal. Learn how it works, which US states require you to honor it, and how to test your site.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.
California CCPA and Cookies: All You Need to Know
Everything about the California CCPA and CPRA: who must comply, the $25M threshold, 7 consumer rights, CCPA vs CPRA explained, the Do Not Sell link, CPPA enforcement, and cookies.
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.
LGPD: An Opportunity for Digital Marketing Agencies!
Have you ever thought that your marketing agency could find a great business opportunity in LGPD? Well, unlike what many think, it brings changes that can accelerate the demand for the services of these companies.
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Axeptio acquires Brazil's AdOpt, expanding global reach in consent management and LGPD compliance.
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

Consent Management Across Countries: How One CMP Serves Every Market
Consent management across countries: how one CMP applies the right rules to each visitor, passes the choice to Google and Meta, and honors GPC.
Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA
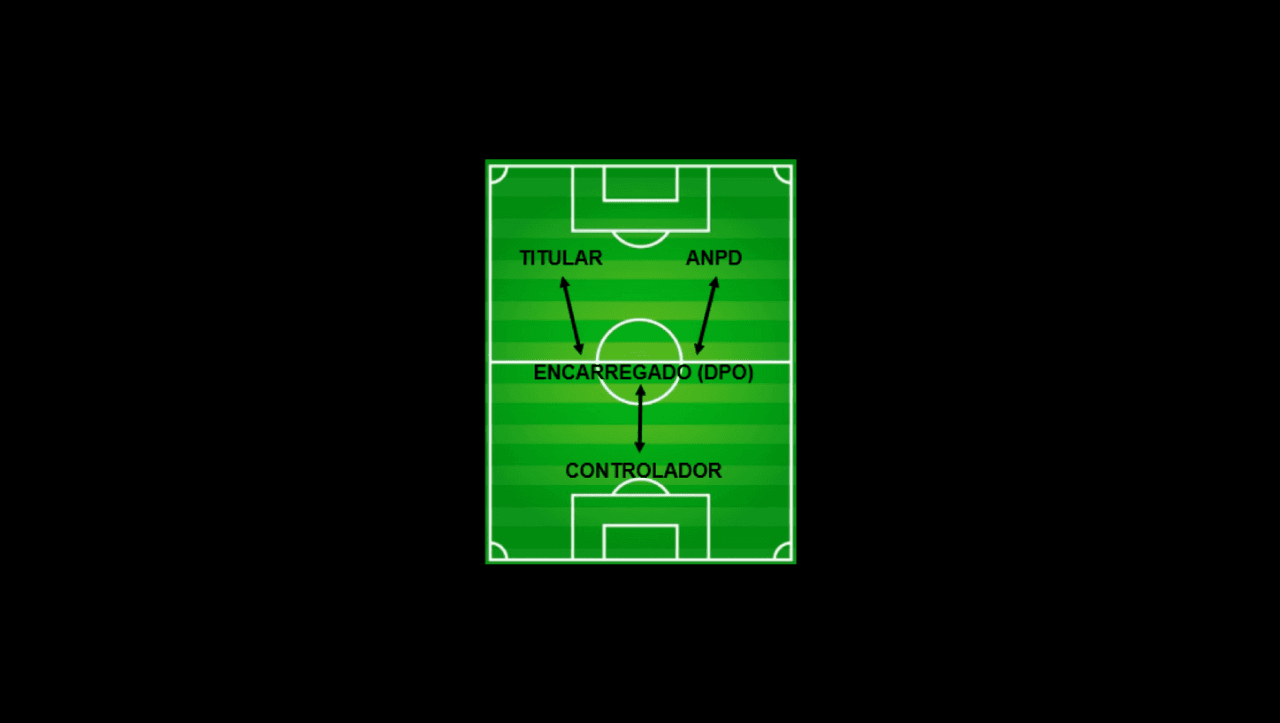
Responsibilities of a data protection officer.
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack.
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Utah UCPA: Privacy Policy
What the Utah UCPA requires from your Privacy Policy: five mandatory elements, opt-out model for sensitive data, no retention periods required, no active contact channel mandate, and the guaranteed 30-day cure period.

Canada PIPEDA and Cookies: All You Need to Know
PIPEDA is Canada's federal private-sector privacy law. See when it reaches your website, what it requires for cookies, and how to prove consent.

How to Choose a CMP (Consent Management Platform)?
Using a CMP (Consent Management Platform) is a great way to make efforts to adapt to new privacy regulations like GDPR, LGPD, DPDPA, CCPA and more...
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

Canada PIPEDA: Cookies Policy
What a PIPEDA cookie policy must say: purposes, third parties, opt-out, retention and Quebec rules. Plus a checklist to write yours.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.

5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.
Explore AdOpt
Autor
João Bruno
26 May 2026
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


