Responsibilities of a data protection officer.
Since the sanction of the LGPD in August 2018, through the approval of Provisional Measure No. 869/2018, until the conversion of the MP into law (Law No. 13.853/2019), the Data Protection Officer (DPO) role has gone through some twists and turns, such as the possibility of the DPO being an individual or legal entity, and the requirement of having regulatory legal knowledge.
Therefore, this brief article aims to provide some clarification regarding this crucial role in the context of data protection. Job vacancies have indeed arisen, but along with them, the responsibility and demands of the market!
In the definition of Article 5, item VIII, of the LGPD, the DPO is the "person appointed by the controller and operator to act as a channel of communication between the controller, data subjects, and the National Data Protection Authority (ANPD)."
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack. Visually, we have:
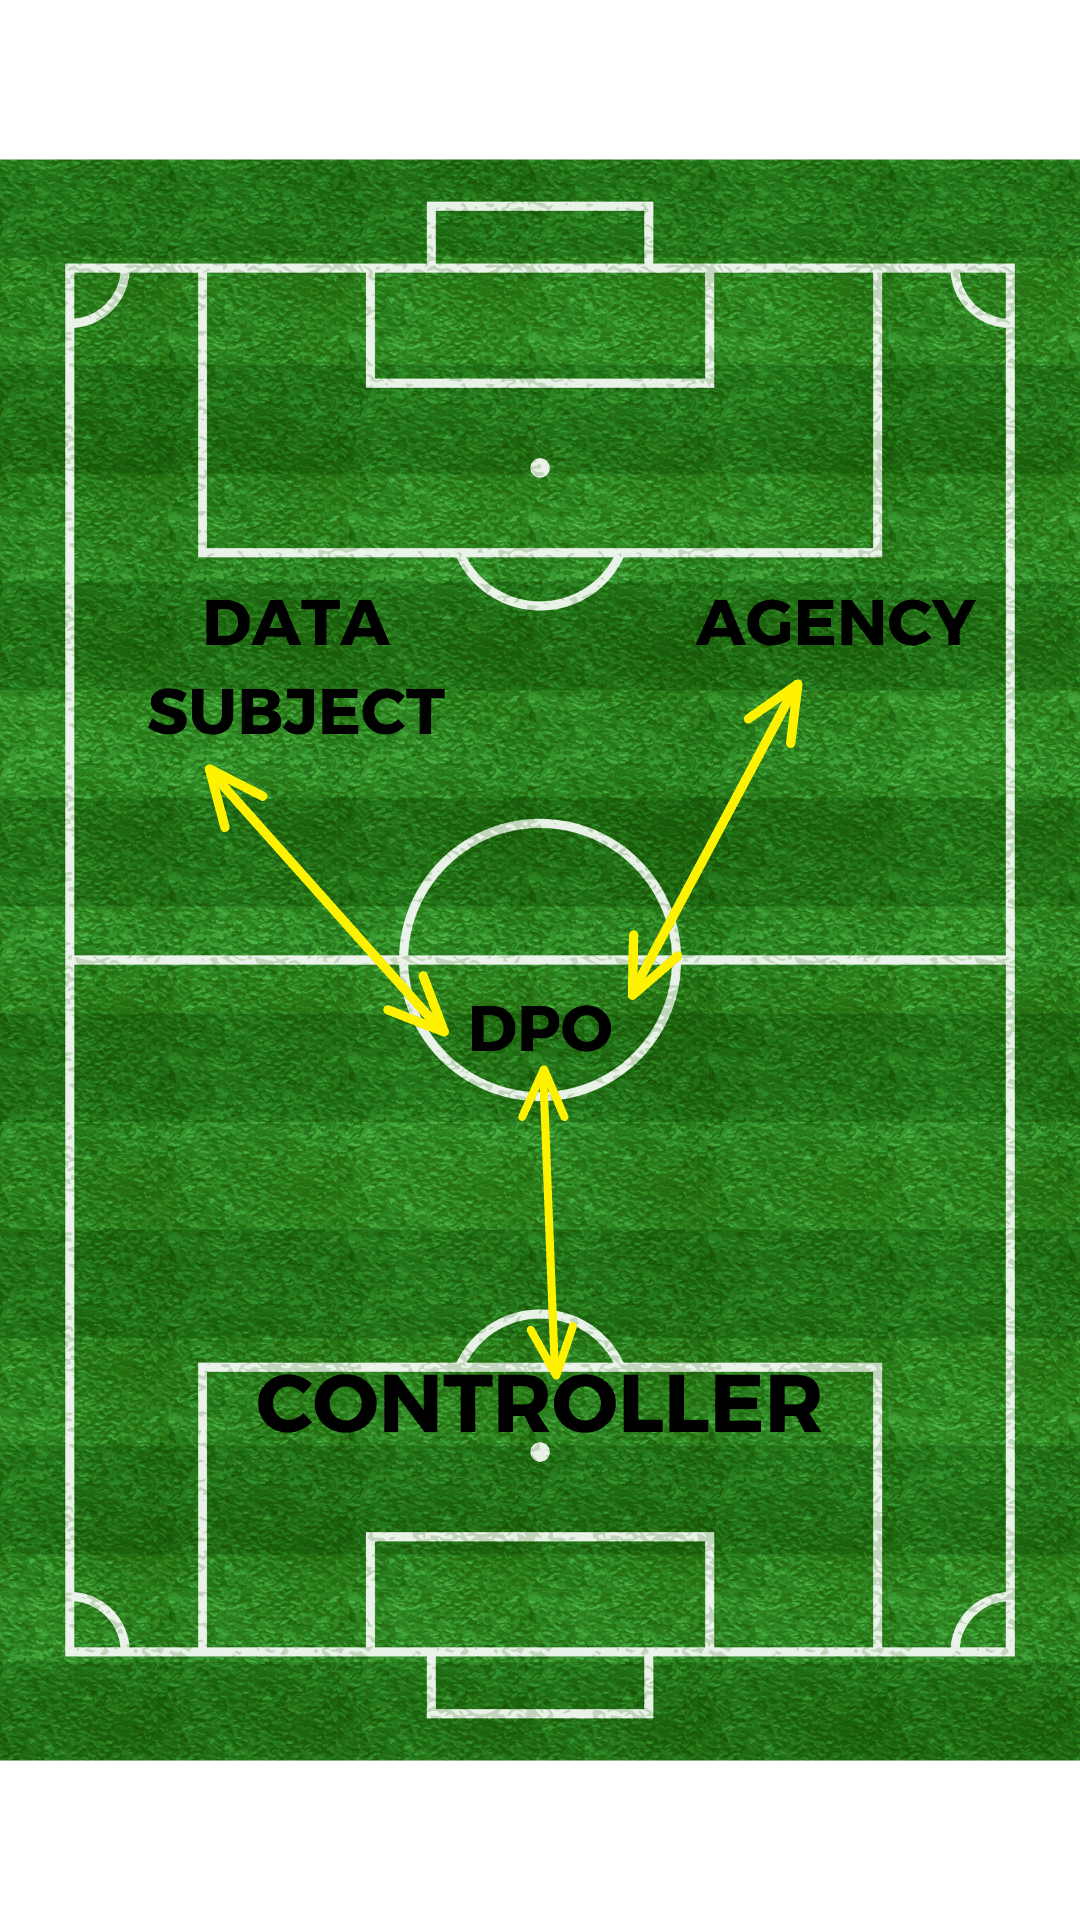
Thus, the DPO is the figure responsible for mediating the dialogue between the controller and the data subject or between the controller and the ANPD, accommodating their needs and interests.
Among their various responsibilities, all outlined in Article 41, § 2 of the LGPD, the DPO's activities consist of:
_I - accepting complaints and communications from data subjects, providing explanations, and taking action;
II - receiving communications from the national authority and taking action;
III - guiding employees and contractors of the entity regarding practices to be taken regarding the protection of personal data; and
IV - performing other duties determined by the controller or established in complementary regulations._
To fulfill these responsibilities, the DPO must master data mapping techniques, identifying all possible sources of collection, as well as controlling the data's lifecycle, i.e., how it will be stored and used, with whom it will be shared, when and how it will be deleted.
Another fundamental aspect for the DPO to truly fulfill the role that the LGPD proposes is autonomy in decision-making power and the exercise of oversight of internal company processes. Naturally, as a professional hired by a particular company to act according to its interests, the DPO will have a degree of subjection to the guidelines of their employer. However, this should not compromise their position as an intermediary between the data subject and the ANPD.
In conclusion, it is worth considering that although the current wording of the LGPD no longer requires the DPO to have regulatory legal knowledge, knowledge and, above all, mastery of the LGPD and other applicable regulations in the context of personal data protection are essential for the effective performance of the DPO's functions.
This is especially true because the LGPD should not be analyzed in isolation but always within the context of the market and the company's regulations seeking compliance.
Nevertheless, the growing concern of entrepreneurs regarding the LGPD is natural. After all, Brazil is an extremely complex country for entrepreneurship, and every new regulation brings uncertainty and instability to the game.
ABOUT THE AUTHOR:
Dânton Zanetti is a lawyer, founding partner of Zanetti, Oliveira & Machado Sociedade de Advogados (www.zomadv.com), working in the areas of Business Law, Contract Law, and Digital Law, with a Master's in privacy and data protection.
Tags
Related posts
Understand the meaning of the LGPD for your company
Surely you've already seen the predictions of fines and sanctions, processes. But, what does it mean to your company?

Fines in LGPD - What are they, amounts, and compliance deadlines
In this article, we will answer all your questions regarding fines under the LGPD (Brazil's General Data Protection Law).
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
Once upon a time, there was a company that got fined. - THE END
Sad, but this story is more real than you think. It all started with a "surprise" fine. Ever imagined everything crumbling around you? All because of a fine, an invoice that came "out of nowhere"? Your bank account, clients, your job, your car loan, marriage...
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.

The impact of privacy regulations, like LGPD, GPDR... on Inbound Marketing
Those who do not operate in accordance with LGPD's provisions risk facing penalties ranging from warnings to the suspension of their website, databases, and hefty fines.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).

Data Protection Officer and LGPD, a Solitary or Teamwork Job?
How do you deal with a profession that didn't even exist a few years ago and is now mandatory in companies? That's precisely the question that arises when we think of the figure of the Data Protection Officer or DPO.

Why Give Consent on Every Website I Visit?
Have you ever noticed that every time you sign up for a service to access information or register on a website for purchases, you need to give consent? If you're wondering why you have to give consent on every website you visit, you'll find the answer here.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.

AdOpt CMP
AdOpt CMP: Google-certified consent platform with prior blocking, granular choices, encrypted logs, and GTM/Consent Mode

New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.

Virginia VCDPA: Privacy Policy
What the Virginia VCDPA requires from your Privacy Policy: the 5 mandatory content categories, sensitive data obligations, targeted advertising disclosure, and the appeal process explained.
Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
California CCPA: Cookies Policy
What the California CCPA/CPRA requires from your Cookies Policy: Do Not Sell or Share link, GPC compliance, sale vs sharing distinction, sensitive PI opt-out, and annual updates.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.
Colorado CPA: DSAR Privacy Portal
How to handle DSARs under the Colorado CPA: 5 consumer rights, portability limited to twice per year, Universal Opt-Out Mechanism, 24-month record retention, and District Attorney enforcement.

Connecticut CTDPA: Cookies Policy
What the Connecticut CTDPA requires from your Cookies Policy: opt-out link, opt-out preference signal from January 2025, 15-day consent revocation, teen protections, and targeted advertising definition.
Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.
Oregon OCPA: DSAR Privacy Portal
Oregon OCPA DSAR guide: the L.O.C.K.E.D. rights, opt-out without authentication, derived data in deletion scope, 15-day revocation deadline, GPC from January 2026, and the elimination of the cure period.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.

Utah UCPA: DSAR and Privacy Portal
Utah UCPA DSAR guide: four consumer rights, limited deletion scope, no right to correct, no formal appeal process, no opt-out of profiling, 45-day deadline, and the guaranteed 30-day cure period.

IOWA ICDPA: Privacy Policy
What the Iowa ICDPA requires from your Privacy Policy: five mandatory elements, 90-day response deadline, 60-day appeal process, opt-out for sensitive data, no retention periods required, and the 90-day cure period.
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.
Explore AdOpt
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Google Consent Mode: Beginner to Advanced Guide.
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


