Understand the meaning of the LGPD for your company
You've probably already come across numerous predictions of fines and sanctions that LGPD brought along, right?
Now that we have the so-called "new" General Data Protection Law, LGPD, what's next?
Hold on!
Before adopting an alarmist or even pessimistic perspective on the law, it's essential to make it clear that the use of personal data (read: processing and treatment) is not prohibited by the law, but merely regulated by it.
As a result, you, as an entrepreneur or an expert in your field, can and should continue your work and strategies as a whole. However, you now need to understand how to adapt your business model to the regulations prescribed by the law for the use of such personal data.
So, what does the LGPD mean for your company?
My goal here is to provide you, as succinctly and practically as possible, with a compilation of key information that will serve as a guide amidst the questions and forks you'll encounter on your path to understanding and, above all, compliance!
After several years at the forefront of work and studies on data, marketing, and internet privacy, a confession is in order. We've genuinely seen it all. We've been in this market since the birth of predictive analysis concepts, and all the AdTechs that have emerged since then. We witnessed the rise and fall of Cambridge Analytica and its scandals and leaks, numerous analyses and documentaries, Wikileaks, Snowden, and so on.
Naturally, we followed the entire market with the emergence of GDPR, CCPA, and their derivatives worldwide, which now, here in Brazil, culminate in LGPD. For almost 8 years, we've been working daily on several of the pillars that the "Data-Driven Marketing" market is so familiar with today. - Building data models for performance metrics analysis,
- Sequential databases, non-relational databases, physical, cloud, and so many others that have passed through our hands.
- Numerous tracking tag characteristics, fingerprints, SDKs, etc. - Endless technology updates, privacy issues, rumors, and browsers with their third-party cookie blocking. - Various integrations with Ad servers, CRMs, email tools, DSPs, Cookie Syncs with DMPs, Data Providers, Credit Bureaus, etc. - Firewalls, Backdoors, Security Routines, DNS, etc.
In short, more than 200 million unique users mapped in our systems, and 40 thousand websites have passed through our network since 2015, when we created our first Tag and Cookie version.
All of this is to tell you that all this knowledge we've accumulated until today gives us one certainty. It's worthless to know all of this if:
1 – We don't promptly execute best work and security practices,
2 – We can't translate international theories into our local legislation and market realities.
3 – We don't demystify the need for infinite, extremely elaborate resources to start good work.
4 – If theory doesn't generate real benefits for clients and, consequently, sales for both sides.
Throughout 2019, we interviewed nearly 250 companies about LGPD and their perceptions of its impacts and challenges for compliance. Most of the difficulties listed at the time were: the difficulty of understanding the law, a lack of skilled labor, difficulties with managing new technologies, and, not least, the administration and collection of consent from data subjects.
Since then, we've had the same feeling: LGPD remains an enigma for most, and at the same time, we, who are a vital part of the market, have the opportunity to reinforce how seriously Privacy should be taken. Not just valued when lost but, in essence,** as an individual right of all citizens.**
Especially today, where it's impossible to ignore the elephant in the room, or rather, the increasing number of mobile phones and devices collecting text, audio, and video data in practically every household. Who hasn't felt like their phone is listening to them? Throw the first stone!
The fact is, all privacy regulations are here to stay!
Yes, we're on an irreversible path when it comes to data usage by our favorite gadgets. Therefore, it's crucial that we understand the value of Privacy while theoretically, we still have control. But more importantly, we need access to technologies that work in our favor, not just collecting data but also giving us freedom in the face of the numerous data collection instances we encounter daily.
Yes, before data collection, there's a choice made by a free citizen, which must be respected and informed clearly and transparently.
So, in the midst of all this data, services, endless questions, and technology tests, AdOpt was born.
These are years of study and practical applications aimed at minimizing the consequences that the marketing and advertising market has faced. Not just when GDPR came into effect in Europe and drastically reduced the revenue of major publishers but also due to the maturation of our local market - Brazilian, facing the numerous technologies we couldn't even test, thanks to our limited budgets.
AdOpt starts as a quick and practical way for all companies to communicate and collect consent from their visitors without risking destroying their metrics and engagement with yet another ugly notice that looks more like a Pay Wall, or shall we say - Cookie Wall?
In the entire roadmap of AdOpt and its evolution as a product, our goal is also to democratize access to information about the legislation and its applications so that we respect everyone's privacy! Again, the context in which AdOpt was born makes it impossible to ignore, given its immense importance in today's world.
From a commercial standpoint, we've come to the conclusion that the market lacks easily understandable positions, and above all, demystifying the interests of certain market segments concerning the new General Data Protection Law, LGPD. It's certain that lawyers, accountants, marketing agencies, IT professionals, and various other "experts" are eager to grab their share of the market. This is perfectly understandable because the law encompasses knowledge from various areas simultaneously. However, before any market advantage or class of workers, we at AdOpt believe that there are 2 principles that should always guide our interpretation of all this, in light of privacy; exalted by the numerous privacy laws worldwide.
Yes, freedom is of immeasurable value, and only those who lose it can truly describe the impact of its absence. Whether in access to information, the right to move freely, freedom of the press, or the simple right to be forgotten.
We are the generation that created memes, but also "cancel culture," fierce criticism of Fake News, banning some social networks, and more. Guided by the premise of valuing truth, sometimes we forget to measure the real impact of some unilateral mechanisms that end up overshadowing the true value of freedom.
LGPD, GDPR, CCPA, and many others are also mechanisms that help citizens maintain their freedom in the face of internet giants.
When this (the internet) "was all wild territory" and we had a handful of blogs and news portals, LGPD would never make sense. However, it was thanks to these internet anchors that the opportunity to monetize people's attention on certain pages was created! Without major publishers, we wouldn't have programmatic advertising and all the opportunities to automate the cash flow generated globally today, at the scale and proportion we experience.
Without programmatic advertising, we wouldn't have social media as we know them today. After all, as Mr. Zuckerberg would say.
"We Run Ads."
Perhaps this introduction has a touch of a "Manifesto" for you, as we emphasize the value of Privacy and Freedom, expressed in free access to information and, consequently, content production.
Here's another confession for you, dear reader. AdOpt today serves as a cookie notice, assisting as a CMP._ But you have no idea what lies ahead when we connect all these points above and provide you with access to the technologies we're designing!
The discussion isn't over yet, but I hope you've understood how passionate we are about this subject and want to guide you through it!
In our next chapter (article), I want to show you the foundation of understanding the law: The Legal Bases of LGPD, see you there!
Tags
Related posts

Understand the legal bases of the LGPD
At the beginning of everything are the legal bases of the LGPD, that is, the legal grounds (legitimate reasons) why companies not only can, but must access customer data in order to do their jobs well.

LGPD and Cookies all do you need to know?
In this article, you will have a great introduction to the topic, as well as various other variations that revolve around the subject: Cookies and LGPD.

Fines in LGPD - What are they, amounts, and compliance deadlines
In this article, we will answer all your questions regarding fines under the LGPD (Brazil's General Data Protection Law).

How to delete cookies and cache in Chrome and other browsers?
Tired of the ads from that site you visited following you around? Is your computer running slow when accessing a particular website? Want to delete all cookies from a specific service or site?

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!

Key Differences between LGPD and GDPR and the Impact on Internet Cookies
While both regulations share the goal of safeguarding individuals' rights regarding the processing of their personal data, there are some important differences between them. It is crucial to understand these distinctions and their implications, particularly in the context of internet cookies.
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.
What is the ideal privacy policy for your company?
Is there an ideal and _foolproof_ Privacy Policy? This is one of the most difficult questions to answer nowadays. Especially considering all the jurisprudence already established in Europe with the GDPR, the extensive history of cases, and the numerous tips we see in the market. Not to mention the judicial decisions that are already emerging in Brazil with the LGPD.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.
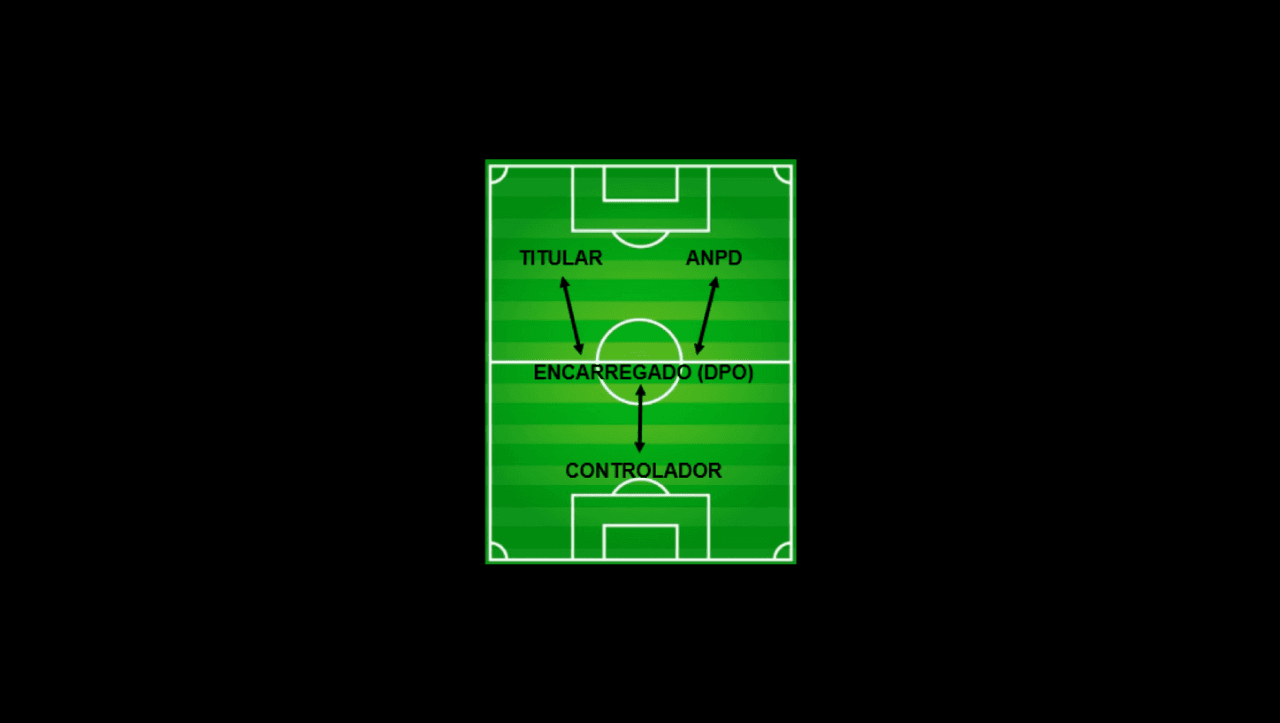
Responsibilities of a data protection officer.
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).

Data Protection Officer and LGPD, a Solitary or Teamwork Job?
How do you deal with a profession that didn't even exist a few years ago and is now mandatory in companies? That's precisely the question that arises when we think of the figure of the Data Protection Officer or DPO.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
LGPD & COOKIES - ANPD Releases "Guidance on Cookies and Personal Data Protection"
On October 18, 2022, the National Data Protection Authority (ANPD) released the "Guidance on Cookies and Personal Data Protection." Highly anticipated by professionals in the field, this document is of utmost importance as it examines various applicable legal scenarios and establishes the requirements to be observed in the case of cookie usage.
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.
5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.

AdOpt CMP
AdOpt CMP: Google-certified consent platform with prior blocking, granular choices, encrypted logs, and GTM/Consent Mode
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!

New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.

Virginia VCDPA: Privacy Policy
What the Virginia VCDPA requires from your Privacy Policy: the 5 mandatory content categories, sensitive data obligations, targeted advertising disclosure, and the appeal process explained.
Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
California CCPA: Cookies Policy
What the California CCPA/CPRA requires from your Cookies Policy: Do Not Sell or Share link, GPC compliance, sale vs sharing distinction, sensitive PI opt-out, and annual updates.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.
Colorado CPA: DSAR Privacy Portal
How to handle DSARs under the Colorado CPA: 5 consumer rights, portability limited to twice per year, Universal Opt-Out Mechanism, 24-month record retention, and District Attorney enforcement.

Connecticut CTDPA: Cookies Policy
What the Connecticut CTDPA requires from your Cookies Policy: opt-out link, opt-out preference signal from January 2025, 15-day consent revocation, teen protections, and targeted advertising definition.
Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.
Oregon OCPA: DSAR Privacy Portal
Oregon OCPA DSAR guide: the L.O.C.K.E.D. rights, opt-out without authentication, derived data in deletion scope, 15-day revocation deadline, GPC from January 2026, and the elimination of the cure period.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.

Utah UCPA: DSAR and Privacy Portal
Utah UCPA DSAR guide: four consumer rights, limited deletion scope, no right to correct, no formal appeal process, no opt-out of profiling, 45-day deadline, and the guaranteed 30-day cure period.
Explore AdOpt
Autor
João Bruno
31 May 2022
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Google Consent Mode: Beginner to Advanced Guide.
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


