The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.
A simple example would be the roles between a company and its marketing agency. In this case, the company would be the data controller and the agency the data processor because their functions are distinct in the chain of services and responsibilities.
For example, when the Data Subject goes to an e-commerce website to purchase a product, from their perspective, who are they entrusting their personal data to in order to make that purchase?
Can they know if the agency receives the lead and then enters it into the email marketing tool? No. Therefore, the e-commerce website becomes the data controller and the agency becomes the data processor. Each has their own role under the law, but all are co-responsible, in their respective functions, for the proper handling of the data of the Data Subjects.
Therefore, in your data mapping that we mentioned a few lines back, what is your role: data controller or data processor? Or, depending on your business model, both depending on the stage?
It is important for you to highlight this because, just as your responsibilities differ based on the role you perform, the way you handle a request for data deletion or data download is different. You may have the data on hand and the capability to deliver it to the Data Subjects.
However, it may also happen that you can only refer this power to the data controller, after all, you are just a link in the chain and do not have direct access to the data, but to some encryption that only provides you with anonymized visualization.
Other common examples where there are different roles but clear co-responsibility for the data and its use include:
Company <> Third-party Accounting Firm. Real Estate Company <> Third-party Brokers. Investment Fund <> Independent Agents. E-commerce Website <>Logistics companies and delivery services. Law firms <> Customer and employee qualification data.
In conclusion, it is clear the importance of an accurate listing of all data controllers and data processors within your company's data mapping. With this information in hand, it is advisable to link all parties involved in the process according to your privacy policy and terms of use.
In the future, we can discuss the obligations prescribed by the law.
However, you can also consult directly with your lawyer, especially if you have any legislation that supersedes the LGPD.
In our next article, we delve into the responsibilities of the Data Protection Officer or Data Controller.
See you there.
Knowing who is controller and who is processor starts with knowing what data flows where: see data mapping and data inventory. The next step is the legal basis for each processing activity.
Tags
Related posts
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.

Why Give Consent on Every Website I Visit?
Have you ever noticed that every time you sign up for a service to access information or register on a website for purchases, you need to give consent? If you're wondering why you have to give consent on every website you visit, you'll find the answer here.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.

What is the ideal privacy policy for your company?
Is there an ideal and _foolproof_ Privacy Policy? This is one of the most difficult questions to answer nowadays. Especially considering all the jurisprudence already established in Europe with the GDPR, the extensive history of cases, and the numerous tips we see in the market. Not to mention the judicial decisions that are already emerging in Brazil with the LGPD.

Key Differences between LGPD and GDPR and the Impact on Internet Cookies
While both regulations share the goal of safeguarding individuals' rights regarding the processing of their personal data, there are some important differences between them. It is crucial to understand these distinctions and their implications, particularly in the context of internet cookies.

Data Protection Officer and LGPD, a Solitary or Teamwork Job?
How do you deal with a profession that didn't even exist a few years ago and is now mandatory in companies? That's precisely the question that arises when we think of the figure of the Data Protection Officer or DPO.
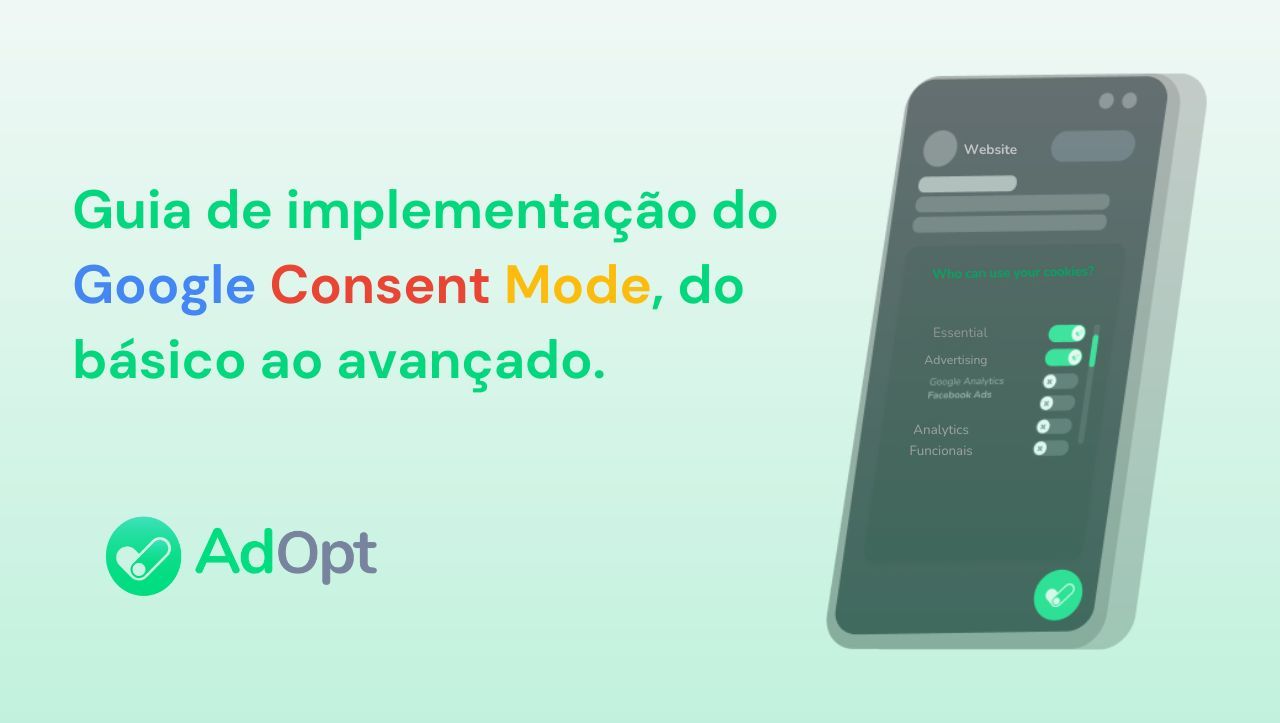
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.

IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.

5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.
Understand the legal bases of the LGPD
At the beginning of everything are the legal bases of the LGPD, that is, the legal grounds (legitimate reasons) why companies not only can, but must access customer data in order to do their jobs well.

AdOpt CMP
AdOpt CMP: Google-certified consent platform with prior blocking, granular choices, encrypted logs, and GTM/Consent Mode

LGPD and Cookies all do you need to know?
In this article, you will have a great introduction to the topic, as well as various other variations that revolve around the subject: Cookies and LGPD.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

Fines in LGPD - What are they, amounts, and compliance deadlines
In this article, we will answer all your questions regarding fines under the LGPD (Brazil's General Data Protection Law).

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Understand the meaning of the LGPD for your company
Surely you've already seen the predictions of fines and sanctions, processes. But, what does it mean to your company?
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?

California CPRA: Privacy Policy
What the California CPRA requires from your Privacy Policy: SPI category, two mandatory links, data retention periods, sharing disclosure, right to correct, GPC, and minor protections.
Responsibilities of a data protection officer.
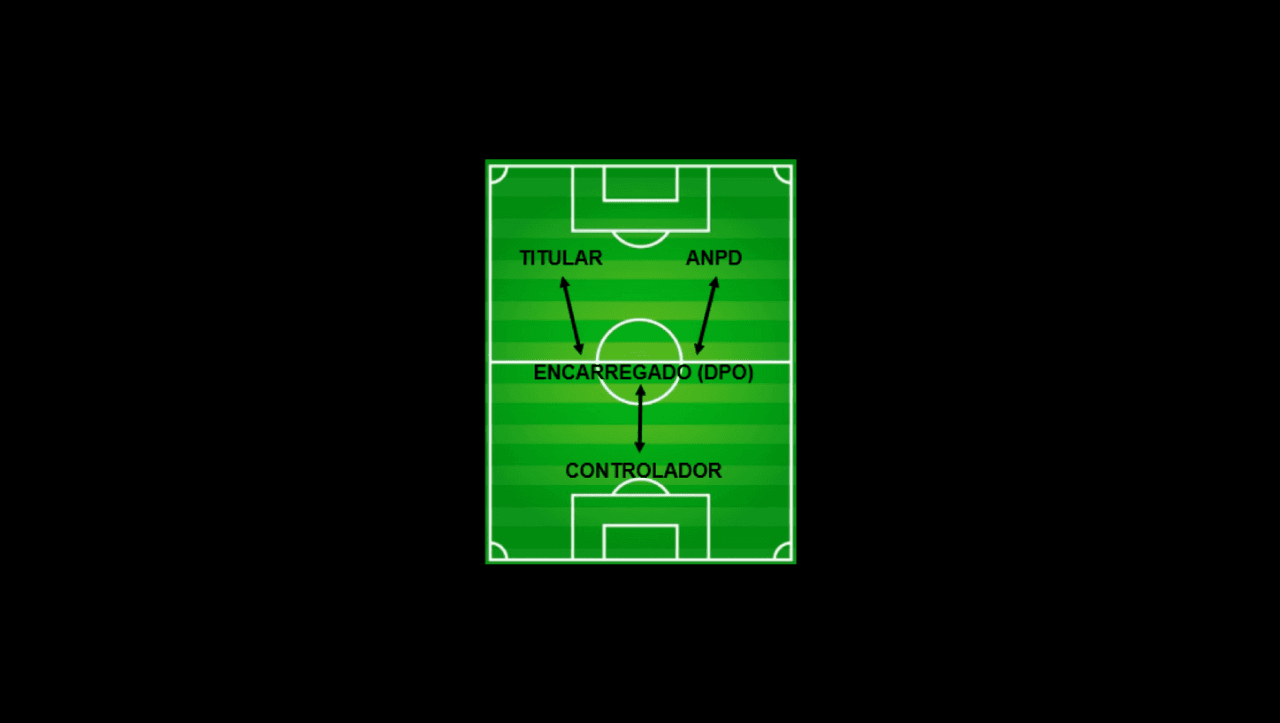
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack.
New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
LGPD & COOKIES - ANPD Releases "Guidance on Cookies and Personal Data Protection"
On October 18, 2022, the National Data Protection Authority (ANPD) released the "Guidance on Cookies and Personal Data Protection." Highly anticipated by professionals in the field, this document is of utmost importance as it examines various applicable legal scenarios and establishes the requirements to be observed in the case of cookie usage.

What are Terms of Use and their importance for the LGPD?
Ignoring Terms of Use and their significance within a website, particularly now with LGPD, is a common mistake that both consumers and website owners frequently commit.
Explore AdOpt
Autor
João Bruno
12 Sep 2023
AdOpt


Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Oregon OCPA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website


Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


