Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the GDPR of the European Union, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).
Due to its novelty and the importance of its role, many companies and organizations are opting for outsourcing this activity. But is it really a good idea? What are the risks and advantages?
Find the answers to these questions and get to know the Data Protection Officer and their responsibilities as per LGPD regulations.
The DPO is an individual or legal entity established within Data Protection Policies as one of the agents involved in the processing and use of data subjects' information. Thus, their role is of utmost importance.
They can be either an individual or a legal entity. However, they cannot correspond to a department or team within the company. After all, documents related to data collection and processing must specifically indicate who is responsible as the DPO.
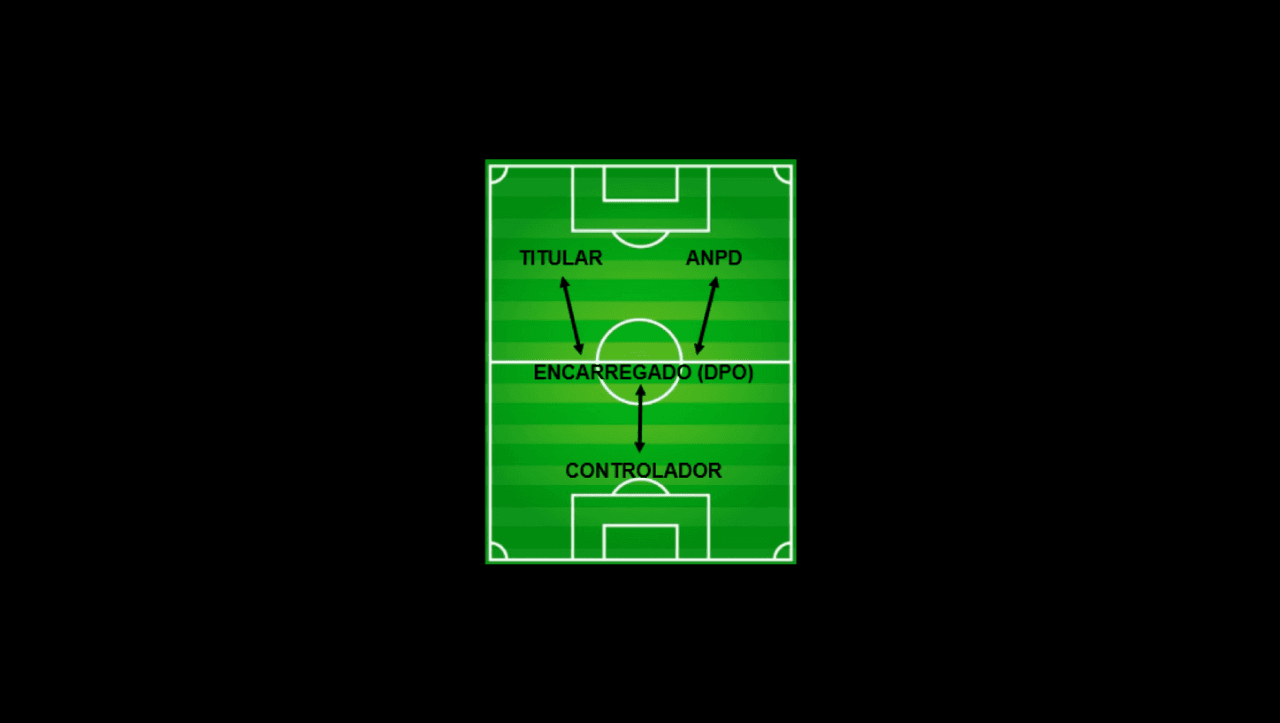
The DPO's functions lie in mediating the relationship between data subjects, the data processor, and the National Data Protection Authority (ANPD).
They do not necessarily make decisions regarding data and its use. However, they assist in following and complying with the guidelines imposed by the data controller and the General Data Protection Law. Another one of the DPO's responsibilities is to provide guidance to employees who have access to third-party data, instructing them on how to adhere to LGPD guidelines and the consents that have been granted.
### Their role is to educate, organize, and audit in accordance with ANPD regulations.
Some of the main activities that a DPO, whether outsourced or not, may perform include:
- Handling data subject complaints, providing clarifications, and taking necessary actions;
- Receiving communications from ANPD and taking appropriate actions;
- Handling consent revocations or changes in consent and taking appropriate measures;
- Ensuring the application of LGPD principles regarding personal data processing;
- Monitoring organizations' compliance with the General Data Protection Law, etc.
Thus, the DPO serves as an intermediary, mediating relationships and being one of the agents responsible for ensuring compliance with LGPD.
Anytime a company or organization desires, they can outsource these services. The law does not require the DPO to be an internal employee. In fact, it does not even require the DPO to be an individual.
Therefore, any self-employed professional or company that provides services in this area can offer services to other companies. This involves the establishment of a service provision or outsourcing contract.
In the case of hiring an external person as a DPO as a service (DPOaaS), a service provision contract is established directly with the professional.
On the other hand, when a company is hired, there is an outsourcing of the DPO. The entity determined as the DPO within the Privacy Policies is the legal entity.
It provides professionals who will perform the typical duties of a DPO. However, they provide this service to a company due to their employer's hiring.
To determine whether outsourcing the LGPD DPO is worthwhile, it is necessary to consider the advantages it offers. Here are some of the main advantages:
First and foremost, it is essential for companies, organizations, and websites to have a clear determination of who the DPO is in order to comply with the LGPD. Currently, all companies must have one, although there are indications of a potential limitation of this requirement in the future.
In this regard, note that it is not always easy to hire someone with the necessary knowledge for this role or to train them to fulfill the duties of a DPO. Therefore, compliance can be more rapid and straightforward through the outsourcing of such services.
Once a qualified professional or even a company with multidisciplinary knowledge for the role is found, the adaptation process becomes much faster. This is because each company and market has its own specificities.
Every new area and law requires extensive study and is subject to various short-term changes. Therefore, outsourcing this role also means outsourcing the responsibility of staying up-to-date and investing in the professionals' training.
Roles involving oversight and audit can sometimes create conflicts with departments and even managers. It is essential for the DPO to have autonomy in their work and even stability, as prescribed by the law. After all, they cannot be threatened with job loss for overseeing processes within the company. Therefore, outsourcing this responsibility can lighten the organizational atmosphere.
Just like any service provider, working with a contract makes it much easier to replace them compared to a full-time employee. Therefore, having a DPOaaS as a legal entity provides much more flexibility in case adjustments or replacements are needed over time.
Labor and social security charges are quite substantial in Brazil. Hiring a legal entity for this role can lead to reduced costs for the company while increasing the remuneration of the service provider.
ATTENTION: It is important to note that, regardless of how responsible a service provider may be for their role, they are still under the hierarchy of the employer. Therefore, ultimate decisions may be the responsibility of the company's administrators, even when using DPOaaS. Be cautious not to rely on outsourcing as a means of avoiding responsibility.
The same applies when the company does not appoint a DPO; the ultimate responsibility falls on the managing partners. When appointed, the professional acts on behalf of the company and its representatives before the national authority.
### Do you know the difference between Data Mapping and ROPA in LGPD?
Another interesting aspect of outsourcing the DPO is that this way, you can have an expert in the field. As mentioned above, it is not your company that is responsible for the training; it is the hired professional or company.
This ensures even greater security for operations to comply with LGPD and be in the hands of experts. It is even better when the professional is part of a network or multidisciplinary group that can assist with the specificities of your business and market.
In this case, the functions are the same as those of an internal DPO. After all, outsourcing only refers to the possibility that the activities are carried out by an external agent to the company.
As mentioned above, this agent can be a legal entity or a natural person. Either way, they must be specifically identified within the Privacy Policy and other documents related to consent, use, and data processing.
Any changes regarding who is responsible as the LGPD DPO must be reflected in policy changes. Failure to do so would result in a violation of the General Data Protection Law and the creation of risks such as fines and even suspension of databases.
Want to learn more about the responsibilities of a Data Protection Officer? I've prepared this article for you!
Tags
Related posts

Virginia VCDPA: Privacy Policy
What the Virginia VCDPA requires from your Privacy Policy: the 5 mandatory content categories, sensitive data obligations, targeted advertising disclosure, and the appeal process explained.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.
5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.

Connecticut CTDPA: Cookies Policy
What the Connecticut CTDPA requires from your Cookies Policy: opt-out link, opt-out preference signal from January 2025, 15-day consent revocation, teen protections, and targeted advertising definition.
Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.

Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!

New Hampshire NHDPA: Cookies Policy
Cookies Policy under NHDPA explained. Discover what's mandatory, dark patterns to avoid, and how to implement legal cookie consent.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.

California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

Why Give Consent on Every Website I Visit?
Have you ever noticed that every time you sign up for a service to access information or register on a website for purchases, you need to give consent? If you're wondering why you have to give consent on every website you visit, you'll find the answer here.
New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
Understand the meaning of the LGPD for your company
Surely you've already seen the predictions of fines and sanctions, processes. But, what does it mean to your company?
IOWA ICDPA: Privacy Policy
What the Iowa ICDPA requires from your Privacy Policy: five mandatory elements, 90-day response deadline, 60-day appeal process, opt-out for sensitive data, no retention periods required, and the 90-day cure period.

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.

Utah UCPA: DSAR and Privacy Portal
Utah UCPA DSAR guide: four consumer rights, limited deletion scope, no right to correct, no formal appeal process, no opt-out of profiling, 45-day deadline, and the guaranteed 30-day cure period.
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.
New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
Colorado CPA: DSAR Privacy Portal
How to handle DSARs under the Colorado CPA: 5 consumer rights, portability limited to twice per year, Universal Opt-Out Mechanism, 24-month record retention, and District Attorney enforcement.

What is Privacy by Design?
With it, all companies that collect personal data such as email, name, phone number, among others, must be attentive to its guidelines and obligations. With the arrival of new laws, some terms begin to stand out, one of them is Privacy by Design, learn more in this post.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.

Data Protection Officer and LGPD, a Solitary or Teamwork Job?
How do you deal with a profession that didn't even exist a few years ago and is now mandatory in companies? That's precisely the question that arises when we think of the figure of the Data Protection Officer or DPO.
Oregon OCPA: DSAR Privacy Portal
Oregon OCPA DSAR guide: the L.O.C.K.E.D. rights, opt-out without authentication, derived data in deletion scope, 15-day revocation deadline, GPC from January 2026, and the elimination of the cure period.

California CPRA: Privacy Policy
What the California CPRA requires from your Privacy Policy: SPI category, two mandatory links, data retention periods, sharing disclosure, right to correct, GPC, and minor protections.

What are Terms of Use and their importance for the LGPD?
Ignoring Terms of Use and their significance within a website, particularly now with LGPD, is a common mistake that both consumers and website owners frequently commit.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.
Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
Responsibilities of a data protection officer.
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack.
California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
California CCPA: Cookies Policy
What the California CCPA/CPRA requires from your Cookies Policy: Do Not Sell or Share link, GPC compliance, sale vs sharing distinction, sensitive PI opt-out, and annual updates.
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.
Explore AdOpt
Autor
João Bruno
19 Sep 2023
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


