Data Mapping or Data Inventory - a life jacket for the DPO!
With Data Mapping, we gain a deep understanding of the 5 stages that every piece of data goes through within any department of a company, regardless of its size or industry. Again, my dear friend, you don't need to be a PhD in PMBOK or Project Management to understand these crucial stages! Data Mapping and Data Inventory have become one of the most essential tools for Data Protection Officers (DPOs)!
The market today has brought a lot of technology and quality to these processes! We have no complaints about that. But my goal here today is to teach you to see things in a simpler and more objective way, as they truly are – a straightforward arrangement of facts, and that will already help you.
So, let's get started!
A basic concept that will guide your understanding from now on:
Therefore, each process can be organized in an order, or not, thus forming the routines of the departments.
Thus, for each process in your company, the following 5 points can be fulfilled in full or in part.
They are:
And what do I do with these 5 points above?
Yes, it's hard, I know!
But, it will be extremely valuable in case of a notification from the National Data Protection Authority (ANPD) or even before that, in case a customer or visitor to your website asks for access to the data you may have about them.
Of course, if you're a small business or have very few employees and processes, all of this can be summed up in 3 or 4 systems (email, marketing automation, some Google Drive, and accounting) because everything is stored in these places. Now, imagine a company with 500 employees in 10 cities.
Remember, according to LGPD, any data subject can knock on your door asking if you have any of their data, and you must respond promptly.
So, without the "treasure map," how will you know that [email protected] subscribed to the Newsletter, made a purchase 3 months ago, and was your employee 5 years ago?
In the above example, you would have to report to that person that you have data such as:
- Name, Email, CPF, Phone, Address, Work Permit, Parentage (HR data), and sharing with Google and Facebook.
For the following reasons:
1- Hiring in the past, so labor legislation obliges you to keep this data in your accounting for X years. In other words, even if he requests deletion, you can deny it, due to another legislation.
2 - Purchase of products X, Y, Z 3 months ago.
This also generated registration in the newsletter (with the famous "I accept to receive promotions"). From the newsletter, you have him on the mailing list for new products and updates from your e-commerce, and all remarketing tools are connected, pursuing him daily across the internet, every time he visits to see your products.
Therefore, he can freely request the deletion of all his data for marketing purposes. This will lead to a series of actions. These include:
- Deleting the email and other data in the CRM and email delivery tool.
- Distributing the Opt-out request to any systems you are integrated with that use this data. (logistics and ERP systems, for example)
- Removing him from the Google and Facebook remarketing segment.
- Reporting in an official company document that the above steps were promptly completed.
(For AdOpt clients, when integrated with Tag Manager, the cookie part becomes much easier! Because when a visitor does not authorize some of them, AdOpt automatically blocks this firing!
Additionally, a visitor's request on the opt-out page sends an email to you immediately, with this request linking the requester's email to the Cookie ID generated in the Opt-In.
So, you can start this search with greater direction if the requester has given consent to any tools and when.
Do you understand now the importance of mapping your company's processes?
Only with all this in hand will you have peace of mind and, more importantly, ease of accessing all this data promptly. For some companies, around 48 to 72 hours (a reasonable response time...) is more than enough, for others, it's practically impossible.
Whether you or your hired DPO, we can't stop the company for every request from a visitor. With Data Mapping in hand, this search is much faster, targeted, and, I dare say, automated, if you use software just for that.
Here's a more detailed breakdown of each of the points in Data Mapping:
- Motivation - Why do we need this data?
If LGPD hasn't already prompted you and your company to reflect on the real need for personal data in your business, stop and do it as soon as possible.
Yes! Often, especially in Marketing and Sales, there's a compulsion for qualification and identification information about prospects and leads for each stage of the funnel. It's great to pick up the phone and close the final details of a sale or surprise an undecided customer and convince them of the value of your business.

But the point I emphasize is: Reconsider the real needs of accessing, processing, and storing this data. You don't necessarily need to have an Excel sheet with thousands of lines of your inactive customers from 5 years ago, hoping to rekindle this dead list one day. In light of LGPD, your risk has already been measured; is it worth it?

[In this article, I present 10 marketing processes that you should rethink in light of LGPD!](https://goadopt.io/en/blog/10-risky-processes-in-your-marketing/)
2. Collection.
What are the ways in which each process collects/receives your data, along with your consent? Do all data enter the company through a single entry point, or more than one?
List them all and review whether each entry point displays the necessary policy and process communications, and whether consents from each data subject are also collected alongside the data. Even if in an analog/offline manner, consent is essential.
1 – Consent.
Yes, consent is essential, but it's not the only instrument that allows you to access or process personal data.

In this [article, we list all the legal bases](https://goadopt.io/en/blog/legal-bases-of-lgpd/) that support the use of personal data according to LGPD.
3. Processing / Treatment
1 – Internal sharing among departments and systems.
- Are third-party software used for data processing?
- How do data flow between them?
- Is the software aligned with your process and privacy policy?
- If a data subject requests the deletion of their personal data from your company, how do you notify this external or internal supplier to process the deletion?

- Is there any documentation or search tool to assist the DPO in case of scanning, making it easy to locate data of a data subject in the department?

3.2 – Storage for internal use and consultation.

- During the processes where data is stored?
- For how long?
- Files, physical hard drives, or in the cloud?
- Is this cloud in the national or international territory?
- Who will be responsible for deleting or querying the database in case of a request?

- Is there any documentation or search tool to assist the DPO in case of scanning, making it easy to locate data of a data subject in the department?

3.3 – Backup.

- What is the frequency and rules for backup?
- Files, physical hard drives, or in the cloud?
- Is this cloud in the national or international territory?
- Who will be responsible for deleting or querying the database in case of a request?

- Is there any documentation or search tool to assist the DPO in case of scanning, making it easy to locate data of a data subject in the department?
4. Disposal
Although greatly facilitated for digital files, this stage of the process is quite serious. Many files remain in the "trash" and are not properly deleted.
For physical files, this problem is even greater when disposal is done poorly or neglected.
Understand this process and, especially if there are third parties involved in the stage, include them in your monitoring of third parties potentially involved.
- End of the process?
Is the end of the process indeed the end of the data's journey in the company, or is it just the beginning of another?
Certainly, at first glance, all these questions and concerns may seem excessive. But believe me, these are just some of the questions you would/have to answer if you hire a consulting and compliance service.
Or, in a scenario not as informal as this text, a visit from the ANPD.
I hope I have helped you gain a better understanding of how these stages are essential in a DPO's routine.
With Data Mapping, we certainly have the foundation for creating a more robust privacy policy.
Did you miss any items or descriptions?
Send them our way; we are open to improvements, always! - You can send them to [email protected]
A recommended further reading to delve deeper into the subject is:
Tags
Related posts
Understand the meaning of the LGPD for your company
Surely you've already seen the predictions of fines and sanctions, processes. But, what does it mean to your company?
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.
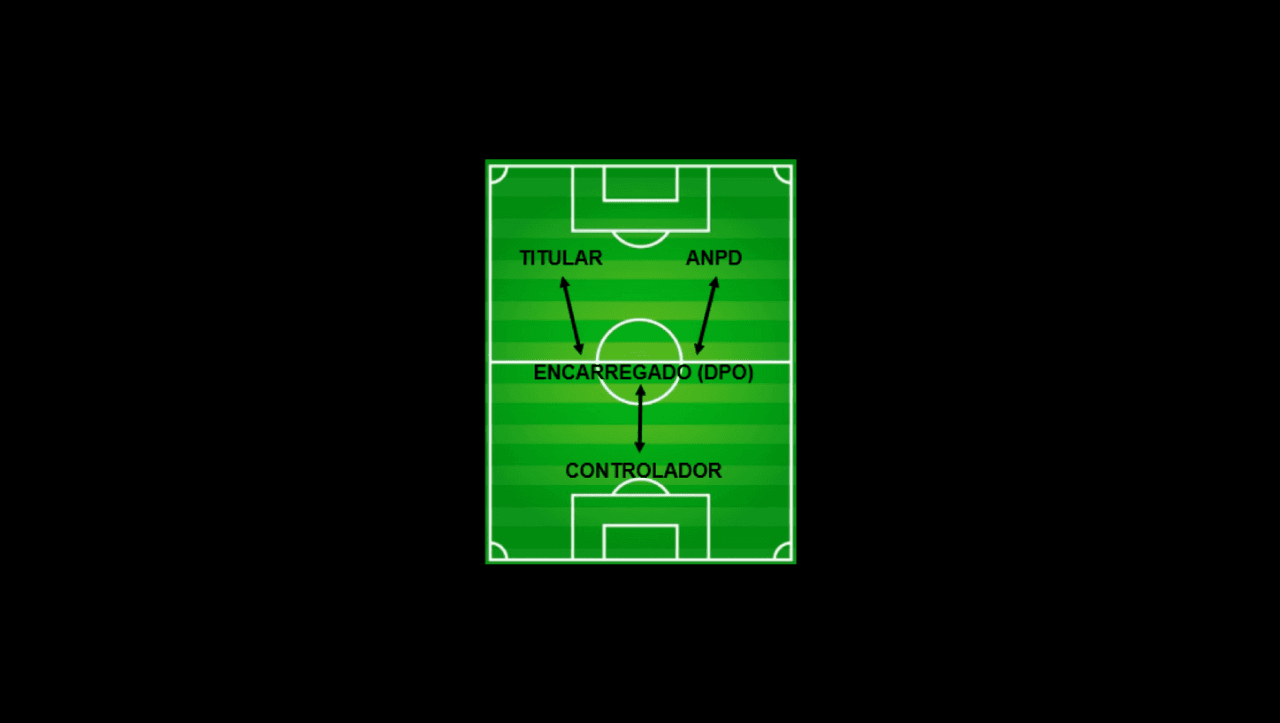
Responsibilities of a data protection officer.
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).

Data Protection Officer and LGPD, a Solitary or Teamwork Job?
How do you deal with a profession that didn't even exist a few years ago and is now mandatory in companies? That's precisely the question that arises when we think of the figure of the Data Protection Officer or DPO.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.
5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.

New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.

Virginia VCDPA: Privacy Policy
What the Virginia VCDPA requires from your Privacy Policy: the 5 mandatory content categories, sensitive data obligations, targeted advertising disclosure, and the appeal process explained.
Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
California CCPA: Cookies Policy
What the California CCPA/CPRA requires from your Cookies Policy: Do Not Sell or Share link, GPC compliance, sale vs sharing distinction, sensitive PI opt-out, and annual updates.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.
Colorado CPA: DSAR Privacy Portal
How to handle DSARs under the Colorado CPA: 5 consumer rights, portability limited to twice per year, Universal Opt-Out Mechanism, 24-month record retention, and District Attorney enforcement.

Connecticut CTDPA: Cookies Policy
What the Connecticut CTDPA requires from your Cookies Policy: opt-out link, opt-out preference signal from January 2025, 15-day consent revocation, teen protections, and targeted advertising definition.
Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.
Oregon OCPA: DSAR Privacy Portal
Oregon OCPA DSAR guide: the L.O.C.K.E.D. rights, opt-out without authentication, derived data in deletion scope, 15-day revocation deadline, GPC from January 2026, and the elimination of the cure period.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.

Utah UCPA: DSAR and Privacy Portal
Utah UCPA DSAR guide: four consumer rights, limited deletion scope, no right to correct, no formal appeal process, no opt-out of profiling, 45-day deadline, and the guaranteed 30-day cure period.

IOWA ICDPA: Privacy Policy
What the Iowa ICDPA requires from your Privacy Policy: five mandatory elements, 90-day response deadline, 60-day appeal process, opt-out for sensitive data, no retention periods required, and the 90-day cure period.
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.
Explore AdOpt
Autor
João Bruno
20 Sep 2023
AdOpt


Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website


Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


