The Brazilian Data Protection Law (LGPD - Lei Geral de Proteção de Dados) emerged a long time ago and has since drawn attention from numerous professionals. However, it is not uncommon to find websites and companies that ignore it, as they seek time to adapt. In this regard, how long can we ignore LGPD?
Well, it is no longer possible to ignore it. This has been a reality since its approval. Furthermore, it has been enforced since 2021.
With that in mind, it has been several years since this law was introduced, which leaves no excuse for ignoring it. Moreover, ignorance of the law can bring significant consequences, like fines.
Therefore, the clock is ticking against those who have chosen to postpone the necessary adaptations imposed by LGPD. It is time to change your stance. How and why to do so will be explained below.
LGPD is often mentioned, yet little is said about its actual requirements. However, it has become essential for online users and website owners to understand what it entails.
Only then can the true importance of this law be comprehended. But don't worry, we won't use legal jargon to explain it to you.
The LGPD is a nationwide regulation that came into effect in 2020. Many expected it to be implemented later, as there were speculations about its postponement, as seen before.
However, that did not happen. In other words, LGPD has been a reality since 2020 and requires attention. Many believe that it only applies to companies and their websites. However, it governs how all legal entities, including companies, governments, NGOs, associations, churches, and various other organizations, handle the data of the country's citizens.
It is worth noting that LGPD and all other privacy regulations do not only focus on digital data but encompass all types of data. Therefore, how a company handles an email provided on a website or on a clipboard matters! Similarly, this extends the care to not only the website's servers but also to files, cabinets, and notebooks that "store" such data.
In summary, all processes in your company that involve personal data in their workflows must be reevaluated and adapted.
Assuming that you already understand that every time you visit a website or take an online action, both your browser will record signals and the website will receive information about you. Let's reinforce that this cannot happen indiscriminately, right? That is precisely what the General Data Protection Law addresses. It ensures limitations on the use of personal data, whether on websites or any other environments.
(If you haven't grasped that we are talking about Internet Cookies, read about them here before proceeding.)
With this, the law aims to protect users' privacy and intimacy. It also ensures that they have a better understanding of how their data is used and the security measures taken by the company that has access to that information.
But it doesn't stop there. LGPD also introduces data classification concepts and specific safeguards regarding data breaches and handling.
Ultimately, this law aims to promote transparency between websites and users. It imposes measures that can ensure their security. Therefore, in summary, it establishes four crucial points regarding data protection:
- Appropriate handling and use of personal data.
- Request for authorization and/or revocation regarding data collection.
- Penalties for companies that fail to comply with the aforementioned measures.
- Freedom for all citizens to access their own data.
It should be clear to you by now that LGPD has brought forth a series of important issues that completely impact the way companies operate.
Now, bringing it into the digital environment we are currently in, it becomes even more crucial for companies to demonstrate transparency to their visitors and strictly adhere to authorizations and policies.
Although the law granted a transition period for companies until August 2021, that deadline has already passed. In other words, the application of penalties and fines under the General Data Protection Law is now possible for websites that fail to comply with its guidelines.
Therefore, if your website still doesn't have clear privacy policies, in the case of cookie usage, or a cookie banner that respects personalized authorizations, it is at risk.
The penalties under LGPD are quite severe and include warnings (less severe) and fines. For non-compliance, the fine can be up to 2% of the company's annual revenue (with a maximum calculation base of R$ 50 million). Additionally, there are possibilities of sanctions that can block a company's database until they regularize their operations.
In this sense, continuing to ignore the law that regulates data security and protection is shooting yourself in the foot for your company.
By doing so, you put your website and your company at risk. Even in the best-case scenario of receiving only a warning, persisting in the error will affect your finances and the image of your website, as well as access to data that is crucial for your activities.
Ignoring LGPD is no longer an option since the deadline for compliance with the law has passed.
As we are currently in the digital environment, let's focus on how to help you in this process. After all, many companies nowadays have a significant portion of their processes and operations in the digital realm. Such as e-commerce, digital agencies, product launches, info product creators, startups, and more.
All the examples mentioned above rely on the use of personal data for marketing automation, landing pages, various tracking pixels with remarketing cookies, media campaigns, and so on.
In short, it is impossible to continue ignoring this law. But how can you put it into practice? Don't worry, we have prepared a basic step-by-step guide with some essential principles.
Remember, LGPD is not just a checkbox on your website; it involves a change in processes and a culture focused on privacy. So, below are some tips. If you take them seriously, you will find some valuable further guidance at the end. (Some people are charging a lot for the information we provide here for free - you're welcome!)Info
First and foremost, it's impossible to talk about LGPD compliance without a plan. What does that mean? Understand that you'll never feel confident in what you're doing if you don't know where the data is, where it comes from, where it goes, who processes and uses it. Therefore, you need a Data Mapping, here's an article that will help you understand what it is and how to create one.
You know when you're at the grocery store and you see a product out of place? It's kind of bizarre, right? It gives us an uncomfortable feeling, as they would say in the South of Brazil. So, seriously, dedicate some time to this, and you'll see that all the other steps will be simplified. You don't want to find a toothbrush in your sock drawer when the Regulatory Agency comes knocking at your door.
First and foremost, it's impossible to put LGPD respect into practice without developing a privacy policy. It provides comprehensive information on how the company collects data, how it uses it, with whom it shares it, its usage deadlines, and other details.
Likewise, it clarifies how data is stored and what precautions are taken to ensure security against leaks, for example. So, remember to use clear and accessible language and address all relevant points in detail.
What's the basis for writing a good policy? Guess what! Your Data Mapping from the previous point. So, don't skip the previous step, trust us!
Here's an article to help you with the privacy policy.
Remember that we're talking about digital companies, right? These companies have a very peculiar characteristic: the entry points for data are usually all digital. Therefore, it's much easier for us to control what goes through them! And even better, with the use of technology!
That's why your Cookie Banner or CMP - Consent Management Platform, when properly implemented, becomes practically a "Pareto of Compliance," those 20% of effort that solve 80% of the problems.
In other words, make sure your website has an appropriate cookie banner that helps you organize data from the moment of entry. The cookie banner won't be your silver bullet, but it will be an excellent start to keep things in order over time.
Here's an article for you to better understand how an LGPD cookie banner works.
For that, rely on Adopt. Our team consists of experienced professionals in the market who provide all the assistance you need. Here, we help you choose a cookie banner for your website.
Another important point for adapting your company and website to the Data Protection Law is to increase the focus on information security. Companies have always been responsible for leaked data, but now even more so! Therefore, let's work hard to prevent any leaks or resulting damages that can have serious consequences for companies and the individuals whose data is exposed.
Therefore, highlight the risks of leaks and security in your data mapping. Once again, dedicate time to these security criteria and processes. You won't regret having them mapped and controlled because, in times of chaos, the best feeling is knowing that you are prepared and know what to do!
Finally, also apply your care in applying LGPD to your marketing actions. After all, it's necessary to strictly adhere to using communications and campaigns only to those who have authorized their receipt, as well as other flows that are triggered through the use of personal data.
Here's another interesting article for you: 10 Marketing Processes You Need to Reconsider under LGPD.
As mentioned before, these are just a few steps. If you want to delve deeper into compliance topics, the next article for you is here.
Tags
Related posts
5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.

Connecticut CTDPA: Cookies Policy
What the Connecticut CTDPA requires from your Cookies Policy: opt-out link, opt-out preference signal from January 2025, 15-day consent revocation, teen protections, and targeted advertising definition.

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.

California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

How to delete cookies and cache in Chrome and other browsers?
Tired of the ads from that site you visited following you around? Is your computer running slow when accessing a particular website? Want to delete all cookies from a specific service or site?

Why Give Consent on Every Website I Visit?
Have you ever noticed that every time you sign up for a service to access information or register on a website for purchases, you need to give consent? If you're wondering why you have to give consent on every website you visit, you'll find the answer here.

New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
The Impact of Cookie Banners on Your E-commerce - LGPD
Having a cookie banner on your brand's website has become indispensable for many. However, for e-commerce websites, it has practically become an obligation to have one. This is because this type of website has a technological composition in which cookies are a structural part. Login flow, items in the shopping cart, recommendation showcases, remarketing... Most of them rely on cookies.

MTCDPA Montana and Cookies: All you need to know
Find out if the MTCDPA applies to your site, key compliance deadlines, and new rules for cookies and consent in Montana

IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.

Utah UCPA: DSAR and Privacy Portal
Utah UCPA DSAR guide: four consumer rights, limited deletion scope, no right to correct, no formal appeal process, no opt-out of profiling, 45-day deadline, and the guaranteed 30-day cure period.
Montana MTCDPA: Privacy Policy
Learn what your MTCDPA Privacy Policy must include after Montana's SB 297 amendments from the conspicuous "privacy" hyperlink and last-updated date requirements to sale disclosures, minor protections, and how to keep your notice operationally aligned with your stack.
Once upon a time, there was a company that got fined. - THE END
Sad, but this story is more real than you think. It all started with a "surprise" fine. Ever imagined everything crumbling around you? All because of a fine, an invoice that came "out of nowhere"? Your bank account, clients, your job, your car loan, marriage...
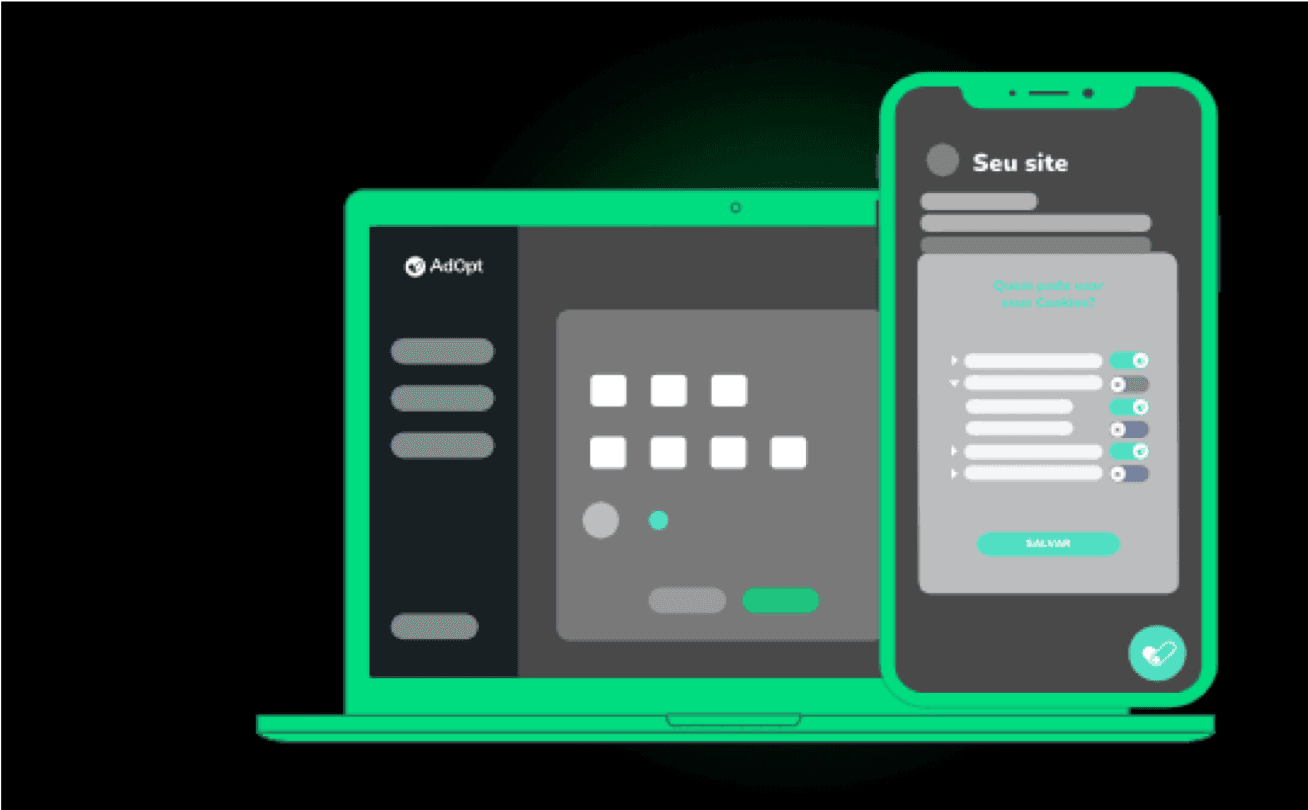
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.

Key Differences between LGPD and GDPR and the Impact on Internet Cookies
While both regulations share the goal of safeguarding individuals' rights regarding the processing of their personal data, there are some important differences between them. It is crucial to understand these distinctions and their implications, particularly in the context of internet cookies.
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.
New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
Tenesse TIPA: Cookies Policy
Learn how to build a defensible TIPA Cookies Policy for Tennessee compliance covering consent architecture, opt-out requirements, the NIST affirmative defense, and how your cookie banner, privacy notice, and vendor management must work together under the Tennessee Information Protection Act.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Florida FDBR and Cookies: All You Need to Know
Everything you need to know about the Florida Digital Bill of Rights (FDBR): who must comply, the $1 billion threshold, 7 consumer rights, FIPA vs FDBR explained, penalties, and cookies.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

LGPD and Cookies all do you need to know?
In this article, you will have a great introduction to the topic, as well as various other variations that revolve around the subject: Cookies and LGPD.

California CPRA: Privacy Policy
What the California CPRA requires from your Privacy Policy: SPI category, two mandatory links, data retention periods, sharing disclosure, right to correct, GPC, and minor protections.
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.
Colorado CPA and Cookies: All You Need to Know
The Colorado Consumer Privacy Act went into effect July 1, 2023 (CPA). CPA is a vital piece of legislation designed to protect the privacy of residents in Colorado. Understanding its requirements is essential for any business operating in the state. This act is all about giving control back to the consumers regarding their personal data. But what does this mean for you and your business, especially when it comes to managing cookies on your website?
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.
Colorado CPA: Privacy Policy
What the Colorado CPA requires from your Privacy Policy: 5 mandatory elements, purpose specification duty, secondary use prohibition, 24-month consent refresh, and Universal Opt-Out Mechanism disclosure.
LGPD & COOKIES - ANPD Releases "Guidance on Cookies and Personal Data Protection"
On October 18, 2022, the National Data Protection Authority (ANPD) released the "Guidance on Cookies and Personal Data Protection." Highly anticipated by professionals in the field, this document is of utmost importance as it examines various applicable legal scenarios and establishes the requirements to be observed in the case of cookie usage.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.

Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA

California CPRA: Cookies Policy
What the California CPRA requires from your Cookies Policy: the sharing concept, GPC as valid opt-out, Do Not Sell or Share link, SPI geolocation, minor protections, and retention periods.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Explore AdOpt
Autor
João Bruno
12 Sep 2023
AdOpt


Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website


Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


