5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle privacy regulations like LGPD, CCPA, GDPR...?
What strategies does it use to comply with the any of them?
Have you thought about using a cookie banner but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.
Below, check out 5 signs that indicate your strategies either don't exist or aren't working as they should. So keep reading to ensure the necessary compliance of your site with the principles of the law that regulates data consent.
Check out the top 5 signs that your website isn't in compliance with privacy regulations and then see how to start your adjustment!
This is an undeniable sign that you need to reconsider how you view LGPD, GDPR, CCPA, etc. After all, it regulates the use of third-party data.
It requires respect for user privacy and their consent. Therefore, data usage should always be informed. Not only that, but also the purposes to which it is directed, the way it is stored, and the period of use.
So, consider that if you don't know what data you collect, how will you inform the visitor? Furthermore, how will you ensure that the use of this information complies with the limits imposed by the data subject?
These are important questions that indicate that something is not right on your website regarding privacy and its requirements.
LPs created without control, rich content available for download without accepting terms and policies, mailing lists being shared and passed from campaign to campaign... Be cautious!
I've separated this article for you, in case this is your situation:
Understand the meaning of LGPD for your company.
Cookies are another type of data that, in principle, should be informed by websites to their visitors. After all, they also capture information about these data subjects and, therefore, fall within the concept of data usage that any privacy regulation addresses.
The use of cookies is almost natural for most websites, especially if they come from e-commerce platforms, for example.
### To check if your site triggers cookies, access it from a computer and - in Google Chrome, click on the padlock just to the left of the address. It should show exactly which ones and how many there are.
However, many pages fail to see cookies for what they really are: data files and personal information. Therefore, the absence of this communication to your site's visitors is dangerous as it can be a violation of the law.
In fact, not just that, but the collection of them without prior consent is also a violation. You know that "We use Cookies" pop-up? Well, it's not there for no reason.
It's a way to comply with GDPR, CCPA,LGPD... as it informs the use of this type of file while capturing authorization to use them.
- In this article, I help you understand more about consent as a Legal Basis.
- In this one, how to choose an appropriate CMP - Consent Management Platform for your website.
Your site probably has documents such as Privacy Policy and Terms of Use. They inform, respectively, the use of visitor data (and capture authorization for it) and the prevailing rules, rights, and duties.
Therefore, they are very important, especially in the times of privacy regulations!
They stand out for their informative content to promote transparency with the data subject.
It is up to the data subject, then, to accept or not the conditions therein. In this sense, it is worth noting that the site may suspend access to some services, for example, due to a lack of acceptance of the rules and conditions. And that is natural since some of them are only possible with the authorization to use certain data.
Either way, these are important documents. But they shouldn't just be there. They should be specific to what the site offers and how it operates. So if you made your terms and policies based on Ctrl C + Ctrl V, pay attention!
It's time to review these documents and rewrite them to make them compatible with the reality of the site. Also, to fill gaps and clarify data usage. Below, I've separated a few more articles for you:
- What is a Privacy Policy?
- What's the Ideal Privacy Policy for Your Company?
- What are Terms of Use in LGPD?
When it comes to data loss, it's time to sound the alarm. Data breaches are a clear sign that your privacy compliance strategy needs urgent correction or revision.
After all, it should be developed to maintain the confidentiality of data and their use in accordance with the data subject's consent or the legal basis chosen. Also, to ensure the protection of this information.
Data breaches are compromising! They can tarnish the company's reputation and often that of its customers and suppliers as well. Furthermore, the company can be held responsible for them and, as a result, face significant sanctions, including hefty fines.
Understand the difference between Data Controller and Data Processor here.
And it's not just data loss itself. The lack of a clear plan of action in the event of information leaks is also an indication that you urgently need to work on your LGPD strategies. Below are some more articles to help you with this review:
- Data Mapping or Inventory in LGPD, the DPO's life jacket.
- How to Adapt Your Marketing to LGPD
- 10 Risky Processes in Your Marketing
Finally, the last sign that your website needs an LGPD, GDPR, CCPA strategy is the absence of the designation of a Data Protection Officer or DPO (Data Protection Officer) for the processing of data on your site.
This figure is a requirement of LGPD, GDPR, CCPA and, according to the laws, is responsible for controlling and managing data processing. They carry out tasks determined by the Data Controller.
They are also the ones who handle complaints from personal data subjects, provide explanations, and communicate with them. Similarly, they control the entry and exit of consents, so they take the necessary actions to ensure compliance with authorizations. In this article, I explain more about the responsibilities of a Data Protection Officer or DPO in LGPD.
If you have recognized that your site falls into any of the signs above, it's a sign that you should take action to align it with the law. Otherwise, you may face fines and other penalties that could even lead to the suspension of your page's activities.
Not to mention the impact on your brand's image in the eyes of the public, as someone who could care more about data privacy.
So, it's more than time to review your privacy strategies in the face of LGPD, GDPR, CCPA... For this, count on AdOpt, which helps you not only organize them but also control the entry and use of data, as well as consents about them.
The article lists five signs: having no control over the data you collect and use, giving no information about cookies, using a generic privacy policy and terms of use, suffering data loss or a breach, and having no designated Data Protection Officer. If any of them applies, the article says it is a sign that the site should take action to align with the law.
Yes. The article explains that cookies capture information about visitors, so they fall within the concept of data use that privacy regulations address. Not informing visitors can be a violation, and so can collecting cookies without prior consent. The "We use cookies" pop-up exists to inform visitors about this type of file while capturing authorization to use it.
The article suggests opening your site on a computer in Google Chrome and clicking the padlock to the left of the address. It should show exactly which cookies exist and how many there are. It also notes that many pages fail to see cookies for what they are, which are data files and personal information, so the lack of communication can be dangerous.
The article says the Privacy Policy and the Terms of Use should not just be there. They should be specific to what the site offers and how it operates. A policy copied with Ctrl C + Ctrl V may not match the site's reality or clarify its data usage, so the article recommends reviewing and rewriting those documents to fill gaps.
According to the article, a site can face fines and other penalties that could even lead to the suspension of the page's activities. Data breaches can tarnish the company's reputation and that of customers and suppliers, and the company can be held responsible. There is also an impact on the brand's image in the eyes of a public that may care about data privacy.
Tags
Related posts
Florida FDBR and Cookies: All You Need to Know
Everything you need to know about the Florida Digital Bill of Rights (FDBR): who must comply, the $1 billion threshold, 7 consumer rights, FIPA vs FDBR explained, penalties, and cookies.
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.

IOWA ICDPA and Cookies: All you need to Know
Iowa ICDPA explained: the longest response deadline of all US state privacy laws (90 days), 90-day cure period, opt-out for sensitive data, limited deletion scope, no right to correct, and how it compares to UCPA, VCDPA, and OCPA.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!

Montana MTCDPA: Privacy Policy
Learn what your MTCDPA Privacy Policy must include after Montana's SB 297 amendments from the conspicuous "privacy" hyperlink and last-updated date requirements to sale disclosures, minor protections, and how to keep your notice operationally aligned with your stack.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

Cookies and the TDPSA
If your website uses cookies and serves users in Texas, the Texas Data Privacy and Security Act (TDPSA) applies to you. This article breaks down exactly how cookies are treated under the law—and what your business must do to remain compliant and build user trust.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.

Cross-Domain Cookie Consent: One Choice, Several Sites
Cross-domain cookie consent lets one visitor choice apply to several sites. See when sharing is valid, how tags read it and what to test before you launch.
Colorado CPA and Cookies: All You Need to Know
The Colorado Consumer Privacy Act went into effect July 1, 2023 (CPA). CPA is a vital piece of legislation designed to protect the privacy of residents in Colorado. Understanding its requirements is essential for any business operating in the state. This act is all about giving control back to the consumers regarding their personal data. But what does this mean for you and your business, especially when it comes to managing cookies on your website?
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

Canada PIPEDA: Privacy Policy
How to write a PIPEDA privacy policy: what the ten principles require you to disclose, what to add for Quebec, and a checklist before you publish.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.

Global Privacy Control (GPC) Explained: What It Is and Who Has to Honor It
Global Privacy Control (GPC) is a browser opt-out signal. Learn how it works, which US states require you to honor it, and how to test your site.
California CCPA and Cookies: All You Need to Know
Everything about the California CCPA and CPRA: who must comply, the $25M threshold, 7 consumer rights, CCPA vs CPRA explained, the Do Not Sell link, CPPA enforcement, and cookies.

How to delete cookies and cache in Chrome and other browsers?
Tired of the ads from that site you visited following you around? Is your computer running slow when accessing a particular website? Want to delete all cookies from a specific service or site?
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.
LGPD: An Opportunity for Digital Marketing Agencies!
Have you ever thought that your marketing agency could find a great business opportunity in LGPD? Well, unlike what many think, it brings changes that can accelerate the demand for the services of these companies.
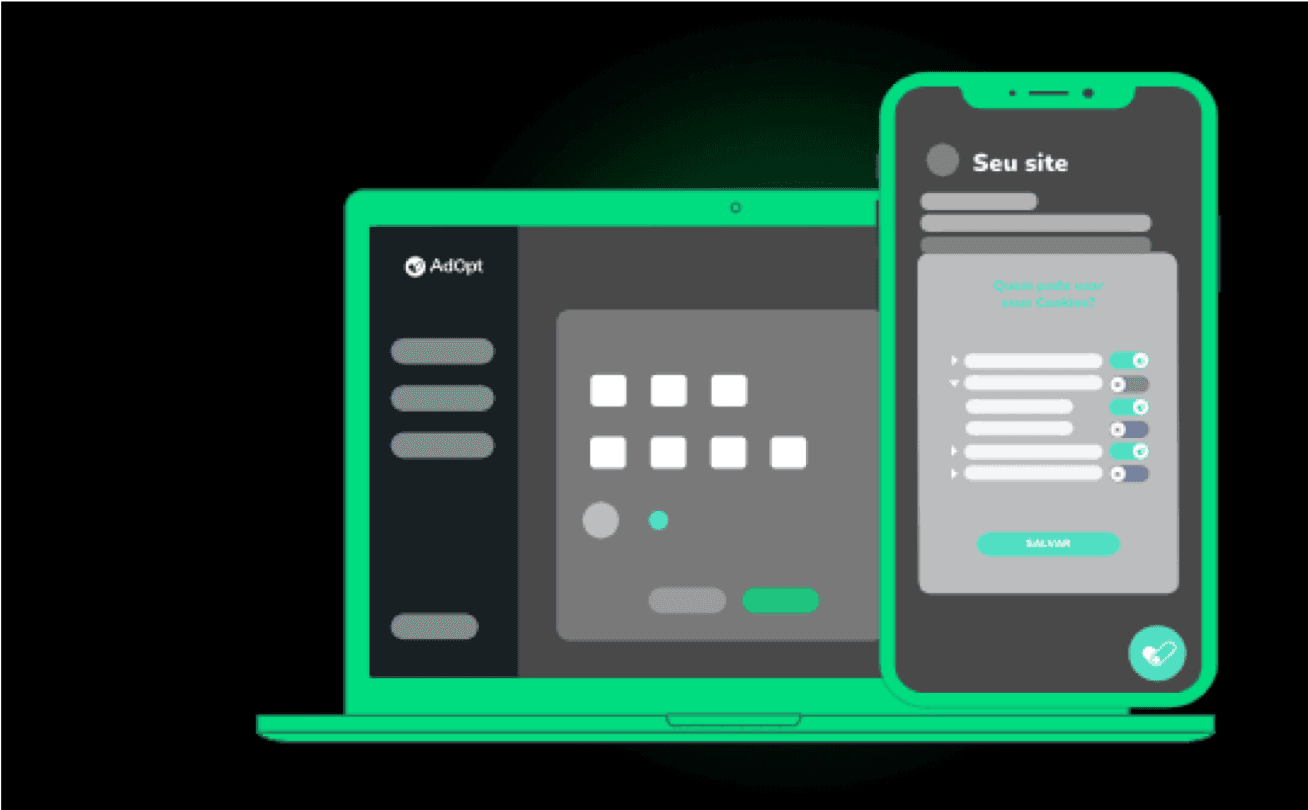
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

Key Differences between LGPD and GDPR and the Impact on Internet Cookies
While both regulations share the goal of safeguarding individuals' rights regarding the processing of their personal data, there are some important differences between them. It is crucial to understand these distinctions and their implications, particularly in the context of internet cookies.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Axeptio acquires Brazil's AdOpt, expanding global reach in consent management and LGPD compliance.

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

Consent Management Across Countries: How One CMP Serves Every Market
Consent management across countries: how one CMP applies the right rules to each visitor, passes the choice to Google and Meta, and honors GPC.
Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Utah UCPA: Privacy Policy
What the Utah UCPA requires from your Privacy Policy: five mandatory elements, opt-out model for sensitive data, no retention periods required, no active contact channel mandate, and the guaranteed 30-day cure period.

Canada PIPEDA and Cookies: All You Need to Know
PIPEDA is Canada's federal private-sector privacy law. See when it reaches your website, what it requires for cookies, and how to prove consent.

How to Choose a CMP (Consent Management Platform)?
Using a CMP (Consent Management Platform) is a great way to make efforts to adapt to new privacy regulations like GDPR, LGPD, DPDPA, CCPA and more...
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

Canada PIPEDA: Cookies Policy
What a PIPEDA cookie policy must say: purposes, third parties, opt-out, retention and Quebec rules. Plus a checklist to write yours.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.

Fines in LGPD - What are they, amounts, and compliance deadlines
In this article, we will answer all your questions regarding fines under the LGPD (Brazil's General Data Protection Law).
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.

5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
Explore AdOpt
Autor
João Bruno
19 Sep 2023
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


