Connecticut CTDPA: Cookies Policy
The Connecticut Data Privacy Act (CTDPA, Public Act No. 22-15) has two specific requirements for sites that process personal data for targeted advertising or sell personal data.
This page covers one piece of the picture. For the full scope of the CTDPA — who must comply, the thresholds, the consumer rights and the penalties — start with our complete guide to the CTDPA and cookies.
The first is immediate: a clear and conspicuous link on the site to an opt-out page.
The second took effect on January 1, 2025: the obligation to honor opt-out signals sent by platforms, technologies, or mechanisms with consumer consent, such as the Global Privacy Control (GPC).
This article focuses exclusively on what the CTDPA requires from a Cookies Policy: what must be in the document, how consent and opt-out must work, and what the law's specific requirements mean for each tracker on your site.
The cookie banner is the visual consent interface. It is what the visitor sees when they first access the site.
The Cookies Policy is the detailed document. It is where the user finds complete information about each technology: what it collects, what it is for, who receives the data, and how to exercise rights.
Both need to exist. Both need to be aligned. And the Cookies Policy must be accessible from a clear link within the consent notice itself.
Section 6(a)(1) requires the controller to limit collection to what is adequate, relevant, and reasonably necessary for the disclosed purposes. And Section 6(c)(2) requires the purpose to be in the privacy notice.
For cookies, each tracker category needs a specific purpose description, not a generic one.
What does not work: "cookies to improve your experience."
What works: "Analytics cookies: collect browsing behavior data including pages visited, traffic source, and session duration. Used to identify content improvement opportunities. Data is not sold or used for targeted advertising."
"Advertising cookies: collect behavioral identifiers shared with advertising platforms for targeted advertising on non-affiliated websites. Include pixels from Meta Ads and Google Ads. Consumers may exercise opt-out via the opt-out link on this page."
The Policy must list tracker categories:
Necessary cookies: essential for basic functionality. Do not constitute targeted advertising or data sale. Must be documented but do not require opt-out.
Analytics cookies: depends on configuration. If data stays internal, generally does not constitute targeted advertising. If sent to third parties for targeting on other sites, may qualify.
Advertising cookies: almost always constitute "targeted advertising" under the CTDPA, which defines it as ads based on data "obtained or inferred from the consumer's activities over time and across nonaffiliated Internet web sites or online applications" (Section 1(28)).
Functional cookies: remember preferences. Generally do not constitute targeted advertising or sale.
Third-party cookies: fired by external services. Correct tag categorization is what makes accurate documentation possible.
The CTDPA defines targeted advertising (Section 1(28)) as displaying ads based on personal data obtained or inferred from the consumer's activities over time and across nonaffiliated Internet web sites or online applications.
What does not constitute targeted advertising:
Advertisements based on activities within the controller's own websites or online applications.
Advertisements based on the context of a current search query or visit.
Advertisements directed to a consumer in response to an information request.
Processing personal data solely to measure or report advertising frequency, performance, or reach.
Retargeting campaigns using behavioral data from other sites therefore almost always constitute targeted advertising under the CTDPA.
The CTDPA defines sale (Section 1(26)) as the exchange of personal data for monetary or other valuable consideration by the controller to a third party.
Not a sale: disclosure to processors, disclosure for products/services requested by the consumer, disclosure to affiliates, consumer-directed disclosure, publicly made available data, and M&A transfers.
If the site shares data with partners in exchange for services or other economic benefits, it may constitute a sale even without direct cash payment.
The Policy must identify the categories of third parties receiving data via cookies (Section 6(c)(5)).
This includes digital advertising platforms, analytics tools, programmatic advertising networks, email marketing platforms receiving behavioral data, and any other partner receiving identifiers or user behaviors collected via cookie.
The obligation to limit collection to what is necessary (Section 6(a)(1)) implies data should also be retained only for as long as necessary. The Cookies Policy must document how long each cookie category stays active and how long data is retained in systems.
Section 6(e)(1)(A)(i) requires a clear and conspicuous link on the controller's website to a page enabling the consumer or their agent to opt out of targeted advertising or sale of personal data.
This link must be visible on the page, not in obscure locations. The Cookies Policy must identify this link and describe how the opt-out works.
Section 6(e)(1)(A)(ii) requires that from January 1, 2025, controllers processing for targeted advertising or selling data allow opt-out via signal sent with consumer consent.
In practical terms for cookies: when a user visits the site with the GPC activated in their browser, the site must interpret this signal as an opt-out of targeted advertising and data sale, and automatically block the corresponding trackers.
The mechanism must meet CTDPA-specific requirements (Section 6(e)(1)(A)(ii)):
Cannot unfairly disadvantage another controller.
Cannot be a default setting: must represent an affirmative, freely given, and unambiguous consumer choice.
Must be consumer-friendly and easy for the average consumer.
Must be as consistent as possible with similar mechanisms required by other laws.
Must enable the controller to accurately determine whether the consumer is a Connecticut resident.
When the opt-out signal conflicts with an existing controller-specific setting or loyalty program participation, the controller must comply with the signal but may notify the consumer of the conflict and give them the option to confirm their prior preference.
The Cookies Policy must describe how the site processes these signals.
Section 1(6) defines consent as a clear affirmative act signifying a consumer's freely given, specific, informed, and unambiguous agreement.
What is not valid consent:
Accepting general terms with data processing descriptions alongside unrelated information.
Hovering over, muting, pausing, or closing a piece of content.
Any agreement obtained through dark patterns.
Dark patterns are defined in Section 1(11) as interfaces designed or manipulated with the substantial effect of subverting or impairing user autonomy, decision-making, or choice, including any practice the FTC refers to as a dark pattern.
The correct standard for cookies: non-essential cookies off by default. The user chooses what to enable, not what to disable.
If the user granted consent for non-essential cookies and then decides to revoke, Section 6(a)(6) requires the controller to:
Provide a revocation mechanism at least as easy as the consent mechanism.
Cease processing not later than 15 days after receiving the revocation.
This 15-day deadline is exclusive to the CTDPA and means the consent management platform must be configured to process revocations promptly, not just log them.
Section 6(a)(7) prohibits processing data of consumers aged 13 to 15 for targeted advertising or sale without their consent when the controller has actual knowledge of that age range.
If the site may have users in this range, the Cookies Policy must describe how advertising cookies are blocked for this audience and how consent is obtained when required.
The CTDPA does not specify a minimum privacy notice update frequency like the CCPA/CPRA does. But Section 6(a)(2) prohibits processing for purposes not disclosed without consent, and Section 6(a)(1) requires limiting collection to what is necessary for the disclosed purposes.
In practice, situations requiring a Cookies Policy update:
Adding a new advertising pixel or tracker.
New analytics tool sending data to third parties.
New partner receiving behavioral data.
Change in the use of cookie data for new purposes.
Any modification to opt-out mechanisms.
Continuous data mapping is what keeps the cookie inventory synchronized with the document.
Violations are treated as unfair trade practices by the Connecticut Attorney General. There is no private right of action.
From January 2025, the cure period is discretionary. The AG may act without a guaranteed prior correction period.
AdOpt's automatic scan identifies all active technologies on the site, feeding the list of categories that must appear in the Cookies Policy.
The cookie notice configured through AdOpt blocks non-essential trackers before acceptance, presents categories with clear descriptions, offers real opt-out options, detects and honors the GPC from January 2025, processes revocations within 15 days, and logs every interaction.
Over 60,000 websites already run with AdOpt.
Privacy is not a banner. It is a position.
Want to build a Cookies Policy for your site that complies with the CTDPA? Talk to our team.
Visible link in the footer and within the cookie banner.
Listing of cookie categories with a description of what each does.
Specific purpose for each category, without vague descriptions (Section 6(c)(2)).
Identification of cookies constituting targeted advertising or sale (Section 6(d)).
Categories of third parties receiving data via cookies (Section 6(c)(5)).
Clear and conspicuous link for opt-out of targeted advertising/sale on the site (Section 6(e)(1)(A)(i)).
Opt-out preference signal: description of how GPC is honored from January 2025 (Section 6(e)(1)(A)(ii)).
15-day consent revocation: mechanism and deadline described (Section 6(a)(6)).
Non-essential cookies disabled by default, without dark patterns (Section 1(11)).
Protection for teens aged 13 to 15 described where applicable (Section 6(a)(7)).
Retention period for each cookie category.
Active email address or online mechanism for contacting the controller (Section 6(c)(6)).
Accessible language, without legal jargon.
No cookie walls.
1. Is the CTDPA opt-out link different from the CCPA's "Do Not Sell" link?
They are similar in function but different in requirement. The CCPA requires specific link texts: "Do Not Sell or Share My Personal Information" and "Limit the Use of My Sensitive Personal Information." The CTDPA simply requires a clear and conspicuous link to an opt-out page for targeted advertising or data sale, without mandating specific text. Businesses that already have the CCPA links likely satisfy the CTDPA requirement, depending on the link's scope.
2. Is the CTDPA's opt-out preference signal the same as the GPC?
The GPC is the best-known mechanism meeting the CTDPA's technical specifications. The law does not name the GPC specifically, but the GPC was developed precisely for this type of legal requirement. As long as the mechanism is an affirmative consumer choice (not a default), does not create unfair disadvantage for the controller, and allows verification that the consumer is a Connecticut resident, it meets Section 6(e)(1)(A)(ii).
3. Does the 15-day consent revocation deadline apply to all cookies?
It applies when consent is the basis for processing. For advertising cookies where the consumer gave consent and then revokes it, Section 6(a)(6) requires cessation within 15 days. For opt-outs of targeted advertising or sale (which do not require prior consent but rather an opt-out mechanism), the law does not specify the 15-day deadline, but requires cessation as soon as practicable.
4. Do analytics cookies constitute targeted advertising under the CTDPA?
It depends on the tool and configuration. If analytics data stays internal or is sent to the provider only to generate reports without use for targeting on other sites, it generally does not qualify. If the tool sends data used for targeting on other sites, it may. The CTDPA's criterion is data "obtained or inferred from activities across nonaffiliated websites" (Section 1(28)).
5. Does the CTDPA require teens aged 13 to 15 to consent before any cookie?
Section 6(a)(7) is specific: it prohibits processing data of 13-to-15-year-olds for targeted advertising or sale without their consent. It does not require consent for other types of processing such as internal analytics. The restriction applies when the controller has actual knowledge of the user's age.
Ready to build a Cookies Policy for your site that complies with the CTDPA? Talk to our team.
Connecticut CTDPA compliance rests on documents that need to agree with each other: the privacy policy, which explains what you do with the data; the privacy portal, which is where the consumer exercises their rights and you keep the record of it.
Tags
Related posts
Florida FDBR and Cookies: All You Need to Know
Everything you need to know about the Florida Digital Bill of Rights (FDBR): who must comply, the $1 billion threshold, 7 consumer rights, FIPA vs FDBR explained, penalties, and cookies.

IOWA ICDPA and Cookies: All you need to Know
Iowa ICDPA explained: the longest response deadline of all US state privacy laws (90 days), 90-day cure period, opt-out for sensitive data, limited deletion scope, no right to correct, and how it compares to UCPA, VCDPA, and OCPA.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.

AdOpt CMP
AdOpt CMP: Google-certified consent platform with prior blocking, granular choices, encrypted logs, and GTM/Consent Mode
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.

Montana MTCDPA: Privacy Policy
Learn what your MTCDPA Privacy Policy must include after Montana's SB 297 amendments from the conspicuous "privacy" hyperlink and last-updated date requirements to sale disclosures, minor protections, and how to keep your notice operationally aligned with your stack.

Why Give Consent on Every Website I Visit?
Have you ever noticed that every time you sign up for a service to access information or register on a website for purchases, you need to give consent? If you're wondering why you have to give consent on every website you visit, you'll find the answer here.

7 Steps to GDPR-Compliant Cookie Banners in 2025
Learn the essential steps for creating GDPR-compliant cookie banners in 2025, ensuring user consent and privacy protection.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
LGPD: An Opportunity for Digital Marketing Agencies!
Have you ever thought that your marketing agency could find a great business opportunity in LGPD? Well, unlike what many think, it brings changes that can accelerate the demand for the services of these companies.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.
The Impact of Cookie Banners on Your E-commerce - LGPD
Having a cookie banner on your brand's website has become indispensable for many. However, for e-commerce websites, it has practically become an obligation to have one. This is because this type of website has a technological composition in which cookies are a structural part. Login flow, items in the shopping cart, recommendation showcases, remarketing... Most of them rely on cookies.
Colorado CPA and Cookies: All You Need to Know
The Colorado Consumer Privacy Act went into effect July 1, 2023 (CPA). CPA is a vital piece of legislation designed to protect the privacy of residents in Colorado. Understanding its requirements is essential for any business operating in the state. This act is all about giving control back to the consumers regarding their personal data. But what does this mean for you and your business, especially when it comes to managing cookies on your website?
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

Data Protection Officer and LGPD, a Solitary or Teamwork Job?
How do you deal with a profession that didn't even exist a few years ago and is now mandatory in companies? That's precisely the question that arises when we think of the figure of the Data Protection Officer or DPO.
10 Marketing Processes You Should Rethink under the LGPD!
In the end, our goal has never been to predict doom for companies or to be part of the LGPD's Apocalypse Cavalry. But, since we've been in the market for some time, these kinds of issues always catch our attention when we start data mapping and having conversations with colleagues.
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.

5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.

LGPD and Cookies all do you need to know?
In this article, you will have a great introduction to the topic, as well as various other variations that revolve around the subject: Cookies and LGPD.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.

California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.
Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Utah UCPA: Privacy Policy
What the Utah UCPA requires from your Privacy Policy: five mandatory elements, opt-out model for sensitive data, no retention periods required, no active contact channel mandate, and the guaranteed 30-day cure period.
California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
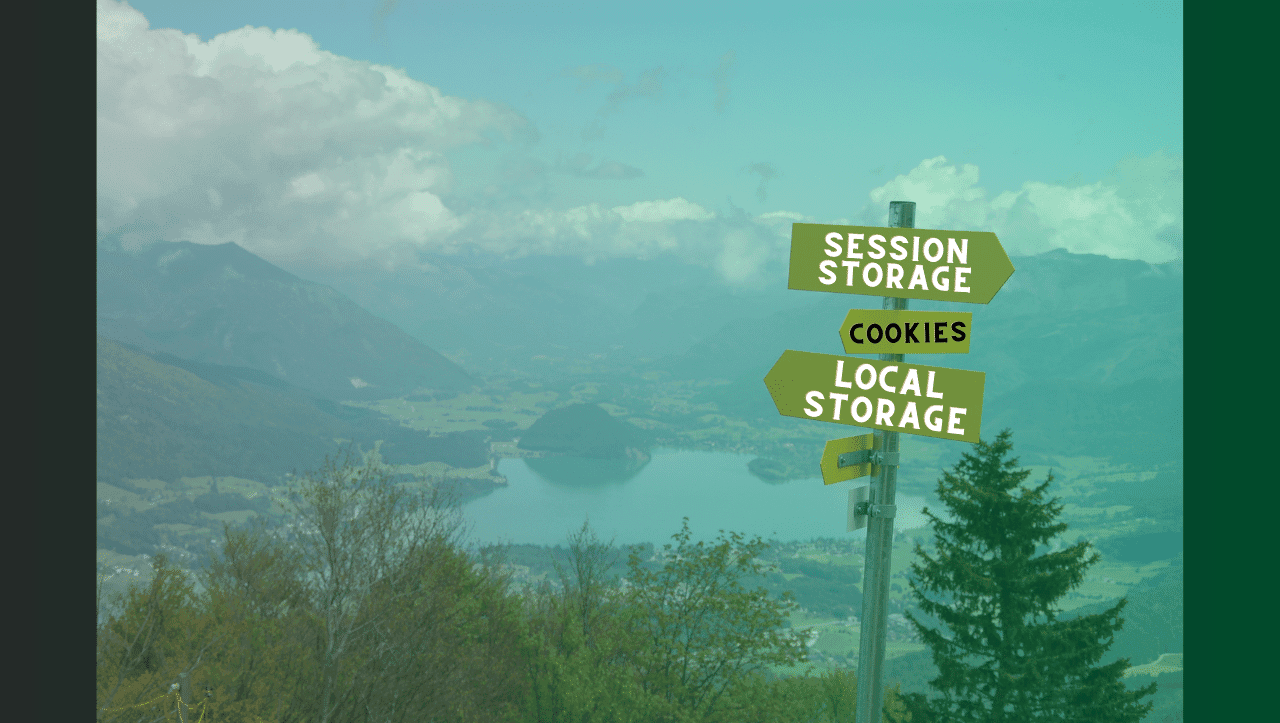
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
Explore AdOpt
Autor
João Bruno
09 Jun 2026
AdOpt


Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website


Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


