In today’s digital landscape, privacy is paramount. With regulations such as GDPR and LGPD, businesses must prioritize consent management to protect users and stay compliant, an effective Consent Management Platform (CMP) like AdOpt turns privacy from a blocker into part of the user experience: clear choices, [granular consent], and [encrypted consent logs] that prove compliance.
Look for a CMP that balances compliance and UX:
- Ease of use & quick setup (seamless with your design).
- [Granular consent controls].
- [Dashboards & reports] for consent rates and banner performance.
- Multi-language and multi-legislation support.
- Human support with SLAs by plan (no blanket “24/7” promise).
Different laws emphasize different rights, but the baseline is the same: transparency, choice, and evidence of consent, a robust CMP helps you implement prior blocking (non-essential tags wait for consent), offer opt-in/opt-out by category, and log consents securely.
Non-compliance can trigger enforcement actions and significant fines, a reliable CMP helps collect and manage consent correctly, reducing risk while preserving user trust.
- Customizable cookie banner (brand-aligned, accessible).
- [Granular consent] by purpose/category.
- Tag scanning & categorization to keep your inventory mapped.
- [Encrypted consent logs], audit trail, and versioning of policies.
- Reports & KPIs.
- Integrations with [Google Tag Manager (GTM)] and [Google Consent Mode].
- Multi-language and multi-legislation operation.
Beyond capturing consent, AdOpt offers actionable analytics to improve banner UX and increase legitimate consent rates without dark patterns.
Let users opt-in or opt-out of specific categories, that’s what we call “real consent” respecting preferences and complying with GDPR/LGPD.
Operate across regions with multi-jurisdiction support and standards such as TCF 2.4, Global Privacy Control (GPC) and, when relevant, Global Privacy Platform (GPP).
AdOpt uses encrypted storage for consent records and provides auditability to prove what was collected, when, and under which legal basis.
Your cookie banner is a UX component not just a compliance checkbox, with AdOpt, tailor layout, copy, and controls to your brand while keeping choices clear and symmetrical (“Accept all” / “Reject all” / “Customize”).
For publishers and advertisers, Google-certified CMP status and TCF 2.4 support help keep ad delivery compliant in regulated regions, aligning signals with platform requirements.
- Tag scanning & categorization for accurate grouping.
- Callbacks, webhooks and APIs to orchestrate consent across systems.
- Reports & KPIs to iterate on UX and compliance.
Check API compatibility, implementation paths GTM, direct tag, and customization options.
Look for independent reviews (e.g., G2 highlights on ease of use) and adoption at scale (e.g., trusted by 40,000+ sites worldwide).
Prior-block non-essential tags, ensure symmetry between Accept and Reject, and keep copy clear.
Use reports & KPIs to refine UX and improve consent quality over time.
Track consent rates, banner interactions, and opt-out requests, iterate continuously.
Integrate AdOpt with GTM and Consent Mode to respect consent state while keeping measurement and ads compliant.
Serve the right experience for GDPR, LGPD, and other regimes with localized copy and standards-based signaling TCF 2.4, GPC, GPP where applicable.
AdOpt CMP supports TCF 2.4, aligning vendor signaling and user choices in EEA/UK.
Respect GPC signals automatically to honor user preferences at the browser/extension level.
Install via Tray or WordPress plugins, or implement via GTM / direct tag / API.
- Assess your current setup (what scripts run, which are essential).
- Choose a brand-aligned design for the cookie banner.
- Implement granular consent (category/purpose).
- Use callbacks/webhooks/APIs to propagate consent.
- Test flows (accept/reject/customize + logging).
- Monitor KPIs and iterate on copy/UX.
- Stay updated on standards and platform requirements TCF 2.4, GPC and GPP.
A secure, elegant CMP that makes privacy part of your user experience not a roadblock.
Install now
**Talk to our team
A Consent Management Platform (CMP) informs, collects, and records user choices before non-essential tags fire.
With AdOpt CMP, you get prior blocking, granular consent, and encrypted consent logs to prove compliance while keeping UX smooth.
AdOpt supports multi-legislation scenarios (e.g., GDPR, LGPD) and industry standards like TCF 2.4, GPC, and where relevant GPP.
The goal: consistent, standards-based consent across regions.
Yes. AdOpt is a Google-certified CMP and supports TCF 2.4, aligning consent signaling for advertising in regulated regions (EEA/UK).
Yes. We integrate with Google Tag Manager and Google Consent Mode so tags respond to the user’s consent state, non-essential tags wait; essentials keep working.
A proper setup preserves eligibility while keeping you compliant, with Consent Mode and tag gating measurement adapts to consent without dark patterns.
Users can opt in/out by category/purpose (e.g., analytics, marketing), that’s “real consent”: clear options, symmetric Accept/Reject, and a Customize path.
AdOpt implements preventive blocking of non-essential scripts until consent is given, via GTM, direct tag, or API.
All consents are encrypted and timestamped, you have an audit trail and versioning for key documents, helping you demonstrate compliance over time.
Yes. Adjust layout, copy, and controls to your brand while keeping clarity and symmetry (Accept/Reject/Customize).
Yes. Serve localized copy and jurisdiction-appropriate flows across markets with standards-based signals (TCF 2.4, GPC, GPP where applicable).
Setup paths include GTM, direct tag, APIs/callbacks, and plugins for WordPress and Tray.
Dashboards show consent rates, banner interactions, and opt-outs. Use them to iterate on copy/UX and improve consent quality.
Yes. You can organize multiple properties and manage access permissions across teams.
AdOpt respects GPC signals automatically and supports GPP where relevant to your stack and regions.
Typical paths (GTM, plugin, or direct tag) are quick to deploy. Your team chooses the path that fits your stack.
You get human support with SLAs by plan. Need more? Talk to us about extended coverage options for critical operations.
Yes. Standards compliance (TCF 2.4, Consent Mode) helps publishers keep delivery compliant and brands maintain trustworthy measurement.
Choosing a Consent Management Platform (CMP) is about far more than showing a cookie banner. It’s about building transparency with your users and securing legal peace of mind for your business without sacrificing experience.
AdOpt is built to handle the technical and regulatory complexity for you prior blocking, granular consent, encrypted consent logs, and native integrations like GTM and Google Consent Mode so your team can focus on what truly matters: growth. See the NZN Group case for a real-world example, and read how Axeptio announced the acquisition of AdOpt in February 2025.
Trusted by 40,000+ sites worldwide, Google-certified as a CMP, and recognized on G2 for ease of use, your path to real compliance is one click away.
Start free and join the companies turning privacy into great experience.
Tags
Related posts
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.

California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
LGPD: An Opportunity for Digital Marketing Agencies!
Have you ever thought that your marketing agency could find a great business opportunity in LGPD? Well, unlike what many think, it brings changes that can accelerate the demand for the services of these companies.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
The Impact of Cookie Banners on Your E-commerce - LGPD
Having a cookie banner on your brand's website has become indispensable for many. However, for e-commerce websites, it has practically become an obligation to have one. This is because this type of website has a technological composition in which cookies are a structural part. Login flow, items in the shopping cart, recommendation showcases, remarketing... Most of them rely on cookies.
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

Key Differences between LGPD and GDPR and the Impact on Internet Cookies
While both regulations share the goal of safeguarding individuals' rights regarding the processing of their personal data, there are some important differences between them. It is crucial to understand these distinctions and their implications, particularly in the context of internet cookies.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.

IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.

How to Choose a CMP (Consent Management Platform)?
Using a CMP (Consent Management Platform) is a great way to make efforts to adapt to new privacy regulations like GDPR, LGPD, DPDPA, CCPA and more...
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.
California CCPA and Cookies: All You Need to Know
Everything about the California CCPA and CPRA: who must comply, the $25M threshold, 7 consumer rights, CCPA vs CPRA explained, the Do Not Sell link, CPPA enforcement, and cookies.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Understand the meaning of the LGPD for your company
Surely you've already seen the predictions of fines and sanctions, processes. But, what does it mean to your company?
New Hampshire NHDPA and Cookies: All you need to know
Discover what the New Hampshire Privacy Act (NHDPA) means for your business. Learn about compliance steps, consumer rights, penalties, and how to simplify it all with AdOpt, a Google-certified CMP.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?
New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.

What are Terms of Use and their importance for the LGPD?
Ignoring Terms of Use and their significance within a website, particularly now with LGPD, is a common mistake that both consumers and website owners frequently commit.
Tenesse TIPA: Privacy Policy
Learn what your TIPA Privacy Policy must include to comply with the Tennessee Information Protection Act from consumer rights and targeted advertising disclosures to the NIST affirmative defense, appeal mechanisms, and how to keep your notice aligned with your operational program.

What is the ideal privacy policy for your company?
Is there an ideal and _foolproof_ Privacy Policy? This is one of the most difficult questions to answer nowadays. Especially considering all the jurisprudence already established in Europe with the GDPR, the extensive history of cases, and the numerous tips we see in the market. Not to mention the judicial decisions that are already emerging in Brazil with the LGPD.

Montana MTCDPA: Cookies Policy
Learn about how to apply Montana MTCDPA Cookies Policy in your site
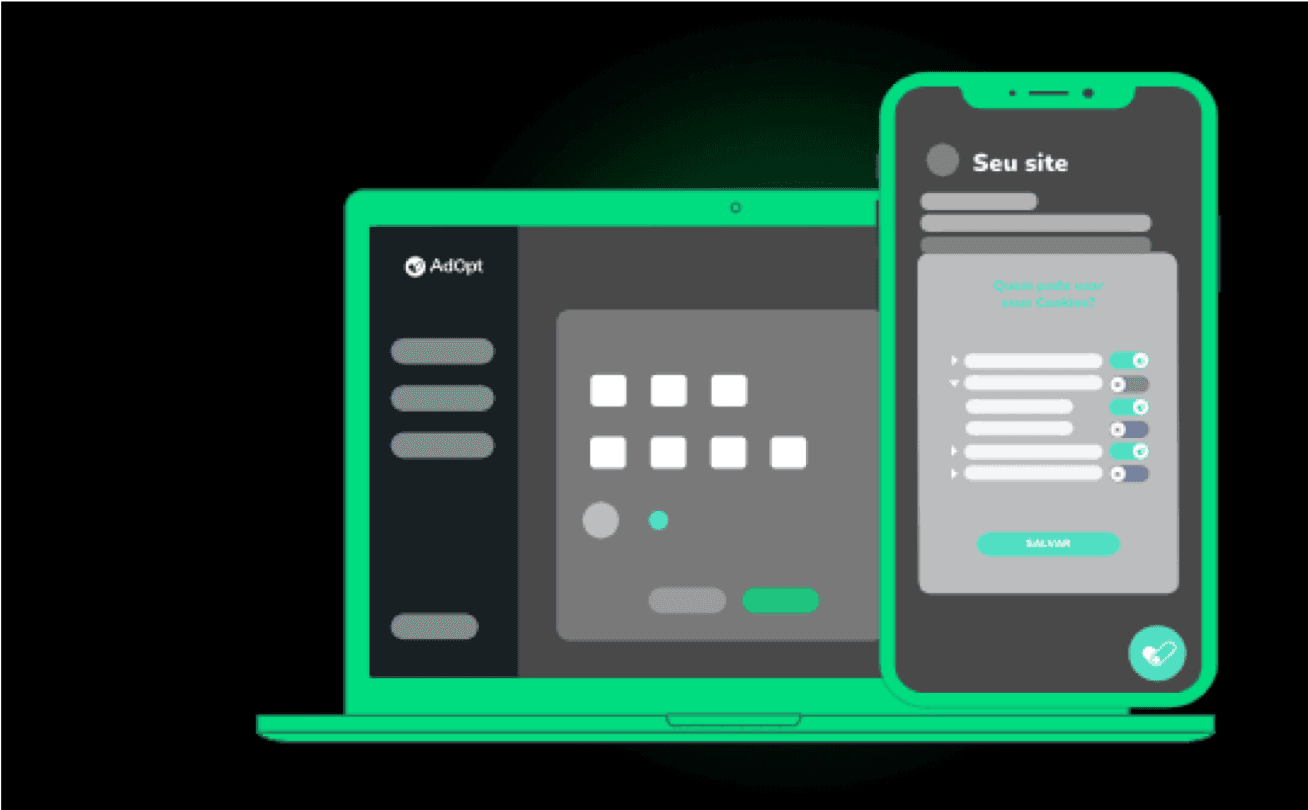
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.
Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
Tennessee TIPA and Cookies: All You Need to Know
If you're looking to understand how this law impacts businesses in Tennessee, especially those dealing with digital cookies, you're in the right place. This article will simplify the complexities of compliance and make them easy to grasp, even if you're just starting to learn about data privacy.
California CPRA and Cookies: All you need to know
California CPRA explained: CCPA vs CPRA timeline and key differences, sensitive personal information, sharing of data, CPPA enforcement, GPC requirement, and tripled penalties for minors.

How to delete cookies and cache in Chrome and other browsers?
Tired of the ads from that site you visited following you around? Is your computer running slow when accessing a particular website? Want to delete all cookies from a specific service or site?
Oregon OCPA: DSAR Privacy Portal
Oregon OCPA DSAR guide: the L.O.C.K.E.D. rights, opt-out without authentication, derived data in deletion scope, 15-day revocation deadline, GPC from January 2026, and the elimination of the cure period.
Explore AdOpt
Autor
João Bruno
27 Apr 2026
AdOpt


Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Oregon OCPA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website


Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


