Florida FDBR and Cookies: All You Need to Know
Florida has not one, but two laws relevant to anyone handling data from state consumers.
And understanding the difference between them is the first step in knowing whether your business falls within the scope of each one.
The Florida Digital Bill of Rights (FDBR), Part V of Chapter 501 of the Florida Statutes (§§ 501.701 to 501.721), came into effect on July 1, 2024. It is the most selective comprehensive data privacy law in the United States: it applies exclusively to companies with global annual revenues exceeding US$ 1 billion that meet specific digital business criteria.
If you have never heard of the FDBR, it probably does not apply to your business. But if it does, you need to know it very well.
When it comes to data privacy in Florida, two names come up frequently: FDBR and FIPA. They coexist, but they regulate different things and have completely different application scopes.
The Florida Information Protection Act (FIPA), codified at § 501.171 of the Florida Statutes, was enacted in 2014. It is a data security and breach notification law, not a comprehensive privacy law in the style of the GDPR or Brazil's LGPD.
FIPA applies to any business, government agency, or individual that maintains personal information of Florida residents in electronic format. The scope is broad: if you have names, Social Security numbers, bank account numbers, health information, or other personal data of Florida residents stored digitally, FIPA applies.
The main FIPA obligations are:
Implement reasonable security measures to protect personal data from unauthorized access.
Notify affected consumers of a data breach within 30 days of discovery.
Notify the Florida Department of Legal Affairs if more than 500 consumers are affected.
Notify national credit reporting agencies if more than 1,000 consumers are affected.
Penalties for delayed notification reach US$ 500,000.
FIPA does not grant rights of access, correction, or deletion. It deals with security and transparency after incidents, not with active control by data subjects over their data.
The Florida Digital Bill of Rights is a comprehensive privacy law modeled on modern legislation. It guarantees rights to Florida consumers, creates compliance obligations for businesses that process their data, and establishes enforcement mechanisms.
The fundamental difference: the FDBR has an extremely high applicability threshold. It applies only to businesses with global revenues exceeding US$ 1 billion that operate in specific digital business sectors.
A company may be subject to both simultaneously. If a Big Tech company with a Florida presence suffers a data breach, FIPA governs the notification process. The FDBR governs everything that happens before: how data is collected, processed, and what rights consumers have over it.
| Feature | FIPA (2014) | FDBR (2024) |
|---|---|---|
| Scope | Any business with Florida residents' data | Companies with US$ 1B+ global revenue |
| Focus | Security and breach notification | Consumer rights + data processing |
| Main obligations | Technical security + 30-day notification | 7 consumer rights + 9 controller duties |
| Penalties | Up to US$ 500K for delayed notification | Up to US$ 50K/violation (triplicable) |
| Private right of action | No | No |
The Florida Digital Bill of Rights is Florida's state-level personal data protection law. It may be cited as the "Florida Digital Bill of Rights" under § 501.701 and forms Part V of Chapter 501 of the Florida Statutes.
The law creates a framework of rights and obligations focused on transparency, consent, and data control. If you are already familiar with the LGPD or the GDPR, the general structure will be familiar. What distinguishes it is the extremely selective applicability threshold.
Enforcement is the responsibility of the Florida Department of Legal Affairs. There is no private right of action.
On July 1, 2024.
The FDBR's applicability threshold is the most restrictive among all US state privacy laws.
Under § 501.703 and § 501.702(9), the law applies to controllers that:
1. Conduct business in Florida or produce products or services used by Florida residents.
2. Process or engage in the sale of personal data.
3. Are organized for profit or the financial benefit of their shareholders or owners.
4. Generate more than US$ 1 billion in global gross annual revenues.
5. Meet at least one of the following additional criteria:
Derive 50% or more of global gross annual revenues from the sale of online advertisements, including targeted advertising or the sale of ads online.
Operate a consumer smart speaker with a voice command component and integrated virtual assistant connected to a cloud computing service.
Operate an app store or digital distribution platform with at least 250,000 different software applications available for download.
In practice, the FDBR was designed to reach companies like Google, Meta, Amazon, and Apple. Smaller businesses, even if they operate in Florida and handle data of Florida residents, are not within the FDBR's scope (but may be within FIPA's scope).
Under § 501.703(2), the following are exempt:
State agencies and political subdivisions of the state.
Financial institutions regulated by the Gramm-Leach-Bliley Act (Title V).
Covered entities and business associates regulated by HIPAA.
Nonprofit organizations.
Postsecondary education institutions receiving state funds.
There are also exemptions for HIPAA-protected data, FERPA-regulated data, Fair Credit Reporting Act data, Driver's Privacy Protection Act data, Farm Credit Act data, employee and job applicant data, and short-term transactional payment processing data.
Under § 501.702(19), personal data is any information, including sensitive data, linked or reasonably linkable to an identified or identifiable individual. It also includes pseudonymous data when used in conjunction with additional information that reasonably links the data to an individual.
De-identified data and publicly available information are excluded.
Under § 501.702(31), sensitive data includes:
Personal data revealing racial or ethnic origin, religious beliefs, mental or physical health diagnosis, sexual orientation, or citizenship or immigration status.
Genetic or biometric data processed to uniquely identify an individual.
Personal data collected from a known child.
Precise geolocation data (within 1,750 feet).
The FDBR has a specific and important definition of "known child" (§ 501.702(17)): any individual under 18 years of age of whose age the controller has actual knowledge or willfully disregards. This is a higher threshold than most US laws, which use 13 years.
The FDBR guarantees seven rights to Florida residents, two more than most US state privacy laws. Under § 501.705(2):
Right to access and confirmation: knowing whether the controller processes their data and obtaining a copy in an accessible format.
Right to correction: correcting inaccuracies in personal data, considering the nature of the data and the purposes of processing.
Right to deletion: requesting deletion of any or all data provided by or obtained about the consumer.
Right to portability: obtaining a copy of data in a portable and, where technically feasible, readily usable format, if the data is available in a digital format.
Right to opt-out of targeted advertising, data sale, and profiling with legal or similarly significant effects.
Right to opt-out of collection of sensitive data, including precise geolocation data, or processing of sensitive data.
Right to opt-out of collection of data via voice recognition or facial recognition features.
The seventh right, related to voice and facial recognition, is exclusive to the FDBR among US state privacy laws.
§ 501.705(3) goes beyond opt-out rights and explicitly prohibits devices with voice recognition, facial recognition, video recording, audio recording, or other electronic, visual, thermal, or olfactory data collection features from being used for surveillance when not in active use by the consumer, unless the consumer has expressly authorized it.
Under § 501.706, the controller must respond without undue delay, no later than 45 days after receipt of the request.
The deadline can be extended once by 15 additional days (not 45 like other laws) when reasonably necessary, as long as the consumer is notified within the initial period with the reason.
After fulfilling the request, the controller must provide notice to the consumer within 60 days confirming compliance (§ 501.706(4)).
Service is free at least twice per year per consumer. For manifestly unfounded, excessive, or repetitive requests, the business may charge a reasonable fee or decline, but bears the burden of demonstrating the excessive nature.
§ 501.709 requires the controller to establish two or more methods for consumers to submit requests. This is unique among US state privacy laws.
The methods must be secure, reliable, and clearly and conspicuously accessible. A mechanism on the controller's own website is mandatory. Online-only businesses with a direct consumer relationship may additionally accept requests by email.
The business cannot require consumers to create a new account to exercise their rights.
Under § 501.702(7), consent is a clear affirmative act signifying a consumer's freely given, specific, informed, and unambiguous agreement.
What is not valid consent: accepting general terms that contain data processing descriptions alongside unrelated information, hovering over or closing content, and any agreement obtained through dark patterns.
Dark patterns are defined in § 501.702(11) as interfaces designed with the substantial effect of subverting or impairing user autonomy, decision-making, or choice, including any practice the FTC refers to as a dark pattern.
Under § 501.71, the controller must:
Limit data collection to what is adequate, relevant, and reasonably necessary for the disclosed purposes.
Implement reasonable technical, administrative, and physical data security practices proportionate to the volume and nature of the data.
Not process data for purposes incompatible with those disclosed, except with consumer consent.
Not process data in violation of anti-discrimination laws.
Not discriminate against consumers who exercise their rights.
Not process sensitive data of consumers without prior consent, or for known children between 13 and 18, without their affirmative authorization, or following COPPA for children under 13.
For search engine operators: make available a plain language description of main ranking parameters, including whether political partisanship or ideology is prioritized or deprioritized in search results.
The FDBR defines targeted advertising (§ 501.702(33)) as ads based on data from consumer activities over time across affiliated or unaffiliated websites and online applications.
This differs from most other state privacy laws. The VCDPA, for example, covers only non-affiliated websites. The FDBR includes affiliated ones, meaning that trackers operating within the ecosystem of companies in the same corporate group may constitute targeted advertising under the FDBR.
§ 501.702(29) defines sale of personal data as sharing, disclosing, or transferring for monetary or other valuable consideration. This is broader than the VCDPA, which mentions only monetary consideration. A company that exchanges user data with partners in return for services, technology, or other benefits may be conducting a "sale" under the FDBR.
§ 501.711 requires the controller to provide a reasonably accessible and clear privacy notice updated at least annually.
Beyond common content elements, the FDBR requires specific notices when the controller sells sensitive or biometric data. If the site sells sensitive data, it must display: "NOTICE: This website may sell your sensitive personal data." If it sells biometric data: "NOTICE: This website may sell your biometric personal data."
§ 501.719(3) requires adoption of a retention schedule that prohibits use or retention of personal data after:
The fulfillment of the initial purpose of collection.
The expiration or termination of the contract.
2 years after the consumer's last interaction with the controller.
This explicit 2-year limit is specific to the FDBR and sets it apart from most other US state privacy laws.
Under § 501.72, violations of the FDBR are treated as unfair and deceptive trade practices. Civil penalties reach up to US$ 50,000 per violation, significantly higher than other state laws like the VCDPA (US$ 7,500) and NHDPA (US$ 10,000).
Penalties may be tripled for:
Violations involving a known Florida child (a controller that willfully disregards age is deemed to have actual knowledge of it).
Failure to delete or correct data after an authenticated consumer request.
Continuing to sell or share a consumer's data after they opt out.
The Department may grant a 45-day cure period, but it is discretionary, not guaranteed. For violations involving children, there is no cure period available.
If you do not exceed US$ 1 billion in global revenue and do not operate an app store, smart speaker, or large-scale online advertising platform, the FDBR likely does not apply. But FIPA still may.
Understand what you collect, for what purpose, how it is used, and with whom it is shared. Data mapping is the foundation of any compliance program.
The FDBR requires at least two secure and accessible methods for consumers to submit requests.
Annual updates are mandatory by law. Include the specific notices required when selling sensitive and biometric data.
The two additional FDBR rights need structured exercise channels.
Data must be deleted after 2 years from the consumer's last interaction, except for the legal exceptions.
If your business operates devices with voice or camera features, ensure they do not collect data when not in active use without express consumer authorization.
Applying privacy by design from product conception is what makes compliance sustainable.
AdOpt records every consent interaction, blocks trackers before acceptance, and generates the auditable log needed in a Department of Legal Affairs investigation.
The automatic scan identifies all active trackers on the site, feeding the data inventory required for the privacy notice and the Data Protection Assessments. And when the law changes, the platform updates automatically.
Over 60,000 websites already run with AdOpt.
Privacy is not a banner. It is a position.
Ready to bring your website into compliance with the FDBR? Talk to our team.
| Law | State | Threshold | Penalty | Cure Period | Effective Date |
|---|---|---|---|---|---|
| FDBR | Florida | US$ 1B+ global revenue | Up to US$ 50K/violation (triplicable) | 45 days (discretionary) | Jul 2024 |
| VCDPA | Virginia | 100K or 25K + 50% revenue | Up to US$ 7,500/violation | 30 days guaranteed | Jan 2023 |
| NHDPA | New Hampshire | 35K or 10K + 25% revenue | Up to US$ 10K/violation | Discretionary (2026) | Jan 2025 |
| TDPSA | Texas | 25K residents | Up to US$ 7,500/violation | 30 days | Jul 2024 |
| CPA | Colorado | 100K or 25K + 50% revenue | Up to US$ 20K/violation | Discretionary (2025) | Jul 2023 |
To understand how these privacy laws compare in terms of structure and practical impact, our comparative guide goes deeper on the subject.
Compliance with the FDBR rests on three documents that have to agree with each other: the cookies policy, which declares every tracker and its purpose; the privacy policy, which explains what you do with the data; and the privacy portal, where the consumer exercises their rights and you keep the record of it.
1. What is the difference between the FDBR and FIPA?
FIPA (2014) is a data security and breach notification law that applies to any business maintaining data of Florida residents. The FDBR (2024) is a comprehensive consumer rights law that applies only to businesses with more than US$ 1 billion in global revenue operating in specific digital technology sectors. A company may be subject to both simultaneously: FIPA governs what happens after a data breach, and the FDBR governs how data is collected, processed, and what rights consumers have over it.
2. Who is actually within the scope of the FDBR?
In practice, the FDBR was designed to reach Big Tech companies such as Google, Meta, Amazon, and Apple. The US$ 1 billion global revenue threshold combined with the additional requirements (online advertising, smart speakers, or app stores with 250K apps) excludes the vast majority of businesses from the scope. Smaller businesses that handle data of Florida residents remain subject to FIPA for security and breach notification matters (§ 501.702(9)).
3. What are the rights exclusive to the FDBR that other laws do not have?
The FDBR guarantees seven rights, two of which are exclusive: the right to opt out of collection of sensitive data (including precise geolocation) and the right to opt out of data collection via voice or facial recognition features (§ 501.705(2)(f) and (g)). The device surveillance prohibition when not in active use is also a requirement exclusive to the FDBR.
4. What are the penalties for non-compliance with the FDBR?
The Department of Legal Affairs may impose civil penalties of up to US$ 50,000 per violation, triplicable for violations involving known children, failure to delete or correct data after an authenticated request, and continued sale of data after consumer opt-out. The 45-day cure period is discretionary, not guaranteed, and does not apply to violations involving children (§ 501.72).
5. How does the FDBR define targeted advertising differently from other laws?
The FDBR (§ 501.702(33)) defines targeted advertising as ads based on data from consumer activities over time across affiliated or non-affiliated websites, making it broader than the VCDPA which only covers non-affiliated websites. Additionally, the "sale" definition in the FDBR includes non-monetary valuable consideration, while the VCDPA mentions only monetary consideration.
Ready to bring your website into compliance with the FDBR? Talk to our team.
Tags
Related posts
5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.

Connecticut CTDPA: Cookies Policy
What the Connecticut CTDPA requires from your Cookies Policy: opt-out link, opt-out preference signal from January 2025, 15-day consent revocation, teen protections, and targeted advertising definition.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?

California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

Why Give Consent on Every Website I Visit?
Have you ever noticed that every time you sign up for a service to access information or register on a website for purchases, you need to give consent? If you're wondering why you have to give consent on every website you visit, you'll find the answer here.

New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.
The Impact of Cookie Banners on Your E-commerce - LGPD
Having a cookie banner on your brand's website has become indispensable for many. However, for e-commerce websites, it has practically become an obligation to have one. This is because this type of website has a technological composition in which cookies are a structural part. Login flow, items in the shopping cart, recommendation showcases, remarketing... Most of them rely on cookies.

California CPRA and Cookies: All you need to know
California CPRA explained: CCPA vs CPRA timeline and key differences, sensitive personal information, sharing of data, CPPA enforcement, GPC requirement, and tripled penalties for minors.

MTCDPA Montana and Cookies: All you need to know
Find out if the MTCDPA applies to your site, key compliance deadlines, and new rules for cookies and consent in Montana
Montana MTCDPA: Privacy Policy
Learn what your MTCDPA Privacy Policy must include after Montana's SB 297 amendments from the conspicuous "privacy" hyperlink and last-updated date requirements to sale disclosures, minor protections, and how to keep your notice operationally aligned with your stack.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.
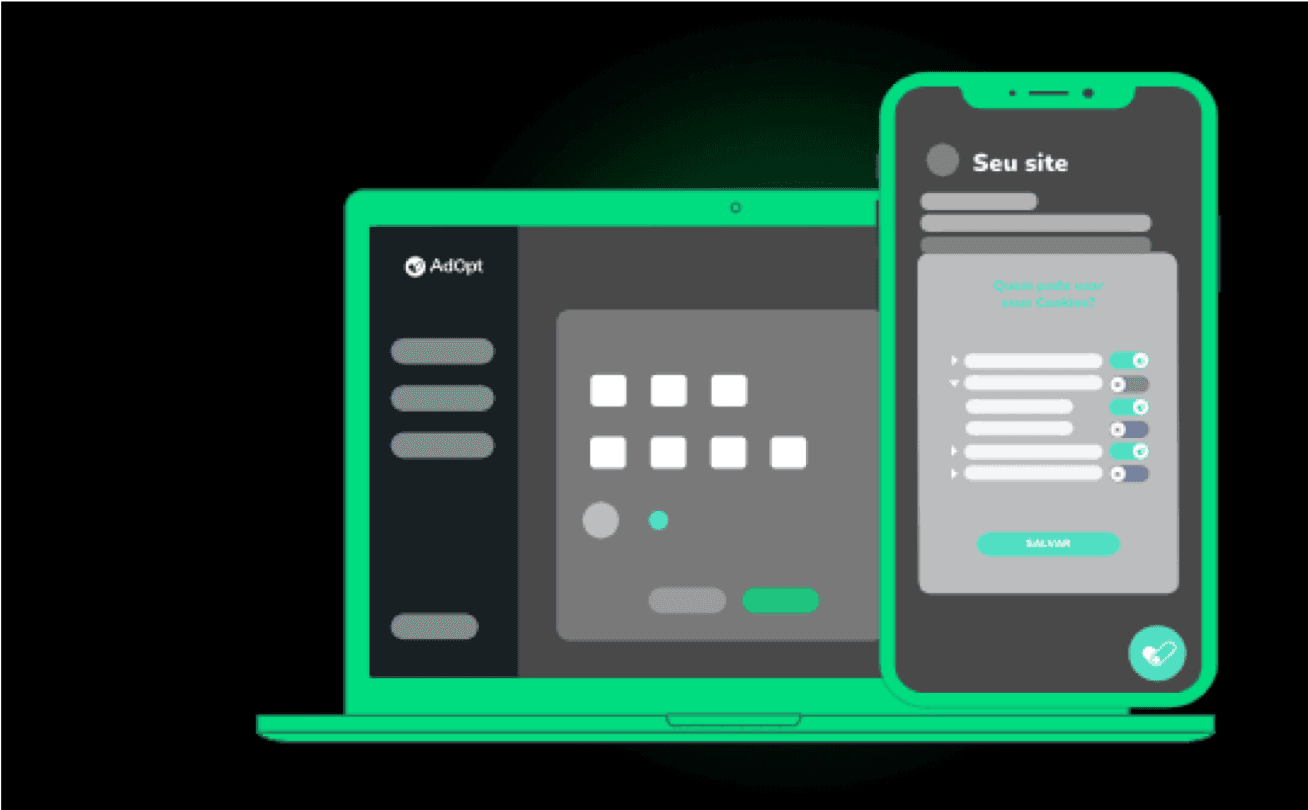
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.

Texas TDPSA: Privacy Policy
The Texas Data Privacy and Security Act (TDPSA) introduces sweeping changes to how businesses collect, use, and disclose personal data—and your privacy policy is now a frontline compliance tool. This article is a comprehensive guide for any company serving Texas residents, explaining how to align your privacy practices with the new legal standards.
New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

California CPRA: Privacy Policy
What the California CPRA requires from your Privacy Policy: SPI category, two mandatory links, data retention periods, sharing disclosure, right to correct, GPC, and minor protections.
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.
Colorado CPA and Cookies: All You Need to Know
The Colorado Consumer Privacy Act went into effect July 1, 2023 (CPA). CPA is a vital piece of legislation designed to protect the privacy of residents in Colorado. Understanding its requirements is essential for any business operating in the state. This act is all about giving control back to the consumers regarding their personal data. But what does this mean for you and your business, especially when it comes to managing cookies on your website?
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.
Colorado CPA: Privacy Policy
What the Colorado CPA requires from your Privacy Policy: 5 mandatory elements, purpose specification duty, secondary use prohibition, 24-month consent refresh, and Universal Opt-Out Mechanism disclosure.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.
California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.
Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!

California CPRA: Cookies Policy
What the California CPRA requires from your Cookies Policy: the sharing concept, GPC as valid opt-out, Do Not Sell or Share link, SPI geolocation, minor protections, and retention periods.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
New Hampshire NHDPA: Cookies Policy
Cookies Policy under NHDPA explained. Discover what's mandatory, dark patterns to avoid, and how to implement legal cookie consent.

Virginia VCDPA and Cookies: All you need to know
Everything you need to know about the Virginia Consumer Data Protection Act (VCDPA): who must comply, consumer rights, cookie requirements, penalties, and how to get your site in compliance.
Tenesse TIPA: Privacy Policy
Learn what your TIPA Privacy Policy must include to comply with the Tennessee Information Protection Act from consumer rights and targeted advertising disclosures to the NIST affirmative defense, appeal mechanisms, and how to keep your notice aligned with your operational program.

Utah UCPA: Privacy Policy
What the Utah UCPA requires from your Privacy Policy: five mandatory elements, opt-out model for sensitive data, no retention periods required, no active contact channel mandate, and the guaranteed 30-day cure period.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.
Explore AdOpt
Autor
João Bruno
12 Jun 2024
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


