5 Common Cookie Consent Mistakes Hurting Your Compliance
Compliance doesn't have to be a nightmare, whether you are a marketing professional or a Data protection officer, making simple mistakes can easily ruin your brand's reputation.
Facing million-dollar fines and losing user trust are the biggest risks today. Everything starts with how you manage cookies at the front door of your website.
We are here to simplify this for you. Let's dive into the five biggest market mistakes and how a solid Cookie notice/banner solves this on autopilot.
The global privacy landscape is changing extremely fast. Because of that, knowing if your website needs cookie consent is no longer a choice, it's a mandatory rule.
Tech giants have paid millions in fines just for ignoring basic transparency and data tracking guidelines.
The good news is that you don't need to pause your operations. Our technology protects everything, from your blog to your e-commerce, without any headaches.
Common Issue: Unclear Cookie Banner Text
Many businesses rely on cookie consent notices filled with confusing or vague language. Here are some common pitfalls:

Using technical jargon or generic text only pushes visitors away. Global laws like the LGPD demand total clarity and transparency in your communication.
Pre-made phrases like "we use technologies to improve your experience" mean absolutely nothing. You need to clearly explain the true role of cookies on your page.
The solution is a colloquial and direct language. A great Cookie banner must detail the collection purposes without sounding like a boring contract.
Hiding the reject button in difficult menus is a dark pattern that generates heavy fines in Europe and the Americas.
Your visitor must have the exact same ease to accept or reject tracking. This balance is the core of why a website needs cookie consent.
Avoid buttons with muted colors or tiny fonts. Let your Data protection officer validate the interface to ensure no deceptive patterns exist.

This is the fatal error that destroys many traffic managers' strategies. Loading tracking scripts before the "accept" click is a clear violation of the LGPD and GDPR.
The golden rule is: block everything that isn't strictly essential. You do not want marketing tools and cookies running without the user's green light.
To be sure your site is running clean, instruct your tech team to delete cookies and simulate accesses as a first-time visitor.
A beautiful banner is useless if you don't store the logs correctly. Remember that a proper website needs cookie consent involves keeping safe proof of actions.
During an audit, your company and the Data protection officer will need to present data such as date, time, and exact user preferences.
Losing this information leaves your operation completely vulnerable. A lack of documentation is a direct shortcut to fines that can shut down your business.
The era of assuming a user agreed just by scrolling the page is over. Modern frameworks like the LGPD strictly prohibit implied consent.
Pre-checked boxes or forced cookie walls are not allowed. The power of choice regarding cookies must be actively in the hands of the visitor.
Respecting this autonomy builds a much stronger brand perception. At the end of the day, it increases trust in your e-commerce and brings qualified leads.
Adapting your marketing processes doesn't have to be ugly or exhausting. Our CMP technology resolves your Cookie notice/banner installation in a few clicks.
With our platform, script blocking happens automatically, protecting your campaigns and mitigating 100% of the risk of fines from improper tracking.
We keep the entire consent history encrypted and organized. It's the security your Data protection officer needs, with the design your brand deserves.
Ignoring permission tracking is a critical compliance error that directly hurts your business. If you receive international traffic, knowing exactly why your website needs cookie consent is the first step to avoiding penalties and protecting your brand.
Absolutely not, as modern privacy rules require affirmative action. Strict frameworks, like the LGPD and GDPR, prohibit implied consent, ensuring the visitor has total control over their data.
Making it hard to refuse trackers is a deceptive practice highly penalized by regulatory authorities. Besides destroying user trust, this flaw attracts heavy financial fines that can cripple your company's budget.
Exactly, because no advertising or marketing script should be fired in the browser without prior authorization. Our AdOpt platform blocks these tags before the visitor interacts with the Cookie banner, doing all the heavy lifting for you.
While the tech team handles the installation, the responsibility for keeping records secure falls on managers and the Data protection officer. These professionals use our automated reports to prove legality during an audit.
Don't let bureaucratic mistakes harm your LGPD e-commerce performance or your agency's metrics.
Compliance technology doesn't have to be an expensive and complex hurdle, and we are ready to show you how fast and smooth it can be.
Book a free demo with our team of experts right now through our HubSpot and discover how to automate your consent management.
Tags
Related posts
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
The Impact of Cookie Banners on Your E-commerce - LGPD
Having a cookie banner on your brand's website has become indispensable for many. However, for e-commerce websites, it has practically become an obligation to have one. This is because this type of website has a technological composition in which cookies are a structural part. Login flow, items in the shopping cart, recommendation showcases, remarketing... Most of them rely on cookies.
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

Key Differences between LGPD and GDPR and the Impact on Internet Cookies
While both regulations share the goal of safeguarding individuals' rights regarding the processing of their personal data, there are some important differences between them. It is crucial to understand these distinctions and their implications, particularly in the context of internet cookies.
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.

Canada PIPEDA: Privacy Policy
How to write a PIPEDA privacy policy: what the ten principles require you to disclose, what to add for Quebec, and a checklist before you publish.

Global Privacy Control (GPC) Explained: What It Is and Who Has to Honor It
Global Privacy Control (GPC) is a browser opt-out signal. Learn how it works, which US states require you to honor it, and how to test your site.

What is Privacy by Design?
With it, all companies that collect personal data such as email, name, phone number, among others, must be attentive to its guidelines and obligations. With the arrival of new laws, some terms begin to stand out, one of them is Privacy by Design, learn more in this post.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Canada PIPEDA and Cookies: All You Need to Know
PIPEDA is Canada's federal private-sector privacy law. See when it reaches your website, what it requires for cookies, and how to prove consent.

How to Choose a CMP (Consent Management Platform)?
Using a CMP (Consent Management Platform) is a great way to make efforts to adapt to new privacy regulations like GDPR, LGPD, DPDPA, CCPA and more...
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.

LGPD for marketing | A practical guideline.
Every day, millions of users generate data on the web, which is used by companies around the globe to improve their offerings. Therefore, in 2018, a law was created to regulate the use of personal data by companies, and this directly impacts digital marketing. We're talking about LGPD.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
New Hampshire NHDPA and Cookies: All you need to know
Discover what the New Hampshire Privacy Act (NHDPA) means for your business. Learn about compliance steps, consumer rights, penalties, and how to simplify it all with AdOpt, a Google-certified CMP.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?
New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.

What are Terms of Use and their importance for the LGPD?
Ignoring Terms of Use and their significance within a website, particularly now with LGPD, is a common mistake that both consumers and website owners frequently commit.
Tenesse TIPA: Privacy Policy
Learn what your TIPA Privacy Policy must include to comply with the Tennessee Information Protection Act from consumer rights and targeted advertising disclosures to the NIST affirmative defense, appeal mechanisms, and how to keep your notice aligned with your operational program.

Canada PIPEDA: DSAR Privacy Portal
How to handle PIPEDA access requests (DSAR): the 30-day deadline, extensions, refusals, costs, Quebec portability and how to run a privacy portal.

Montana MTCDPA: Cookies Policy
Learn about how to apply Montana MTCDPA Cookies Policy in your site
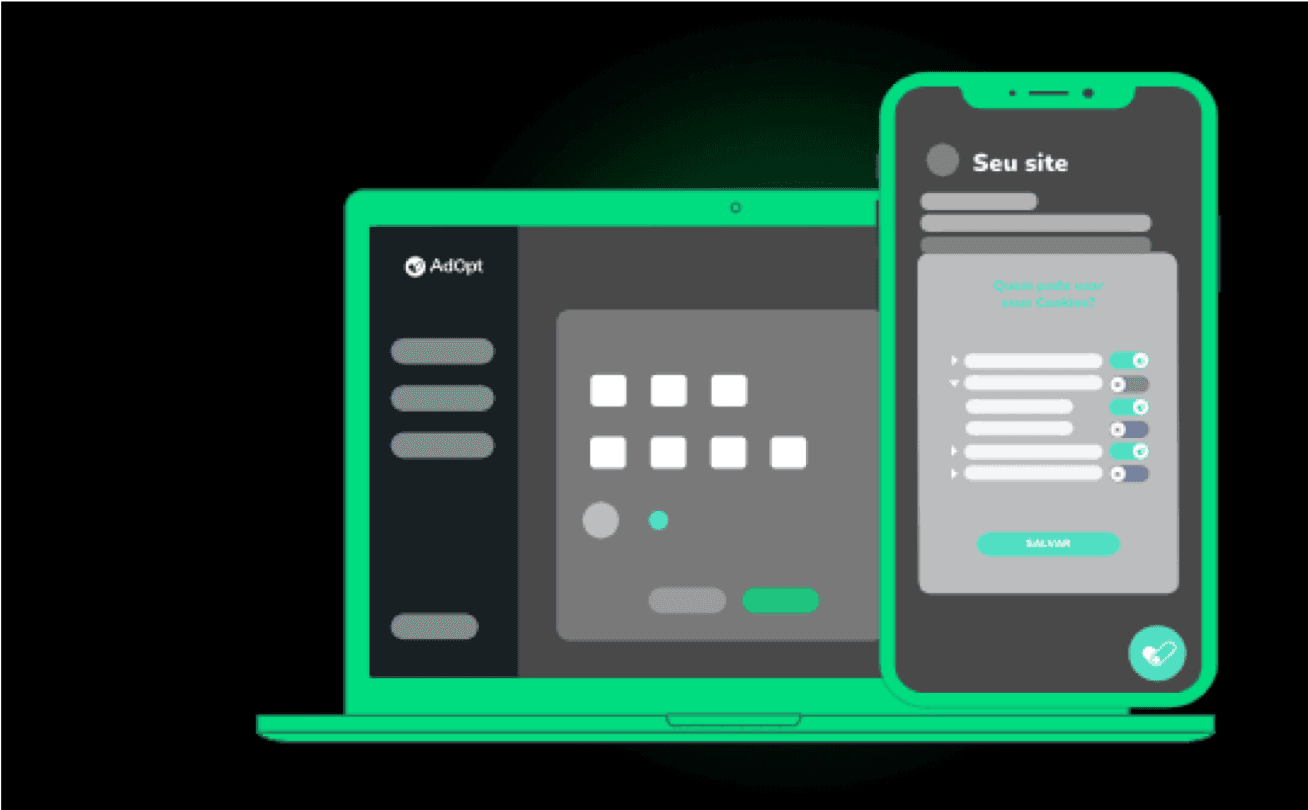
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.
Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
Tennessee TIPA and Cookies: All You Need to Know
If you're looking to understand how this law impacts businesses in Tennessee, especially those dealing with digital cookies, you're in the right place. This article will simplify the complexities of compliance and make them easy to grasp, even if you're just starting to learn about data privacy.

California CPRA and Cookies: All you need to know
California CPRA explained: CCPA vs CPRA timeline and key differences, sensitive personal information, sharing of data, CPPA enforcement, GPC requirement, and tripled penalties for minors.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
Explore AdOpt
Autor
João Bruno
04 Aug 2026
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Oregon OCPA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


