Virginia VCDPA: Cookies Policy
Every tool you install on your site places something on the visitor's device before any question is asked.
This page covers one piece of the picture. For the full scope of the VCDPA — who must comply, the thresholds, the consumer rights and the penalties — start with our complete guide to the VCDPA and cookies.
An advertising pixel starts tracking behavior as soon as the page loads. Google Analytics begins measuring sessions before the first click. A support chat already knows where the user came from before any message is sent.
The Virginia Consumer Data Protection Act (VCDPA, Va. Code § 59.1-575 et seq.), in effect since January 1, 2023, changed the relationship between these trackers and user consent.
This article focuses exclusively on what the VCDPA requires from a Cookies Policy: what the document must contain, how tracker consent must work, and what the law says about each specific point.
The cookie banner is the visual consent element. It is what the visitor sees when they first access the site. It must be clear, offer real options, and block non-essential trackers before they fire.
The Cookies Policy is the detailed document. It is where the user finds complete information about every technology operating on the site, its purposes, the data it collects, who receives it, and how long it is retained.
Both need to exist. Both need to be aligned. And the Cookies Policy must be accessible through a clear link within the consent notice itself.
Va. Code § 59.1-578 A, 2 prohibits processing data for purposes incompatible with those disclosed, except with new consent. And Va. Code § 59.1-578 C, 2 requires the purpose of processing to be included in the privacy notice.
For cookies, each category needs a purpose description specific enough for the consumer to understand what they are agreeing to.
What does not work: "we use cookies to improve your experience." That is not a purpose. It is a vague description that does not create compliance and does not protect the business.
What works:
"Analytics cookies: collect browsing behavior data, including pages visited, session duration, and traffic source. Used to identify opportunities to improve site content and user experience."
"Advertising cookies: collect behavioral data across non-affiliated websites over time to build interest profiles and display personalized ads on other platforms. Include pixels from platforms such as Meta Ads, Google Ads, and TikTok."
The Policy must list the categories of trackers operating on the site. The main ones:
Necessary cookies: essential for basic functionality. Authentication, session security, shopping cart. These do not require consent but must be documented.
Analytics cookies: measure browsing behavior. Google Analytics, Hotjar, Clarity, and similar tools. These require consent in most cases because they collect data that may identify users through cross-referencing.
Advertising cookies: feed ad pixels, build behavioral profiles, enable remarketing. These always require explicit consent and, if used for targeted advertising as defined by the VCDPA, require specific disclosure and an opt-out.
Functional cookies: remember user preferences, such as selected language or recently viewed items. May or may not require consent depending on the nature of the data retained.
Third-party cookies: fired by external services integrated into the site. Correct tag categorization is what makes it possible to document each one accurately and keep the inventory up to date.
The VCDPA has a requirement that goes beyond the general privacy notice. Va. Code § 59.1-578 D requires that if the business processes data for targeted advertising, it must disclose this clearly and conspicuously, with the opt-out mechanism accessible.
Targeted advertising, under Va. Code § 59.1-575, consists of ads based on data collected from the consumer's activities over time and across non-affiliated websites or applications. This covers any retargeting pixel, custom audience in ad platforms, or any technology that carries data from your site to an external advertising network.
What does not constitute targeted advertising under the VCDPA:
Ads based on activities within the controller's own websites or applications.
Contextual ads based on the consumer's current search query or current site visit.
Ads directed to a consumer in response to their request for information.
Data processed solely for measuring advertising performance, reach, or frequency.
If your site has any pixel that sends data to an external advertising network, you are operating targeted advertising under the VCDPA definition. The Cookies Policy must explicitly state this and the opt-out must work.
Va. Code § 59.1-578 C, 4 and 5 require the privacy notice to disclose which categories of data are shared with third parties and which categories of third parties receive them.
For cookies, this translates into clearly declaring:
If a Meta Pixel transfers behavioral data to Meta, it must be documented.
If Google Analytics sends session data to Google, it must be stated.
If CRM tools receive form submission data from the site, they must be identified.
Every data flow leaving the controller's environment must be categorized and described.
Va. Code § 59.1-578 A, 1 requires that collection be limited to what is adequate, relevant, and reasonably necessary for the declared purposes. The minimization principle implies the need to disclose how long data is stored.
For the Cookies Policy, this means documenting:
How long each cookie category remains active on the user's device.
How long data collected via cookies is retained in the business's systems.
When and how data is deleted after the retention period.
The VCDPA guarantees consumers the right to opt out of the processing of their data for targeted advertising, under Va. Code § 59.1-577 A, 5.
Va. Code § 59.1-578 D requires that the disclosure of targeted advertising come with the opt-out mechanism. The Cookies Policy must describe how the consumer can exercise this opt-out and the link must be accessible.
A well-configured consent management platform ensures that when the user opts out of targeted advertising, all corresponding pixels and trackers stop firing automatically.
Va. Code § 59.1-575 defines consent as a clear affirmative act signifying a consumer's freely given, specific, informed, and unambiguous agreement. This may include a written statement, including by electronic means, or any other unambiguous affirmative action.
The correct standard for cookies: non-essential technologies off by default. The user chooses what to enable, not what to disable.
Accepting general terms of use that contain data processing descriptions mixed with other conditions.
Continuing to browse the site without any explicit action.
Interfaces that use design to make opting out harder than accepting.
Banners that reappear until the user accepts.
Cookie walls that block access to content until all cookies are accepted.
The VCDPA does not use the term "dark patterns" explicitly as the NHDPA does, but the principle of free, specific, informed, and unambiguous consent renders the same manipulative design patterns invalid.
In most cases, yes.
The VCDPA defines personal data as any information linked or reasonably linkable to an individual. Analytics cookies from major platforms collect identifiers that, when cross-referenced with other data the provider holds, can identify a specific user.
The safest approach: treat analytics cookies as non-necessary in the banner, block them before acceptance, and document this categorization in the Cookies Policy.
Va. Code § 59.1-578 F establishes specific protections for known children under 13:
Prohibition on processing for targeted advertising, data sale, and profiling with significant effects.
Processing only when reasonably necessary to provide the online service, product, or feature.
No use of data for purposes beyond those disclosed at collection.
Retention only for the time necessary to provide the service.
For social media platforms, protection extends to minors under 16 starting January 2026 (Va. Code § 59.1-577.1), with a 1-hour daily usage limit.
If your site may have users under 13, the Cookies Policy must describe how their data is treated differently.
Whenever the site begins using a new tool that fires cookies or trackers. The technology inventory of the site must stay synchronized with the document.
Situations that require an update:
Adding a new advertising pixel.
A new analytics or heatmap tool.
A new chat, support, or engagement plugin.
A new CRM or email marketing platform integration.
Any new partner that receives behavioral data from site users.
Continuous data mapping is what maintains this synchronization. When the technology inventory changes, the Cookies Policy must change with it.
The Attorney General must provide a guaranteed 30-day cure period before initiating any action (Va. Code § 59.1-584 B). An inadequate Cookies Policy can be corrected within that period if the business has its processes structured.
However, if the violation continues or the business breaches the correction statement provided, penalties can reach US$ 7,500 per violation, with each affected consumer potentially constituting a separate violation.
AdOpt's automatic scan identifies all technologies active on the site, feeding the list of categories that must appear in the Cookies Policy.
The cookie notice configured through AdOpt blocks non-essential trackers before acceptance, presents categories with clear descriptions, offers real choice options, and logs every interaction for audit purposes.
The integration with the business's systems ensures that targeted advertising opt-outs are processed automatically.
Over 60,000 websites already run with AdOpt.
Privacy is not a banner. It is a position.
Want to build a Cookies Policy for your site that complies with the VCDPA? Talk to our team.
Visible link in the site footer and within the cookie banner itself.
Listing of cookie categories with a description of what each one does on the site.
Specific purpose for each category, without vague descriptions (Va. Code § 59.1-578 C, 2).
Clear and conspicuous disclosure of targeted advertising with an accessible opt-out mechanism (Va. Code § 59.1-578 D).
Categories of data shared with third parties via cookies (Va. Code § 59.1-578 C, 4).
Categories of third parties that receive data via cookies (Va. Code § 59.1-578 C, 5).
Retention period for each cookie category.
Non-essential cookies disabled by default in the banner, without manipulative design patterns.
Protection for data of known children under 13 with a differentiated flow (Va. Code § 59.1-578 F).
Protection for minors under 16 on social media platforms where applicable (Va. Code § 59.1-577.1, effective Jan 2026).
Accessible language, without legal jargon.
No cookie walls.
1. Does the VCDPA require a separate document called a "Cookies Policy"?
Not by name. The disclosure requirements for trackers are distributed between the privacy notice (Va. Code § 59.1-578 C) and the targeted advertising disclosure requirement (Va. Code § 59.1-578 D). A dedicated Cookies Policy is the most organized way to meet all of these requirements in a user-accessible format.
2. Do analytics cookies always require consent under the VCDPA?
In most cases, yes. Analytics cookies from major platforms collect data that may identify users through cross-referencing with other information the provider holds, falling within the definition of personal data in Va. Code § 59.1-575. Tools with genuine anonymization and no technical re-identification capability may be an exception. The safest approach is to treat them as non-necessary in the banner.
3. How quickly must the opt-out of targeted advertising be processed?
The VCDPA does not specify a separate cessation deadline after opt-out, unlike the NHDPA which has a specific 15-day period. In the VCDPA, the criterion is "without undue delay" for the general response, with a maximum of 45 days (Va. Code § 59.1-577 B, 1). In practice, for targeted advertising opt-outs, the expectation is that cessation is processed with the greatest technically reasonable agility.
4. Does a third-party advertising pixel constitute "sale of data" under the VCDPA?
It depends on the structure. The VCDPA defines sale as the exchange of data for monetary consideration. If the pixel sends data to an ad platform and in return the business receives paid advertising services, there are divergent legal positions on whether this constitutes a sale. The safest approach is to treat it as targeted advertising (which also requires opt-out) and disclose explicitly in the Cookies Policy.
5. What changes for social media platforms starting January 2026?
Va. Code § 59.1-577.1 comes into effect on January 1, 2026 and requires social media platforms to determine if users are under 16, limit their use to 1 hour per day, and allow parents to adjust this limit through verifiable parental consent. The Cookies Policy must describe how age identification data is collected and used solely for that purpose, without application to other processing activities.
Ready to build a Cookies Policy for your site that complies with the VCDPA? Talk to our team.
Virginia VCDPA compliance rests on documents that need to agree with each other: the privacy policy, which explains what you do with the data; the privacy portal, which is where the consumer exercises their rights and you keep the record of it.
Tags
Related posts
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.
Data Mapping or Data Inventory - a life jacket for the DPO!
With the data mapping we have a clear understanding of the 5 stages that every data goes through in a company.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.
GDPR Legal Basis: An Introduction
In this article, we'll explore the GDPR foundations and provide practical insights from the basics to more advanced concepts of its legal basis.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.
The Impact of Cookie Banners on Your E-commerce - LGPD
Having a cookie banner on your brand's website has become indispensable for many. However, for e-commerce websites, it has practically become an obligation to have one. This is because this type of website has a technological composition in which cookies are a structural part. Login flow, items in the shopping cart, recommendation showcases, remarketing... Most of them rely on cookies.
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.
Google Consent Mode: Beginner to Advanced Guide.
Google Consent Mode (GCM) is nothing more than a way for you to integrate the consent you collect from your visitors into Google technologies. In this way, upon receiving this consent information, collection can only occur with authorization, thus complying with the legislation and having direct evidence of compliance as defense for both you and Google.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

Everything about the Brazilian LGPD - General Data Protection Law.
All the important information about the General Data Protection Law - LGPD: what it is, why it exists, how it works, when it came into force, who it applies to, potential fines, steps for compliance, and its legal principles.

IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

How to Choose a CMP (Consent Management Platform)?
Using a CMP (Consent Management Platform) is a great way to make efforts to adapt to new privacy regulations like GDPR, LGPD, DPDPA, CCPA and more...
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Outsourcing the DPO (DPOaaS), Is It a Good Idea?
The Data Protection Officer, or DPO, is a new position that emerged all over the globe with the new privacy regulations, and more recently at the LGPD. Although it already existed in other international legislations, such as the EU's GDPR, it is still a novelty here since 2020. Along with it comes the possibility of outsourcing, known as DPO as a Service (DPOaaS).
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
What is the difference between cookies, local storage, and session storage?
Despite cookies being more well-known, what is the main difference between cookies and session storage and local storage? Why choose one over the other? This article will help you with these doubts!
Florida FDBR: Privacy Policy
What the Florida FDBR requires from your Privacy Policy: annual updates, 6 mandatory content categories, specific notices for sensitive and biometric data sales, and the 7 consumer rights.
ROPA in LGPD? Get to Know the Records of Processing Activities.
Brazilian LGPD - General Data Protection Law brought with it several acronyms and specific terms. Many of them are imported from other countries and regulations. One of them is ROPA (Record Of Processing Activities), adapted in Brazil to Registros das Atividades de Tratamento. An essential document for any DPO, Data Processor.

The Differences Between Data Controller and Data Processor - LGPD
Now that we have the data flow within your company, we need to highlight 2 aspects of LGPD that will help you determine the extent of your responsibility in relation to the many points listed in the company. I'm talking about the difference between Data Controller and Data Processor.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Understand the meaning of the LGPD for your company
Surely you've already seen the predictions of fines and sanctions, processes. But, what does it mean to your company?
New Hampshire NHDPA and Cookies: All you need to know
Discover what the New Hampshire Privacy Act (NHDPA) means for your business. Learn about compliance steps, consumer rights, penalties, and how to simplify it all with AdOpt, a Google-certified CMP.
What is a privacy policy?
A privacy policy is a document that outlines how an organization collects, uses, discloses, and manages a customer's data. It's essential for building trust with users and complying with legal requirements. However, if you're not familiar with it, don't worry as we're here to help you.

How long can we ignore LGPD?
LGPD is in effect. Despite that, there are still many companies ignoring it, but is that possible? How long can we ignore LGPD?
New Hampshire NHDPA: Privacy Policy
Learn what your Privacy Policy must contain under the NHDPA. We break down the 8 mandatory elements and how to comply with New Hampshire's data privacy law.

What are Terms of Use and their importance for the LGPD?
Ignoring Terms of Use and their significance within a website, particularly now with LGPD, is a common mistake that both consumers and website owners frequently commit.
Tenesse TIPA: Privacy Policy
Learn what your TIPA Privacy Policy must include to comply with the Tennessee Information Protection Act from consumer rights and targeted advertising disclosures to the NIST affirmative defense, appeal mechanisms, and how to keep your notice aligned with your operational program.

Montana MTCDPA: Cookies Policy
Learn about how to apply Montana MTCDPA Cookies Policy in your site
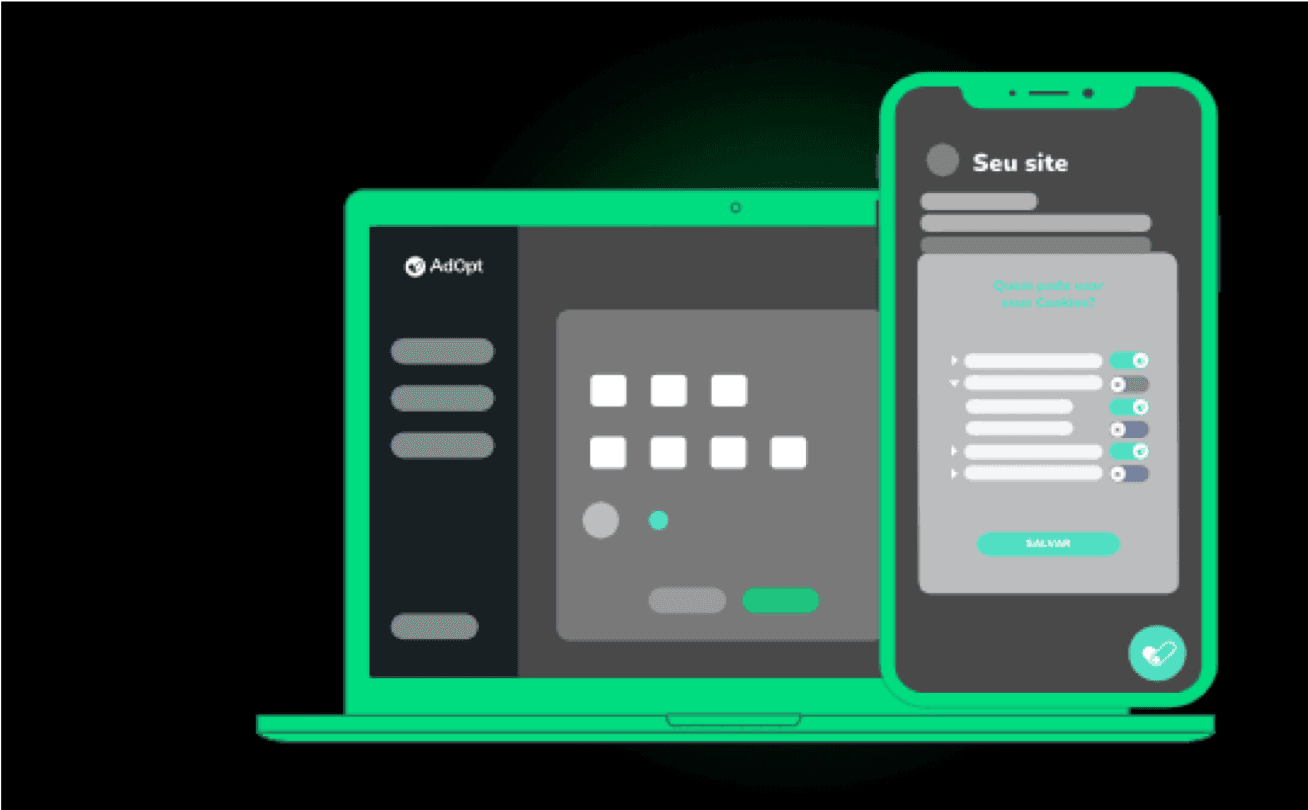
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.

Virginia VCDPA: DSAR Privacy Portal
How to handle DSARs under the Virginia VCDPA: consumer rights, 45-day response deadlines, the appeal process, free requests twice per year, and how to build a compliant Privacy Portal.
Tennessee TIPA and Cookies: All You Need to Know
If you're looking to understand how this law impacts businesses in Tennessee, especially those dealing with digital cookies, you're in the right place. This article will simplify the complexities of compliance and make them easy to grasp, even if you're just starting to learn about data privacy.

California CPRA and Cookies: All you need to know
California CPRA explained: CCPA vs CPRA timeline and key differences, sensitive personal information, sharing of data, CPPA enforcement, GPC requirement, and tripled penalties for minors.

Google Analytics 4 Cookie Consent: What Changes in Your Data and How to Set It Up
Google Analytics 4 cookie consent explained: what GA4 does when a visitor says no, what changes in your reports, and how to check your setup.

GDPR, LGPD, and CCPA: What Are These Laws, Similarities, and Differences
LGPD, GDPR, and CCPA are data privacy regulations. In this article, we discuss their similarities and differences for practical application.
California CPRA: DSAR and Privacy Portal
California CPRA DSAR guide: new rights to correct and limit SPI, opt-out without multiple steps, GPC as valid opt-out, 12-month minor rule, private right of action, and CPPA enforcement.
Oregon OCPA: DSAR Privacy Portal
Oregon OCPA DSAR guide: the L.O.C.K.E.D. rights, opt-out without authentication, derived data in deletion scope, 15-day revocation deadline, GPC from January 2026, and the elimination of the cure period.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Axeptio acquires Brazil's AdOpt, expanding global reach in consent management and LGPD compliance.
Florida FDBR and Cookies: All You Need to Know
Everything you need to know about the Florida Digital Bill of Rights (FDBR): who must comply, the $1 billion threshold, 7 consumer rights, FIPA vs FDBR explained, penalties, and cookies.
Explore AdOpt
Autor
João Bruno
26 May 2026
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Oregon OCPA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


