The Iowa Consumer Data Protection Act (ICDPA, Iowa Code § 715D) has privacy notice requirements very similar to Utah's UCPA, with one important operational difference: the response deadline for consumer requests is 90 days, not 45.
This page covers one piece of the picture. For the full scope of the ICDPA — who must comply, the thresholds, the consumer rights and the penalties — start with our complete guide to the ICDPA and cookies.
For the Privacy Policy, this means the process described in the document for exercising rights must reflect this longer deadline. Iowa consumers will have to wait up to three months to receive a response, and the notice must be clear about this.
This article focuses exclusively on what the ICDPA requires from the Privacy Policy.
The law uses the term "privacy notice." Under § 715D.4(5), the controller must provide a notice that is "reasonably accessible, clear, and meaningful."
The notice must list the categories of personal data the controller processes (§ 715D.4(5)(a)).
Personal data under the ICDPA is any information linked or reasonably linkable to an identified or identifiable natural person (§ 715D.1(18)). This includes identifiers such as name, email, IP address, browsing history, and data that allows tracking a person.
De-identified data, aggregate data, and publicly available information are excluded.
The notice must explain the purpose for which data is processed (§ 715D.4(5)(b)).
The law does not specify that purposes must be highly detailed, but the requirement that the notice be "clear and meaningful" implies that generalities like "improve services" are insufficient.
The notice must describe how consumers can exercise the rights guaranteed by the ICDPA, including how to appeal a controller decision (§ 715D.4(5)(c)).
The four rights under the ICDPA are:
Confirm and access: confirm whether the controller processes data and access that data (§ 715D.3(1)(a)).
Deletion: request deletion of data the consumer provided to the controller (§ 715D.3(1)(b)).
Portability: obtain a copy of the data in a portable format (§ 715D.3(1)(c)).
Opt-out from data sales: refuse the sale of personal data (§ 715D.3(1)(d)).
The deadline that must be described: 90 days to respond from receipt of the request, with a possible extension of 45 more days with notification within the initial period (§ 715D.3(2)(a)).
The appeal process: the notice must describe how the consumer can appeal a denial decision, with a 60-day response deadline for appeals (§ 715D.3(3)). If the appeal is denied, the consumer must be informed of how to contact the Attorney General online.
The notice must identify the categories of personal data the controller shares with third parties, if any (§ 715D.4(5)(d)).
The notice must identify the categories of third parties with whom data is shared, if any (§ 715D.4(5)(e)).
The ICDPA does not require the level of detail about how each third party may process data that the OCPA demands. Identifiable categories are sufficient.
If the business sells data or engages in targeted advertising, § 715D.4(6) requires clear and conspicuous disclosure of that activity, with description of the method by which the consumer can exercise the opt-out for each activity.
Targeted advertising, per § 715D.1(28), consists of ads selected based on data obtained from the consumer's activities over time and across non-affiliated websites or applications.
Although opt-out from targeted advertising is not listed as a formal right in § 715D.3, the disclosure obligation in § 715D.4(6) creates the practical requirement to offer this opt-out in the privacy notice.
Under § 715D.4(7), the controller must establish secure and reliable means for consumers to submit rights requests, and describe those means in the privacy notice.
These means must:
Consider how consumers normally interact with the controller.
Ensure secure and reliable communication.
Allow authentication of the consumer's identity.
The controller may not require the consumer to create a new account to exercise their rights. It may require use of an existing account (§ 715D.4(7)).
Under § 715D.4(2), the controller may not process sensitive data without first presenting the consumer with a clear notice and offering an opt-out opportunity.
Sensitive data includes: racial or ethnic origin, religious beliefs, mental or physical health diagnosis, sexual orientation, citizenship or immigration status, genetic or biometric data for unique identification, data of known children, and precise geolocation data.
This opt-out model for sensitive data is identical to the UCPA's. It is less restrictive than the opt-in required by the CPRA, OCPA, VCDPA, and CTDPA.
For data of known children, the business must comply with COPPA (§ 715D.2(2)(r) and 715D.4(2)).
The Privacy Policy must:
Identify whether the business processes sensitive data.
Describe how the sensitive data notice is presented to consumers.
Explain how the consumer can exercise the opt-out from sensitive data processing.
Comparing with other laws:
No mandatory retention periods. The CPRA requires specifying how long each data category is retained. The ICDPA has no such requirement.
No detail about third parties. The OCPA requires describing how each third party may process data. The ICDPA requires only categories.
No right to correct to describe. Since the ICDPA does not provide this right, the policy does not need to describe it.
The 90-day deadline must be clearly described. Consumers familiar with VCDPA, OCPA, and CTDPA expect responses within 45 days. A notice that clearly states the ICDPA's 90-day deadline avoids unnecessary complaints.
Under § 715D.4(3), the business may not discriminate against consumers who exercise their rights. This includes denying goods or services, charging different prices, or offering different quality.
The exception is voluntary loyalty programs and situations where the consumer opted out of targeted advertising and the business adjusted prices accordingly.
Before initiating any action, the Iowa Attorney General must notify the controller and grant 90 days to cure (§ 715D.8(2)). This is the longest cure period of all US state privacy laws.
An outdated or incomplete Privacy Policy can be corrected within 90 days with the right processes. But structuring it correctly from the start is always more efficient.
AdOpt ensures that what is written in the Policy has real correspondence with what actually happens on the site.
The automatic scan identifies all active technologies, feeding the list of data categories and third parties. The consent management platform ensures the opt-out mechanism works as described.
Every interaction is logged. If the Attorney General requests evidence, the record is available.
Over 60,000 websites already run with AdOpt.
Privacy is not a banner. It is a position.
Want to build a Privacy Policy for your site that complies with the ICDPA? Talk to our team.
Visible and accessible link on all pages of the site.
Categories of personal data processed (§ 715D.4(5)(a)).
Purpose for processing each category (§ 715D.4(5)(b)).
How to exercise the 4 rights with channel and 90-day deadline (§ 715D.4(5)(c)).
Appeal process with 60-day response deadline (§ 715D.3(3)).
How to contact the Attorney General if appeal is denied (§ 715D.3(3)).
Categories of personal data shared with third parties (§ 715D.4(5)(d)).
Categories of third parties with whom data is shared (§ 715D.4(5)(e)).
Disclosure of data sales or targeted advertising with opt-out method (§ 715D.4(6)).
Request submission channel described, without requiring new account (§ 715D.4(7)).
Sensitive data treatment: clear notice and opt-out before processing (§ 715D.4(2)).
COPPA compliance for children's data (§ 715D.4(2)).
Non-discrimination policy (§ 715D.4(3)).
Free service for 2 requests per year per consumer (§ 715D.3(2)(c)).
1. Why must the ICDPA Privacy Policy clearly state the 90-day deadline?
Most consumers who have interacted with privacy notices from other jurisdictions expect responses within 45 days. The ICDPA establishes 90 days as the standard deadline (§ 715D.3(2)(a)), which is significantly different. A Policy that clearly describes this deadline helps manage expectations and avoids complaints from consumers expecting a faster response. Describing the correct deadline also demonstrates that the business knows its specific legal obligations.
2. Does the privacy notice need to mention the ICDPA's appeal process?
Yes. § 715D.4(5)(c) requires the notice to describe how consumers can exercise their rights "including how a consumer may appeal a controller's decision with regard to the consumer's request." This means the appeal process, with a 60-day response deadline (§ 715D.3(3)), must be described. If the appeal is denied, the notice should also indicate how the consumer can contact the Attorney General.
3. Does the ICDPA have the same free-service policy as the UCPA?
Not exactly. The ICDPA guarantees free service for 2 requests per consumer per 12-month period (§ 715D.3(2)(c)). The UCPA guarantees free service for only 1 request per 12-month period. The VCDPA also guarantees 2 free requests per year. The Privacy Policy must correctly reflect this number, as stating "free once per year" when the law guarantees 2 would be an inaccuracy that could generate complaints.
4. Does the ICDPA use the same opt-out model for sensitive data as the UCPA?
Yes. Both the ICDPA (§ 715D.4(2)) and the UCPA require only a clear notice and opt-out opportunity before processing sensitive data, without requiring active prior consent. This model differs from the opt-in required by the CPRA, OCPA, VCDPA, and CTDPA. A business already compliant with the UCPA on this point will be compliant with the ICDPA as well.
5. Does the ICDPA require the same level of detail about third parties as the OCPA?
No. The OCPA requires describing third parties at a level of detail that enables the consumer to understand what type of entity each third party is and how it may process data. The ICDPA (§ 715D.4(5)(d) and (e)) requires only the categories of data shared and the categories of third parties, without the additional detail the OCPA demands. Categories such as "digital advertising platforms" and "analytics tools" are sufficient under the ICDPA.
Ready to build a Privacy Policy for your site that complies with the ICDPA? Talk to our team.
Iowa ICDPA compliance rests on documents that need to agree with each other: the cookies policy, which declares every tracker and its purpose; the privacy portal, which is where the consumer exercises their rights and you keep the record of it.
Tags
Related posts
Florida FDBR and Cookies: All You Need to Know
Everything you need to know about the Florida Digital Bill of Rights (FDBR): who must comply, the $1 billion threshold, 7 consumer rights, FIPA vs FDBR explained, penalties, and cookies.
GDPR and Cookies all you need to know
Understanding the General Data Protection Regulation (GDPR) and its impact on cookies is essential. So, let's break it down, step by step.

IOWA ICDPA and Cookies: All you need to Know
Iowa ICDPA explained: the longest response deadline of all US state privacy laws (90 days), 90-day cure period, opt-out for sensitive data, limited deletion scope, no right to correct, and how it compares to UCPA, VCDPA, and OCPA.
Tenesse TIPA: DSAR Privacy Portal
Learn how to build a TIPA-compliant Privacy Portal for Tennessee. Understand DSAR deadlines, consumer rights, opt-out mechanisms, and the affirmative defense that sets TIPA apart from every other US state privacy law.
Colorado CPA: Cookies Policy
What the Colorado CPA requires from your Cookies Policy: mandatory Universal Opt-Out Mechanism from July 2024, targeted advertising definition, dark pattern rules, and the 24-month consent refresh.

Why are cookie banners everywhere?
Want to understand why there are cookie banners on every website you visit today? This article is for you!

Montana MTCDPA: Privacy Policy
Learn what your MTCDPA Privacy Policy must include after Montana's SB 297 amendments from the conspicuous "privacy" hyperlink and last-updated date requirements to sale disclosures, minor protections, and how to keep your notice operationally aligned with your stack.
Utah UCPA and Cookies: All you need to know
Utah UCPA explained: the most business-friendly US state privacy law, dual threshold requirement, opt-out for sensitive data, no right to correct, guaranteed 30-day cure period, and key differences from other state laws.

Cookies and the TDPSA
If your website uses cookies and serves users in Texas, the Texas Data Privacy and Security Act (TDPSA) applies to you. This article breaks down exactly how cookies are treated under the law—and what your business must do to remain compliant and build user trust.
Texas TDPSA and Cookies: All You Need to Know
Your website have users accessing from Texas? So be ready… the Texas Data Privacy and Security Act is here to shake things up. Don't worry; we've got your back. This guide will walk you through everything you need to know to ensure your website complies with the new regulations.

California CCPA: Privacy Policy
What the California CCPA/CPRA requires from your Privacy Policy: 12-month lookback, annual updates, Do Not Sell link, sensitive PI disclosures, toll-free number, and the 7 consumer rights.

Virginia VCDPA: Cookies Policy
What the Virginia VCDPA requires from your Cookies Policy: targeted advertising disclosure, consent standards, tracker categories, opt-out mechanisms, and the 30-day cure period explained.

Connecticut CTDPA: DSAR Privacy Portal
How to handle DSARs under the Connecticut CTDPA: 5 consumer rights, opt-outs without mandatory authentication, 60-day appeal deadline, 15-day consent revocation, and AG-only enforcement.

What is the ideal privacy policy for your company?
Is there an ideal and _foolproof_ Privacy Policy? This is one of the most difficult questions to answer nowadays. Especially considering all the jurisprudence already established in Europe with the GDPR, the extensive history of cases, and the numerous tips we see in the market. Not to mention the judicial decisions that are already emerging in Brazil with the LGPD.

Cross-Domain Cookie Consent: One Choice, Several Sites
Cross-domain cookie consent lets one visitor choice apply to several sites. See when sharing is valid, how tags read it and what to test before you launch.
Colorado CPA and Cookies: All You Need to Know
The Colorado Consumer Privacy Act went into effect July 1, 2023 (CPA). CPA is a vital piece of legislation designed to protect the privacy of residents in Colorado. Understanding its requirements is essential for any business operating in the state. This act is all about giving control back to the consumers regarding their personal data. But what does this mean for you and your business, especially when it comes to managing cookies on your website?
Oregon OCPA and Cookies: All You Need to Know
Everything about the Oregon OCPA: who must comply, the payment transaction exclusion, 25% revenue threshold, derived data in scope, GPC requirement from January 2026, and elimination of the cure period.

Canada PIPEDA: Privacy Policy
How to write a PIPEDA privacy policy: what the ten principles require you to disclose, what to add for Quebec, and a checklist before you publish.

Best practices in tag categorization
It's time to talk about one of the most impactful tasks, both for the company and for the visitors of your websites: tag categorization. But why is it so impactful? What is the relevance of this configuration and how can it affect us? It is precisely because of these common questions we receive from our clients that we have written this article on best practices in tag categorization.

Global Privacy Control (GPC) Explained: What It Is and Who Has to Honor It
Global Privacy Control (GPC) is a browser opt-out signal. Learn how it works, which US states require you to honor it, and how to test your site.

5 Signs Your Website Needs an Cookie Consent Strategy
How does your website handle LGPD? What strategies does it use to comply with the General Data Protection Law? Have you thought about using a cookie notice but don't know if your site has cookies or if it's enough? If you can't answer these questions, be cautious! Your page may be exposed to fines and other sanctions.
California CCPA and Cookies: All You Need to Know
Everything about the California CCPA and CPRA: who must comply, the $25M threshold, 7 consumer rights, CCPA vs CPRA explained, the Do Not Sell link, CPPA enforcement, and cookies.
IOWA ICDPA: DSAR and Privacy Portal
Iowa ICDPA DSAR guide: 90-day response deadline, 45-day extension, 60-day appeal process, limited deletion scope, opt-out from data sales, targeted advertising disclosure requirement, and 90-day cure period.
LGPD: An Opportunity for Digital Marketing Agencies!
Have you ever thought that your marketing agency could find a great business opportunity in LGPD? Well, unlike what many think, it brings changes that can accelerate the demand for the services of these companies.
How does a cookie banner operate?
Here is a step-by-step explanation of how consent registration works in AdOpt.
Oregon OCPA: Cookies Policy
What the Oregon OCPA requires from your Cookies Policy: opt-out link, GPC from January 2026, opt-out without authentication, derived data in scope, teen protections, and the elimination of the cure period.
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Axeptio acquires Brazil's AdOpt, expanding global reach in consent management and LGPD compliance.
Oregon OCPA: Privacy Policy
What the Oregon OCPA requires from your Privacy Policy: actively monitored contact channel, detailed third-party descriptions, derived data in scope, GPC from January 2026, and the elimination of the cure period.

Consent Management Across Countries: How One CMP Serves Every Market
Consent management across countries: how one CMP applies the right rules to each visitor, passes the choice to Google and Meta, and honors GPC.

Texas TDPSA: Privacy Policy
The Texas Data Privacy and Security Act (TDPSA) introduces sweeping changes to how businesses collect, use, and disclose personal data—and your privacy policy is now a frontline compliance tool. This article is a comprehensive guide for any company serving Texas residents, explaining how to align your privacy practices with the new legal standards.
Montana MTCDPA: DSAR Policy
Rights, Policy and how to understand about the DSAR Montana MTCDPA
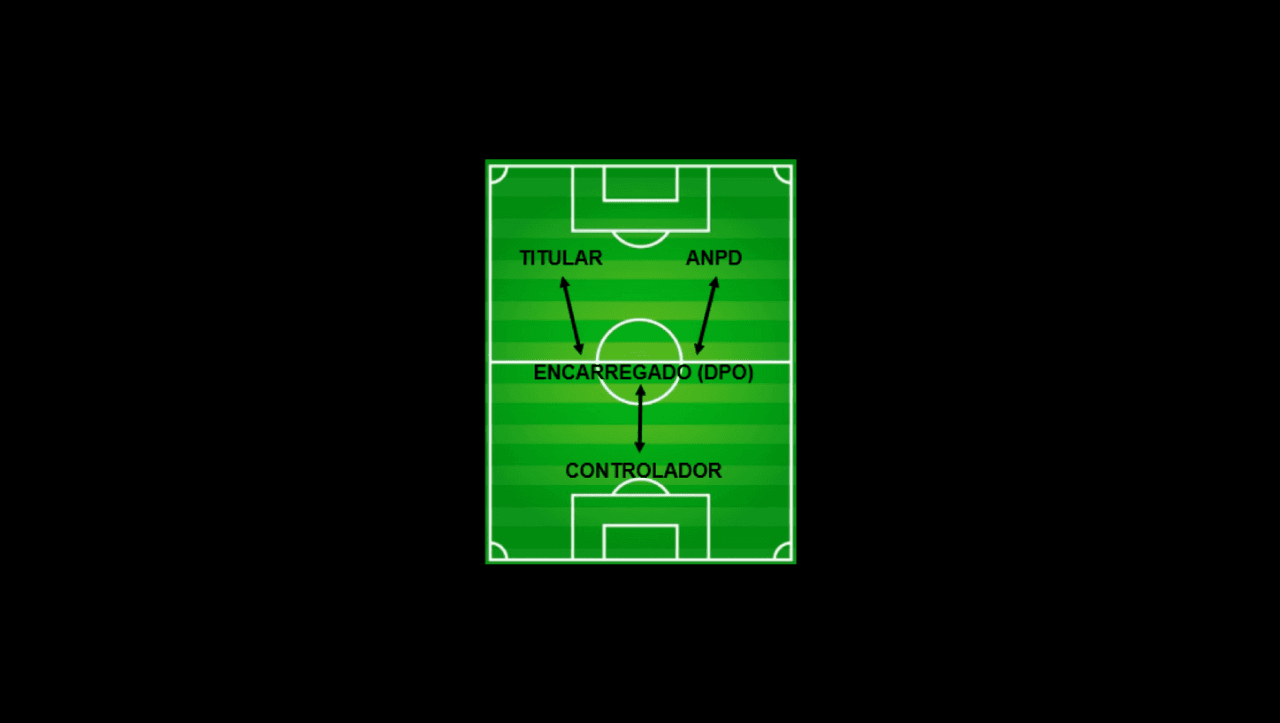
Responsibilities of a data protection officer.
Drawing an analogy from the world of soccer, we can think of the DPO as the "midfielder" of the team, responsible for connecting the defense and the attack.
IOWA ICDPA: Cookies Policy
What the Iowa ICDPA requires from your Cookies Policy: opt-out for data sales and targeted advertising, opt-out model for sensitive data, no GPC requirement, no specific link text required, and the 90-day cure period.

Utah UCPA: Privacy Policy
What the Utah UCPA requires from your Privacy Policy: five mandatory elements, opt-out model for sensitive data, no retention periods required, no active contact channel mandate, and the guaranteed 30-day cure period.

Canada PIPEDA and Cookies: All You Need to Know
PIPEDA is Canada's federal private-sector privacy law. See when it reaches your website, what it requires for cookies, and how to prove consent.

How to Choose a CMP (Consent Management Platform)?
Using a CMP (Consent Management Platform) is a great way to make efforts to adapt to new privacy regulations like GDPR, LGPD, DPDPA, CCPA and more...
Florida FDBR: Cookies Policy
What the Florida FDBR requires from your Cookies Policy: targeted advertising across affiliated sites, opt-out for sensitive data and voice recognition, dark patterns, and tripled penalties.
Connecticut CTDPA and Cookies: All You Need to Know
The Connecticut Data Privacy Act (CTDPA) is a state regulation designed to protect the privacy of Connecticut residents. It also regards cookies, so in this article we will help you understand all about this new privacy regulation.
Florida FDBR: DSAR Privacy Portal
How to handle DSARs under the Florida FDBR: 7 consumer rights, two required submission channels, 45-day deadline with only 15-day extension, tripled penalties for children, and compliance guide.

Canada PIPEDA: Cookies Policy
What a PIPEDA cookie policy must say: purposes, third parties, opt-out, retention and Quebec rules. Plus a checklist to write yours.
California CCPA: DSAR Privacy Portal
How to handle DSARs under the California CCPA/CPRA: 7 consumer rights, 45-day deadline, toll-free number required, 12-month lookback, private right of action for breaches, and CPPA enforcement.

New Hampshire NHDPA: DSAR Privacy Portal
What is a DSAR under NHDPA? Complete guide to consumer rights, response deadlines, and building a compliant Privacy Portal for your site.
Connecticut CTDPA: Privacy Policy
What the Connecticut CTDPA requires from your Privacy Policy: active email contact, opt-out link, 15-day consent revocation, opt-out preference signal from January 2025, and teen protections.

5 Common Cookie Consent Mistakes Hurting Your Compliance
Discover the 5 common **cookie consent mistakes** that risk your **compliance** and learn how to avoid heavy **fines**. Simplify your **data privacy** strategy using a reliable **[Cookie notice/banner](https://goadopt.io/en/blog/why-the-cookie-banner/)**.
How to choose a Cookie Banner for your website
What are the criteria for this choice, and what are the strengths and weaknesses of each option? Well, we're here to help you because this decision needs to be well thought out!
Explore AdOpt
Autor
João Bruno
09 Jun 2026
AdOpt

Relevant posts
What is a privacy policy?
Colorado CPA and Cookies: All You Need to Know
Tennessee TIPA and Cookies: All You Need to Know
Florida FDBR and Cookies: All You Need to Know
Texas TDPSA and Cookies: All You Need to Know
Axeptio Strengthens its International Expansion with the Acquisition of AdOpt
Oregon OCPA and Cookies: All You Need to Know
Google Consent Mode: Beginner to Advanced Guide.
Utah UCPA and Cookies: All you need to know
How to choose a Cookie Banner for your website
Address: 7345 W Sand Lake Road, Ste 210 Office 5898 Orlando, FL 32819
15 Rue du Général Campredon, 34000 Montpellier, France
207 Rue de Bercy, 75012 Paris, France
EIN: 86-3965064
Phone: +1 (407) 768-3792
AdOpt
Resources
Product
Certifications


